

issame
New Member
June 12, 2020
Solved

subnet don't much with any policy

  • June 12, 2020
  • 5 replies
  • 6753 views

hello

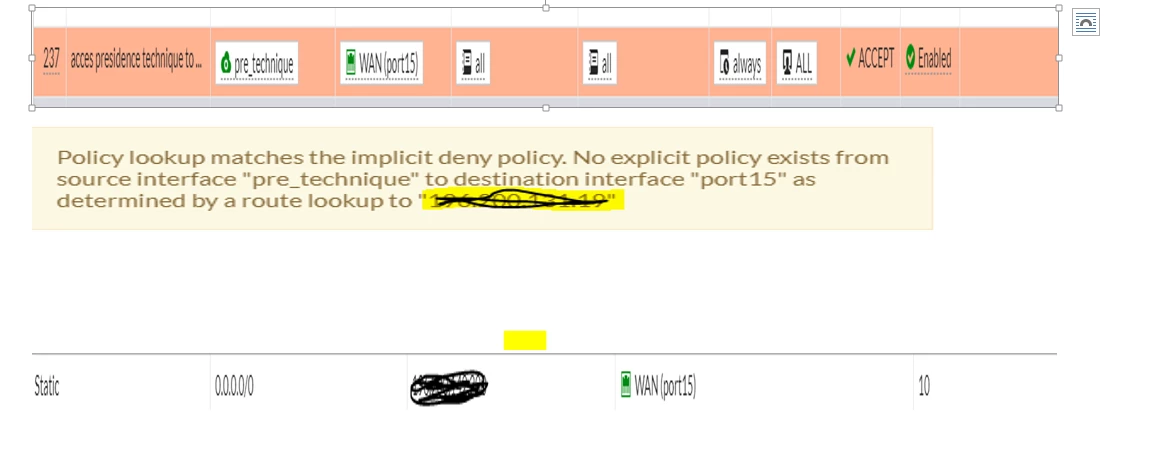
i have a only one subnet that don't much with any ipv4 policy, when i check the router loockup i find the route to this subnet but when i use loockup policy to this subnet they much with poiciy id=0  knowing that i have policy from my vlan to wan with source set to any and destination set to any and all service are accepted

Best answer by emnoc

comon,It's not a bug in the fortigate it not fortios or hardware issue.,


If you'e hitting policy 0 and you think you have a policy that should have match and  it DID not, than your policy creation is flawed , or incorrect, typeo, wrong interface(s), wrong  address, wrong service ...pick one but your policy is NOT being matched and a reason exist as to why.


The diag debug flow  output kinda of tells you where your next step(s) are. Your screenshot attachment clearly tells you you have no match also.


You need to do some more work and correct the reason as to why the "the policy that you  'wrote' " is not working. It's really that simple. 


Ken Felix


5 replies

ede_pfau
SuperUser
SuperUser
June 12, 2020

Re-check and double check the network address and netmask on the interfaces involved. Even with a matching route (again: check address and mask) and a plain open policy a connection might fail.

You can debug that by using "diag debug flow" but my experience is that if you already know it's hitting policy 0 it will not give you any additional info.

emnoc
New Member
June 12, 2020

Ede nalied it but yoru answer is in your screenhot. It sounds like the wrong interface pairs are not being matched.


Here's a trick I've been doing now for 14+ years. If you believe the src-dst-address and service is correct, change the policy src/dst-interfaces to "all" and test. If the traffic matches that changed policy, you know the interfaces are wrong.


e.g


config firewall policy edit 2 set name "school out" set uuid ba78edf0-79ec-51ea-75d7-3e1d831dc294 set srcintf "lan" set dstintf "wan1" set srcaddr "LAN" set dstaddr "all" set action accept set schedule "always" set service "DNS" "FTP" "HTTP" "HTTPS" "IMAPS" "NTP" "PING" "POP3S" "SMTP" "SMTPS" "FTP_GET" "FTP_PUT" "SSH" "SYSLOG" "TRACEROUTE" "VNC" set nat enable next


now I made it simpler by eliminating  the interface from the policy


config firewall policy edit 2   set srcintf "any" set dstintf "any" set srcaddr "LAN" set dstaddr "all" set action accept set schedule "always" set service "DNS" "FTP" "HTTP" "HTTPS" "IMAPS" "NTP" "PING" "POP3S" "SMTP" "SMTPS" "FTP_GET" "FTP_PUT" "SSH" "SYSLOG" "TRACEROUTE" "VNC" set nat enable next end


Ken Felix


issame
issameAuthor
New Member
June 12, 2020

thank you for all but i try  to use any interface in destination , all services but they don't work, and i already execute the diag debug flow but without any solution, i think that i need to restart the policy but i don't know how!!

i thnik this a bug inside fortigate.

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!
