Solved
SSL-VPN with WAN Interface containing secondary ip addresses
Hello all,
we have a /28 subnet which is provided to us by our ISP. From this we can use 11 addresses.
I have created this network as a physical interface with the "secondary IP Address" option.
The first address as IP/Netmask in the interface and the others in the table below.
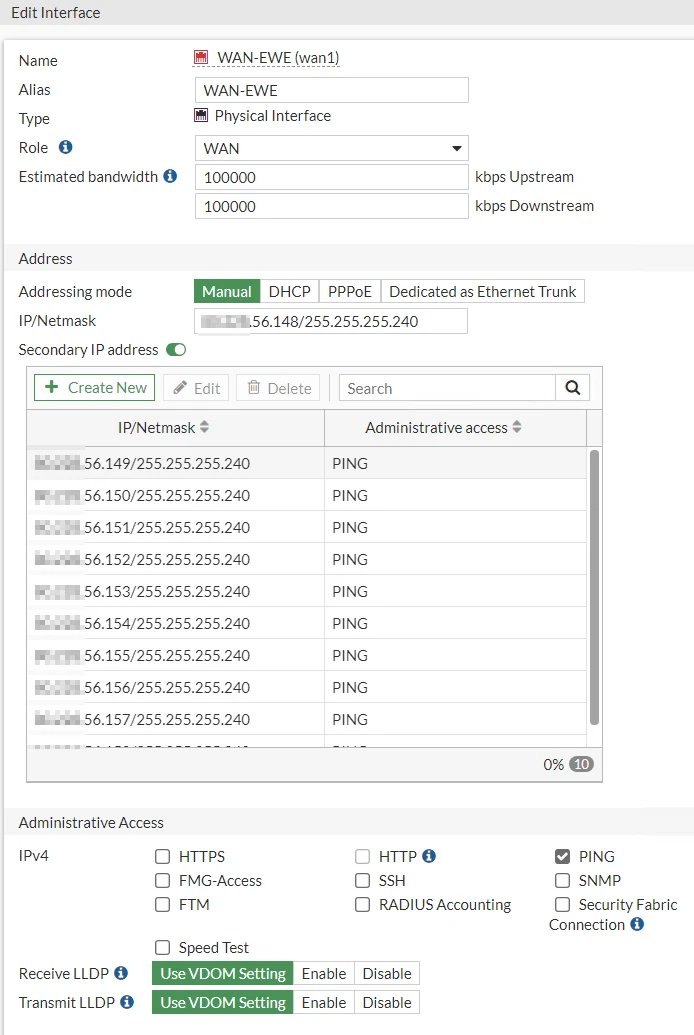
But now I want to use VPN only on the first address. This blocks me now on all other addresses the port.
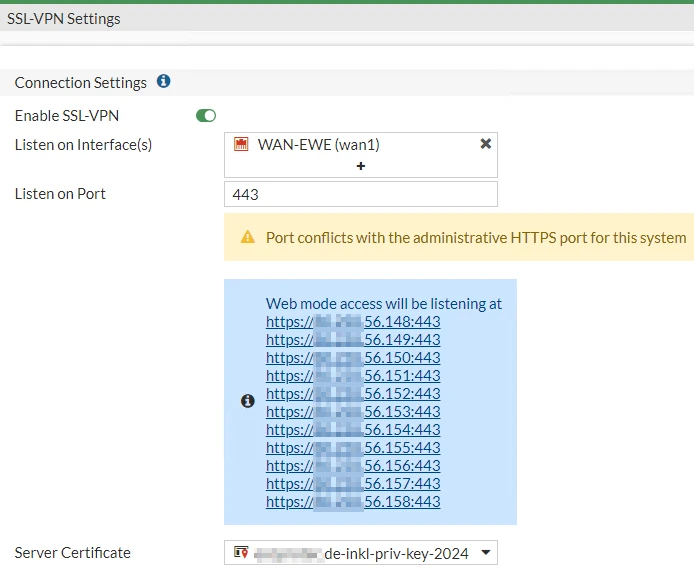
Or am I not following best practice for the WAN connection with multiple fixed IP addresses?
We are currently moving from an Sophos UTM to Fortinet and many things have been implemented differently here.