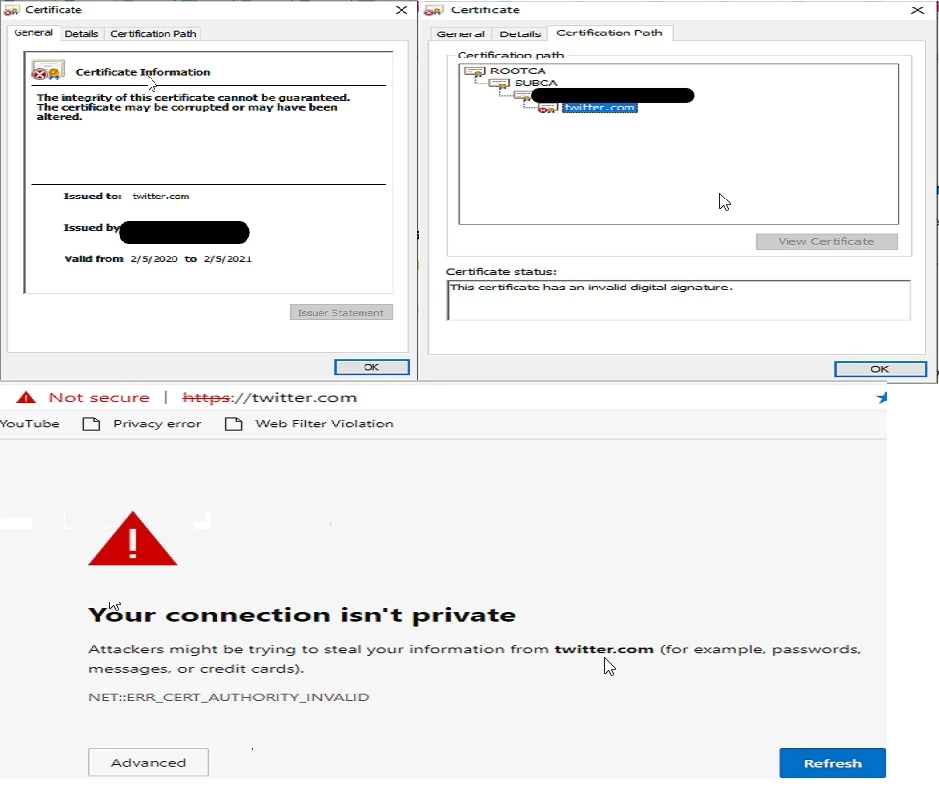
SSL/SSH Inspection Challenge - Invalid Digital Signature
Hello all. I'm experiencing some difficulties with using Web Filtering and SSL Inspection. My test policy has blocked the usual culprits (social media, gambling, porn, etc.) and I have a test machine and user going to the Internet via the policy. This is what I've done:
- Acquired root and subordinate CA certs from my sub ca server, imported them into FGT as root and sub CAs respectively.
- Created a local CA for the FGT via the Issuing server (my sub ca server)
- Created an SSH/SSL Inspection profile utilizing the local CA object
- Created a Web Filter profile blocking the usual suspects
- Created policy outlining both the SSL Inspection and Web Filter profiles and made it so only a single user/PC combo hits it
Below are some of the issues I'm having with some websites. Others are blocked and show the block page as expected. All HTTPS websites. What am I doing wrong?