

Some SDWAN(BGP) routes discovered on wan interface.
My issue is that if I have 2 dialup tunnels on a remote gate, each dialup is connected to a seperate ISP, if I lose the primary ISP that is connected to dialup tunnel 1 and dialup tunnel 2 (seperate ISP) picks up the routing, then some routes are discovered on the correct dialup interface, but others show as being discovered via the wan interface.
I am not sure what the problem is.
See below:
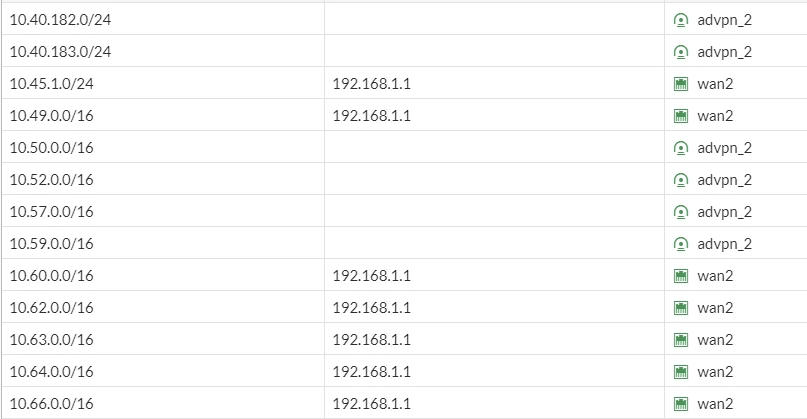
This is in a test environment. The gates are on 7.2.8
Remote Gate
config vpn ipsec phase1-interface
edit "advpn_1"
set interface "wan1"
set peertype any
set net-device disable
set proposal aes256-sha256
set add-route disable
set auto-discovery-receiver enable
set remote-gw x.x.x.x
next
end
config vpn ipsec phase2-interface
edit "advpn_1_p2"
set phase1name "advpn_1"
set proposal aes256-sha256
set auto-negotiate enable
next
end
config vpn ipsec phase1-interface
edit "advpn_2"
set interface "wan2"
set peertype any
set net-device disable
set proposal aes256-sha256
set add-route disable
set auto-discovery-receiver enable
set remote-gw x.x.x.x
next
end
config vpn ipsec phase2-interface
edit "advpn_2_p2"
set phase1name "advpn_1"
set proposal aes256-sha256
set auto-negotiate enable
next
end
Hub Dialup config
config vpn ipsec phase1-interface
edit "advpn_1"
set type dynamic
set interface "port1"
set peertype any
set net-device disable
set proposal aes256-sha256
set add-route disable
set dpd on-idle
set auto-discovery-sender enable
set auto-discovery-receiver enable
set dpd-retryinterval 60
next
end
config vpn ipsec phase2-interface
edit "advpn_1_p2"
set phase1name "advpn_1"
set proposal aes256-sha256
next
end
config vpn ipsec phase1-interface
edit "advpn_2"
set type dynamic
set interface "port2"
set peertype any
set net-device disable
set proposal aes256-sha256
set add-route disable
set dpd on-idle
set auto-discovery-sender enable
set auto-discovery-receiver enable
set dpd-retryinterval 60
next
end
config vpn ipsec phase2-interface
edit "advpn_2_p2"
set phase1name "advpn_2"
set proposal aes256-sha256
next
end
Thank you for any help.


