
luca1994
Explorer III
January 15, 2024
Solved

SNMP no response: timed out

Hello team,


I configured snmp.

I enabled snmp in the management interface, after which I went under "System > SNMP" and configured as follows:
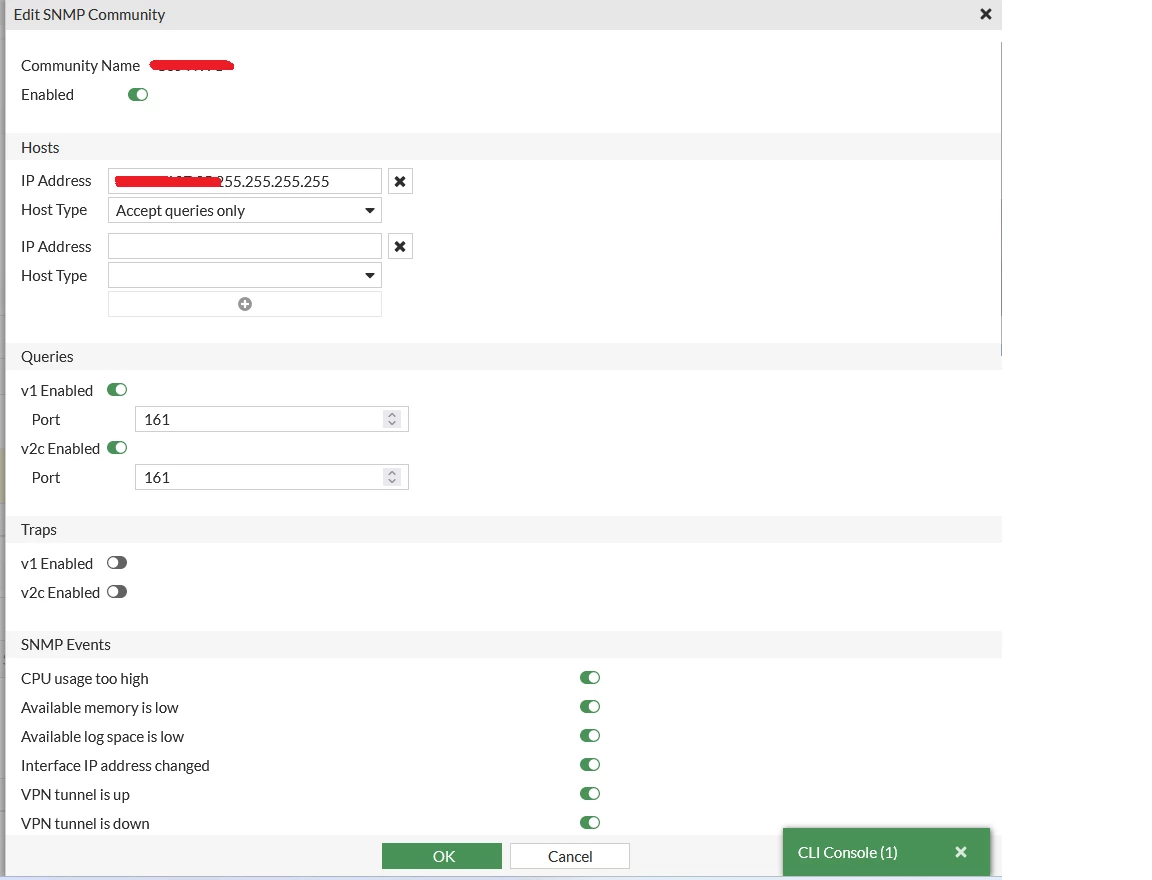
 

snmp.png

When test with snmpwalk command via cli from my monitoring system, Fortigate side capture this traffic:
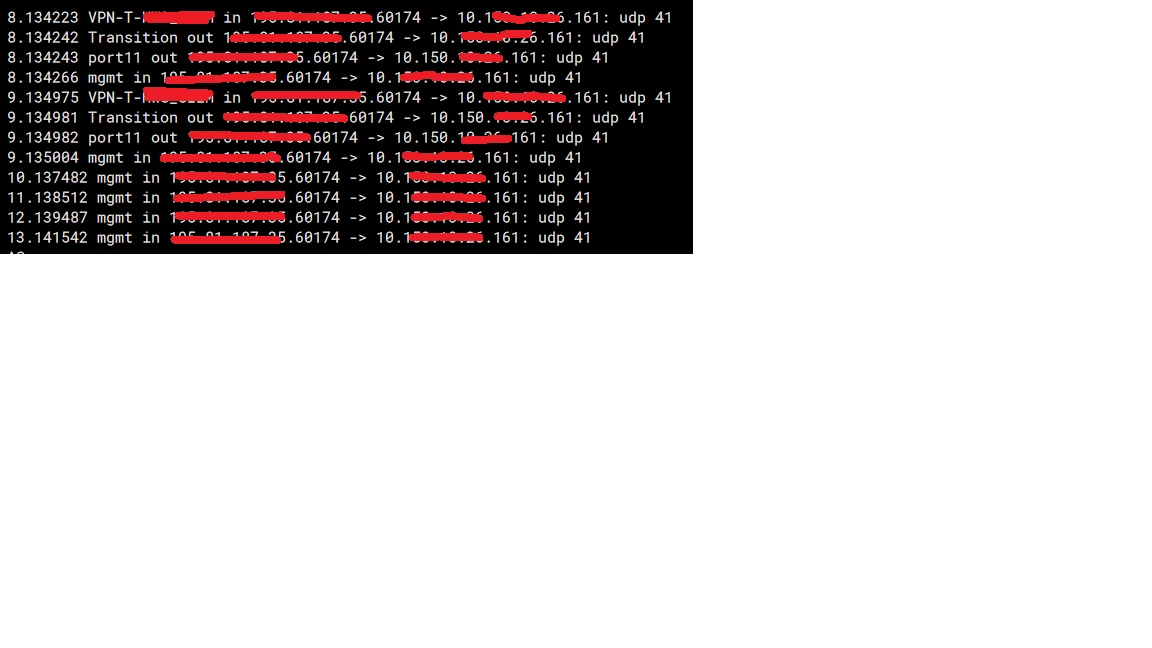
 

capture.png


it is as if the fortigate is not responding to snmp traffic. Maybe some policy is missing?

Thanks for the support


BR

AEK
AEKAnswer
SuperUser
January 15, 2024

Hello Luca

If your host is not in the same VLAN as your mgmt interface, they yes you have to add a firewall policy as follows:

  • Source interface: Interface from which the host is sending SNMP query (in your case I think it is VPN)
  • Source IP: Host
  • Destination interface: mgmt
  • Destination IP: mgmt IP

In case your mgmt interface is "dedicated for management", then I think you will not be able to add this policy, so I think you will have to enable SNMP on another firewall interface.

AEK

9 replies

syordanov
Staff
Staff
January 15, 2024

Dear luca1994,

I hope you are doing well.
Can you try to run the following commands when your monitoring does snmpwalk :


SSH No1:

diagnose debug reset
diagnose debug disable
diagnose debug flow trace stop
diagnose debug flow filter clear
diagnose debug flow show iprope enable
diagnose debug flow show function-name enable
diagnose debug flow filter daddr x.x.x.x <---- where x.x.x.x is the IP address of your mgmt interface
diagnose debug console timestamp enable
diagnose debug flow trace start 200
diagnose debug enable


SSH No2:

diag sys session filter dst x.x.x.x <---- where x.x.x.x is the IP address of your mgmt interface
diag sys session filter dport 161
diag sys session list
diag sys session clear
diag sys session list

Check if the traffic from your monitor station is dropped by policy - 0 deny or reverse patch fail check .

Regards,

Fortinet

funkylicious
SuperUser
SuperUser
January 15, 2024

If you are using trusted hosts for your firewall administrators to log in, you would need to add this ip of the snmp query server to one of them.

"jack of all trades, master of none"
AEK
SuperUser
AEKAnswer
SuperUser
January 15, 2024

Hello Luca

If your host is not in the same VLAN as your mgmt interface, they yes you have to add a firewall policy as follows:

  • Source interface: Interface from which the host is sending SNMP query (in your case I think it is VPN)
  • Source IP: Host
  • Destination interface: mgmt
  • Destination IP: mgmt IP

In case your mgmt interface is "dedicated for management", then I think you will not be able to add this policy, so I think you will have to enable SNMP on another firewall interface.

AEK
luca1994
luca1994Author
Explorer III
January 16, 2024

Hello @AEK ,


thank you for your response.
So not being able to do policy on the management interface it is mandatory to configure snmp on another interface and then allow this traffic via policy.
Does the same thing apply if the firewall is in HA A-P?

BR

AEK
SuperUser
SuperUser
January 16, 2024

Hi Luca

Yes it is same for HA A-P.

AEK
Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT


