simon0711
Visitor III
June 23, 2022
Solved

Site-to-Site VPN to AWS is up, but only one way connection

I have established an S2S VPN tunnel from my FortiGate-100F to AWS VPC

I can ping from the EC2 to a local device but however, I cannot ping from a local device to my AWS EC2

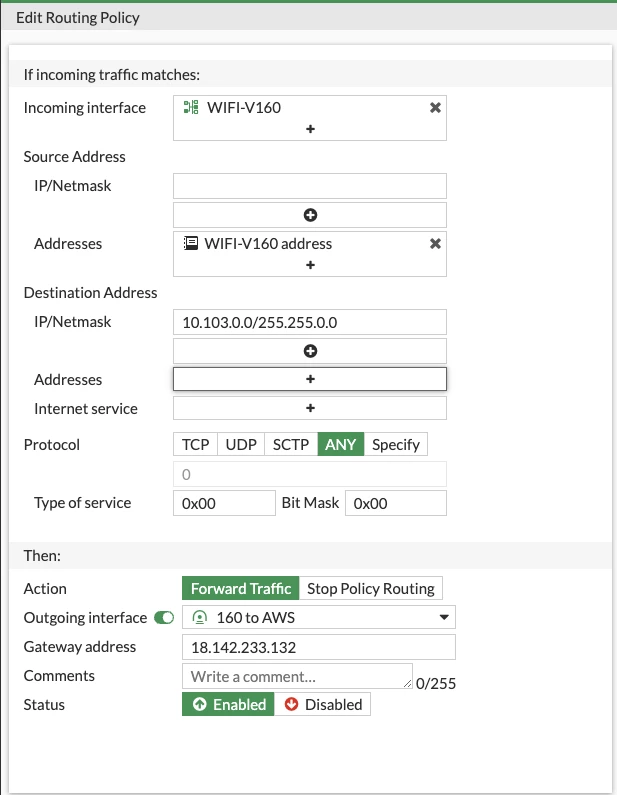
I have already set up a static route and even tried the policy route but still no luck...

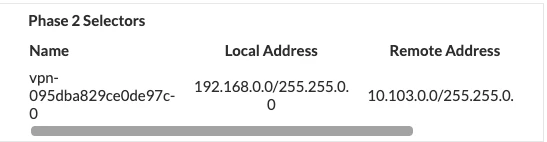
below is the config I have set

Much appreciate any help

Thanks in advance!
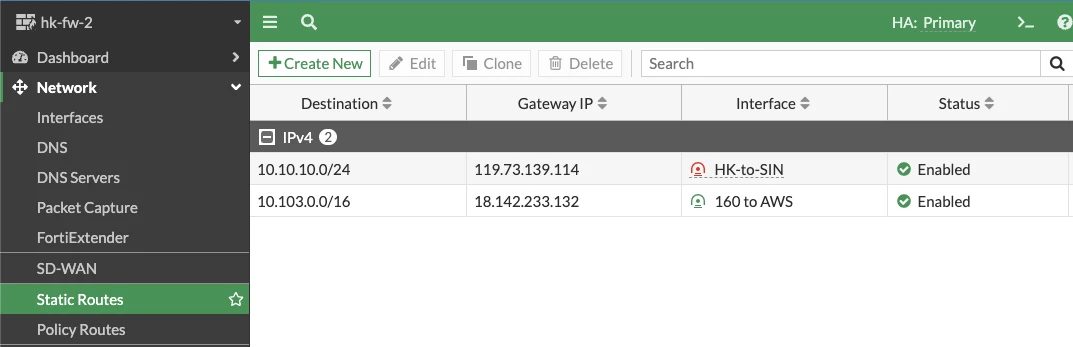
image (9).pngimage (10).pngimage (11).png

Vichu_94
Vichu_94Answer
Staff
June 23, 2022

Hi Simon,

To further troubleshoot the issue we would need to run the flow debug command on the CLI to check if the traffic is leaving the firewall or not 

di de flow filter clear
di de reset 
di de flow filter saddr x.x.x.x 
di de flow filter daddr y.y.y.y
di de flow filter proto 1
di de flow show function-name 
di de flow show iprope enable 

di de flow trace start 1000
di de en 

Where x.x.x.x is the source ip address and y.y.y.y is the destination ip address. After running the command, please try to initiate a ping from a test pc to the other site 

To disable the logs on the firewall, please run the command 

di de di

Refer link: https://docs.fortinet.com/document/fortigate/6.2.10/cookbook/54688/debugging-the-packet-flow

Regards

2 replies

Vichu_94
Staff
Vichu_94Answer
Staff
June 23, 2022

Hi Simon,

To further troubleshoot the issue we would need to run the flow debug command on the CLI to check if the traffic is leaving the firewall or not 

di de flow filter clear
di de reset 
di de flow filter saddr x.x.x.x 
di de flow filter daddr y.y.y.y
di de flow filter proto 1
di de flow show function-name 
di de flow show iprope enable 

di de flow trace start 1000
di de en 

Where x.x.x.x is the source ip address and y.y.y.y is the destination ip address. After running the command, please try to initiate a ping from a test pc to the other site 

To disable the logs on the firewall, please run the command 

di de di

Refer link: https://docs.fortinet.com/document/fortigate/6.2.10/cookbook/54688/debugging-the-packet-flow

Regards

simon0711
simon0711Author
Visitor III
June 24, 2022

Thanks for your reply, after debugging the packet flow, I am able to found out the problem, we have set wan1 as the out-going interface for my wifi VLAN which I think messed up the route, now I removed it from the policy route and it is working fine, thanks a lot for the tips!!!! 

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT