Sending around 300GB (!) logs daily to the FortiGate Cloud, but I have no idea how to stop it
Hi!
Recently, we bought a FortiGate 40F after we had a 30E in use for some years.
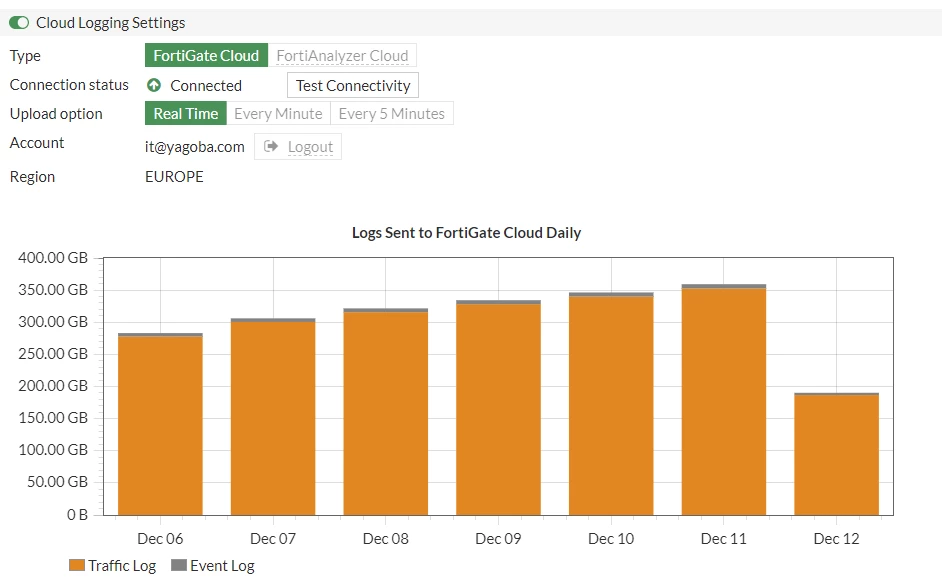
Since some time, it seems that the unit sends around 300GB of logs to the FortiGate Cloud, which seems way too much in my point of view:
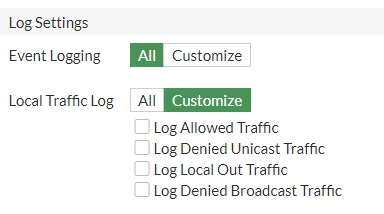
For reference, the Log Settings are:
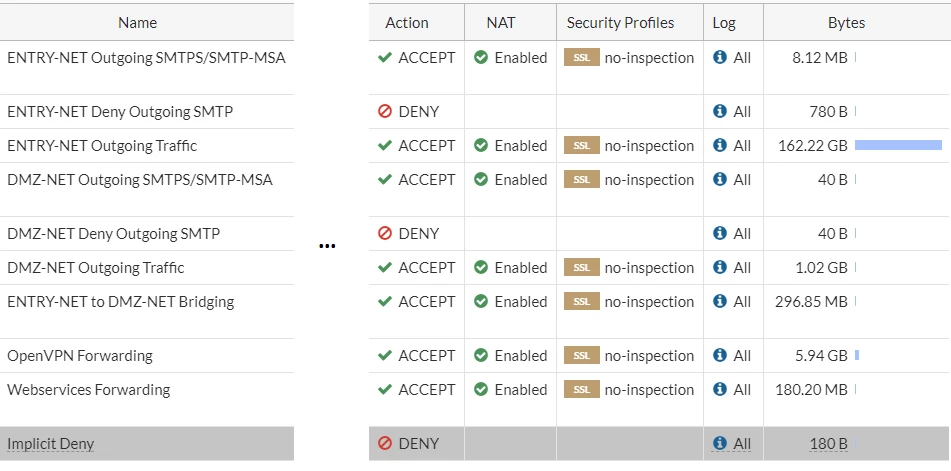
What makes me wonder is that for all the policies under "Policy & Objects - Firewall Policy", it is shown that "All" gets logged:
However, I never configured it like this and when I open the details of a specific policy, I don't see that log "All" is configured. See as an example the details for policy "ENTRY-NET Outgoing Traffic":
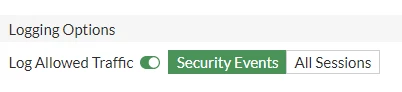
So I'm not logging "All" allowed traffic but only if it triggers security events.
Furthermore, no matter what I set here, the "All" in the list of policies changes. So even if I DISABLE "Log Allowed Traffic" here, the list of policies still shows "all" in column "Log" for the policy "ENTRY-NET Outgoing Traffic".
Remark: I have the feeling that this "All"-logging started when I activated the "Security Fabric" under "Security Fabric - Fabric Connectors - Security Fabric Setup":
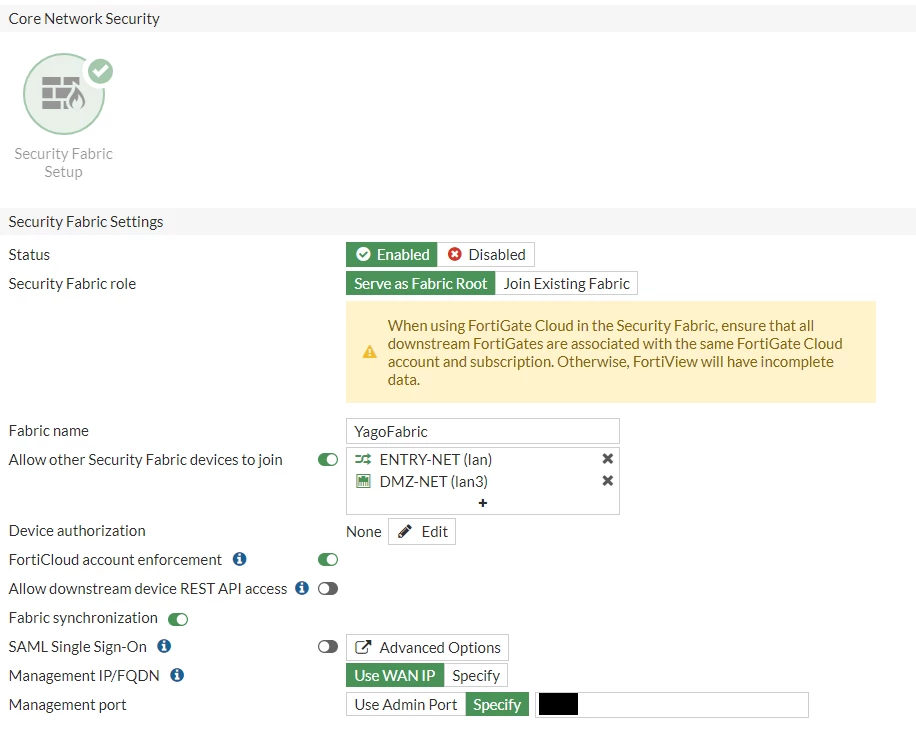
So my questions are:
- Is 300 GB of daily logs ok? I guess, no.
- If no, what have I done wrong in the configuration? In other words, how can I fix it?
- Why is the value in the Log column of the list of policies different from the actual log setting of a specific policy?
Thanks and best regards,
-Thomas