

LSI-IT
New Member
November 15, 2022
Question

SAML Auth for FortiClient EMS user verification using Azure AD as IdP

  • November 15, 2022
  • 11 replies
  • 8680 views

I'm using EMS 7.0.7 and client 7.0.7

I want to use saml auth with azure AD as the IdP when creating an invitation for user verification. I have my AD domains imported. Azure is setup to be the IdP and the test is successful. 

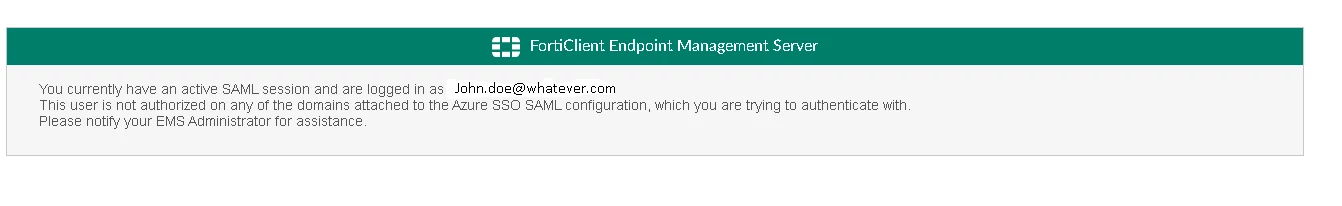
If I add the saml configuration in EMS user management with "None" as the authorization type I can get it to work using a bulk invitation. If I add saml configuration with "LDAP" as the authorization type and assign an imported domain I get an error on the client when connecting the EMS in zero trust telemetry. 
LSIIT_0-1668521435084.png

It looks to me like the imported domains are using the SamAccountName for the users and the SAML configuration is using the UserPricipalName for the assertion attribute. I'm not sure how to setup the domain identification. 


FortiNet does have some documentation on this setup but, it doesn't give allot of information 

https://docs.fortinet.com/document/forticlient/7.0.7/ems-administration-guide/156283/saml-configuration


Has anybody set this up and how did you make it work?

 

11 replies

Anthony_E
Staff
Staff
November 18, 2022

Hello LSI-IT,


Thank you for using the Community Forum.

I will seek to get you an answer or help. We will reply to this thread with an update as soon as possible.


Regards,

Best Regards
Anthony_E
Staff
Staff
November 21, 2022

Hello,


We are still looking for someone to help you.

We will come back to you ASAP.


Regards,

Best Regards
Anthony_E
Staff
Staff
November 22, 2022
Best Regards
LSI-IT
LSI-ITAuthor
New Member
November 22, 2022

Thanks Anthony_E, That document is for configuring SAML on a FortiGate with Azure AD as the IdP. I'm trying to use it on FortiClient EMS. I did get an update this morning from Fortinet support that using Azure AD as the IdP in a SAML connection in EMS will be supported in version 7.2.1 It's a little confusing because the documentation already reads like it's supported. It would still be great to know if anyone else has experienced this issue and what they did to work around it.

Zakari81
Explorer
December 16, 2022

Hi LSI-IT,


I am having the same issue, no documentation on it, i am using EMS version 7.0.7.0398

Anthony_E
Staff
Staff
November 22, 2022

Hello,


Indeed :)!

I will try to find you somebody!


Regards,

Best Regards
GenesisTechhub
New Member
August 23, 2023

I have the same issue. Has anyone found a resolution for this?

JonasV
Explorer
September 21, 2023

I have the same issue, trying to connect to EMS from my FortiClient by using SAML invite

ALLEOFLO
New Member
October 26, 2023

Same Bug here in 7.2.2 :(

xlntech
New Member
November 5, 2023

Anyone get anywhere with this? FortiDocs are the worst. 

BreakinLabs
New Member
May 2, 2024

The crucial step lies in employing a custom claim within FortiClient, such as the username, and subsequently configuring a corresponding claim with identical nomenclature in the attributes within Azure, which should be mapped to the userprincipalname.
FC1.pngFC2.png


Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!
