



Route Branch FGT to BGP via Site to Site VPN
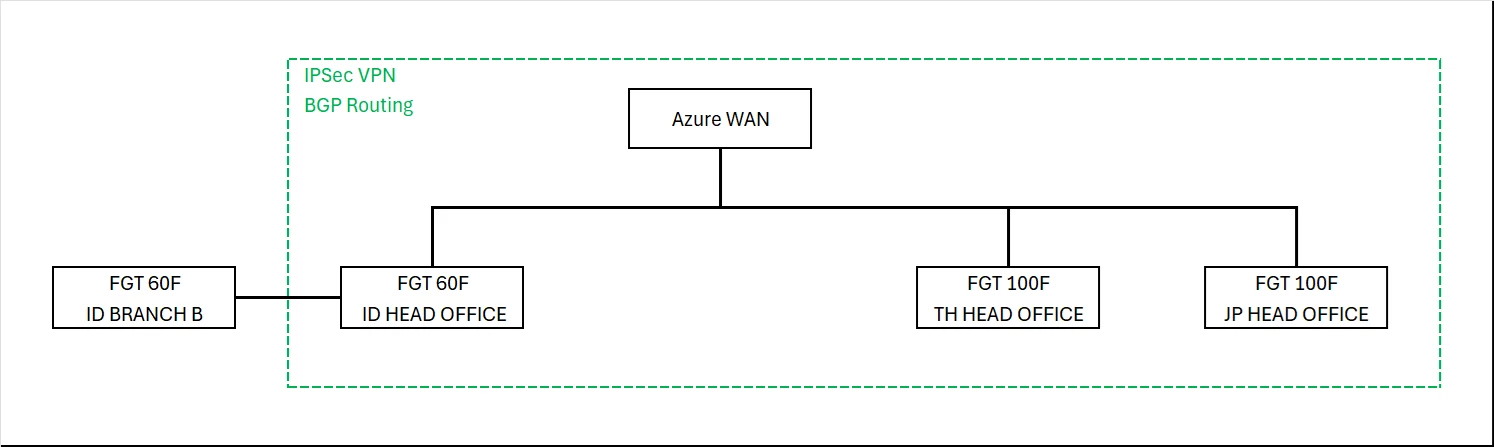
Hi all, I have some question regarding the routing in FortiGate here. I have attached the topology here for better understanding. I only have a control of ID FortiGate and cannot see the configuration on Azure WAN and other Head Office. Current condition is in the green box, all Head Office FortiGate has IPSec tunnel to Azure WAN, and I think the Azure WAN is responsible for the BGP routing to all other Head Office. From ID Head Office, I can connect to TH Head Office and JP Head Office. Everything is working well.
So, I have a new Branch office in ID. I can create the site-to-site VPN between ID Head Office and ID Branch, but the problem here is to connect the ID Branch to TH Head Office or JP Head Office via ID Head Office. Does anyone ever have this kind of configuration and can give me suggestions about how to configure it?
Thank you.
