

Solved
PeerID/LocalID on IPSec client VPN
Hello,
I'm currently configuring a second client IPSec VPN. The new uses IKEv2, on the same WAN interface/IPaddress. I saw help pages about the PeerID and LocalID, but my tries aren't okay. I have an phase1 error. I put a PeerID on the Authentication frame, and I reported it on the LocalID in the Forticlient configuration as I understand. Is it okay ? What about the LocalID on the Fortigate ?
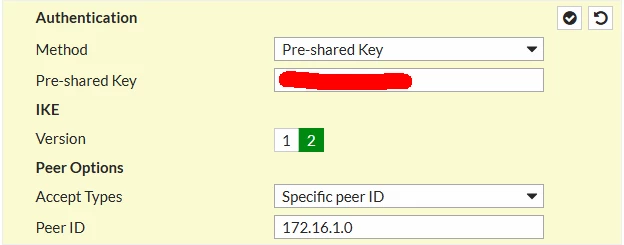
The existing Client VPN has this configuration :
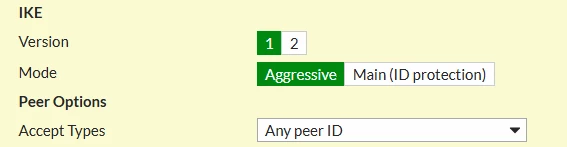
Is this configuration a problem ?


