

amizi
New Member
April 24, 2022
Question

OSPF and IPsec

  • April 24, 2022
  • 2 replies
  • 1281 views

Hi there,

I'm trying to create an OSPF icluding both FortiGates and Cisco routers.

Do I need to configure only the linked adresses to each port?

And how do I configure IPsec between the two fortigates? Do I need to configure the VPCs as well on the FG? I got a little bit lost...
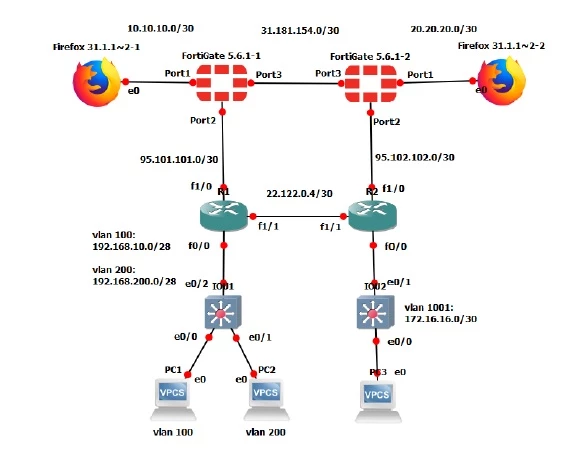
fotriask.jpg

2 replies

akristof
Staff
Staff
April 25, 2022

Hi,


Thank you for your question. You need site to site Ipsec tunnel and then configure IP address to the tunnel on both FortiGates. And then enable OSPF on these IPs. And that's it.

seshuganesh
Staff
Staff
April 25, 2022

Hi Team,


As my colleague mentioned you need to define IPSEC tunnels and mention IP address in tunnel interface and configure IPSEC tunnel between them.

For this question:

 Do I need to configure the VPCs as well on the FG
Seems like your environment is there in AWS, you have to deploy firewall in any VPC  and define lan ip of the firewall in same VPC.

While establishing IPSEC tunnel between two fortigate firewall, you have to mention elastic IP of the remote firewall.

This should establish IPSEC tunnel.

Make sure you define securty group to allow the traffic for port 500 and 4500.

Please check and keep us posted.