Options to pass a VLAN through different Fortigate interfaces in NAT mode
Hello team!!!
I hope it goes well for you!
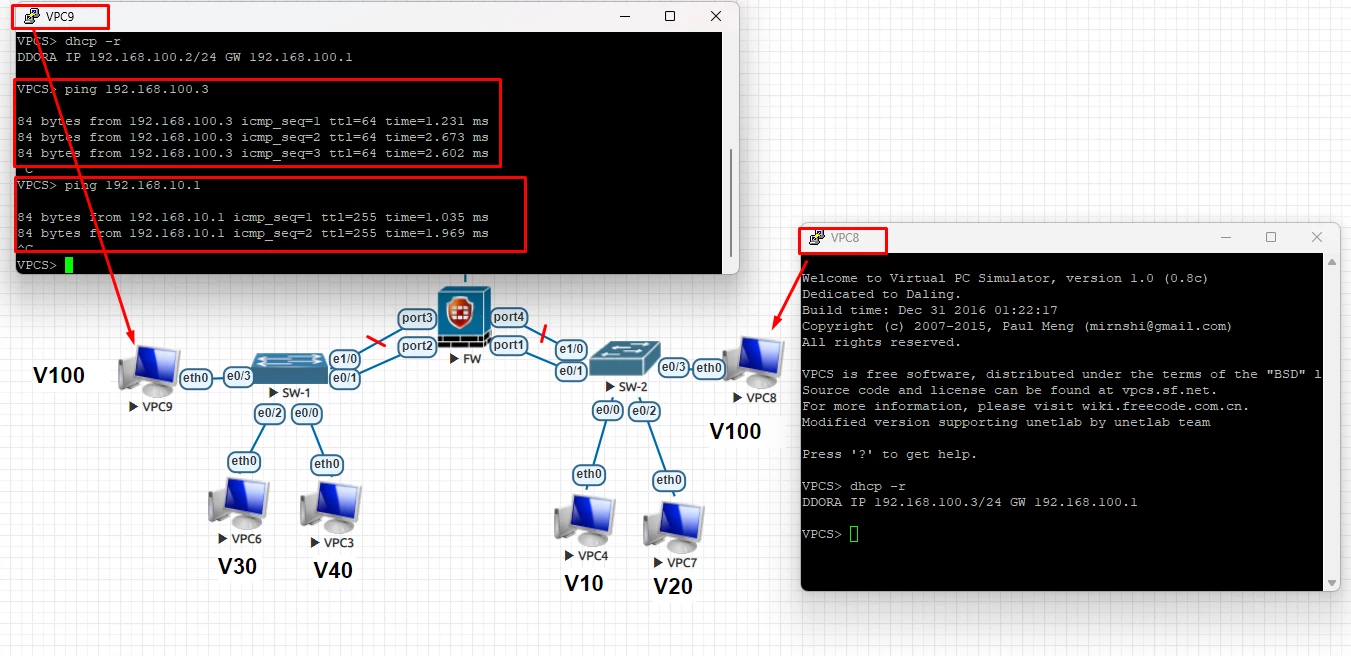
We have 2 different "trunk" interfaces (With different VLANs on each one).
For example:
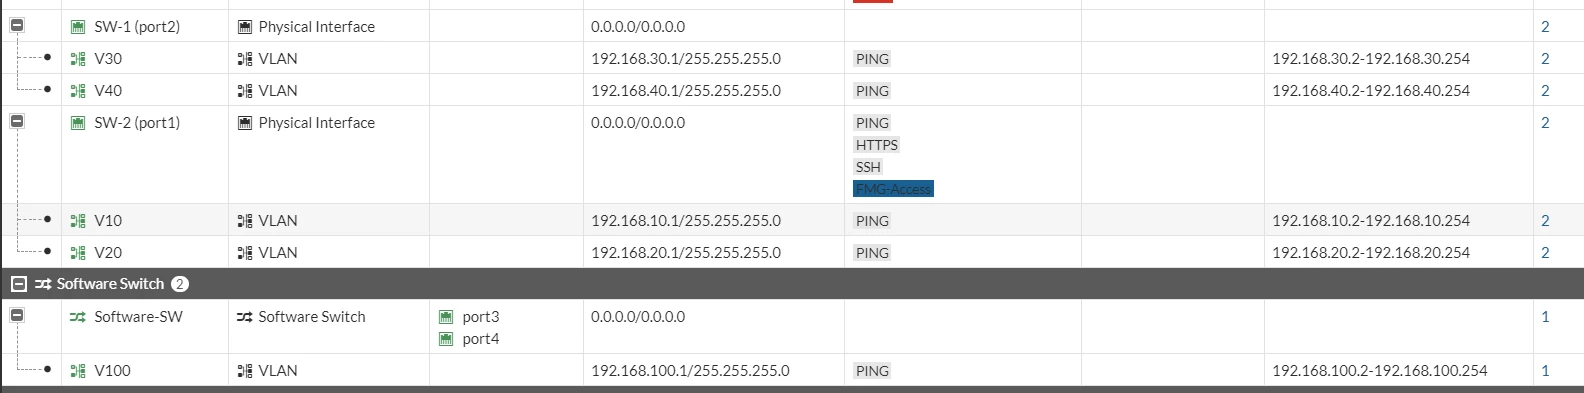
* VLANs 10, 20 and 30 on port1
* VLANs 40, 50 and 60 on port2
Now, we need to add the VLAN 100 in both trunks interfaces
Because, for example, we need to access from something in VLAN 100 connected to port1 to something on VLAN 100, connected to port2.
We have a managed switch directly connected to port1 and a different managed switch connected to port2
I thought to create the first VLAN Switch (Other 2 are not VLAN switches, just interfaces with VLANs) but I do not believe I will be able to use current port 1 and port 2 on it
So, with my moderate knowledge, I think the following 2 options:
* Create a VLAN switch for different ports (example: port3 and port4), with VLAN 100, and connect both to each managed switch in a different port, with VLAN 100 as tagged
* Create a virtual switch (without VLANs) for different ports (example: port3 and port4), and connect both to each managed switch in a different port, with VLAN 100 as untagged
I think these 2 options are not so prolix.
Is there other option?
What do you suggest?
Thanks in advance.
Regards,
Damián