
MarcusCope
Explorer
March 4, 2022
Solved

Name resolution issue with Azure AD Firewall Auth / Guest Wi-Fi Captive Portal

Hi,

I have a FortiGate 100F with a LAN interface (10.1.10.1) that uses the local Captive Portal to authenticate users to Azure AD using SAML 2.0 SSO.

I also have a Wi-Fi Interface (10.1.40.1) that uses the local Captive Portal to authenticate guest users with temporary accounts created in ‘User & Authentication -> Guest Management’.

The Captive Portal FQDN is -  captive.local.acme.co.uk

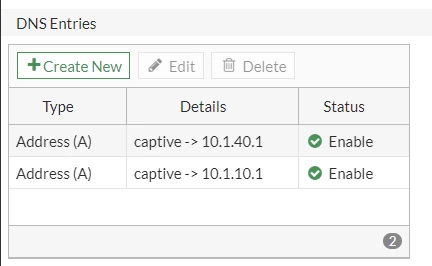
I have setup the FortiGate DNS Server database, created a local.acme.co.uk zone and created two DNS A records for the Captive Portal for this FQDN.

Captive -> 10.1.10.1

Captive -> 10.1.40.1

All appeared to work OK for a few days, but now the DNS resolution is selecting the wrong A record, e.g. 10.1.40.1 is being resolved when trying to connect to the Captive Portal from the LAN interface.

Is there any way to force the correct FQDN to IP Address resolution? Or an alternative way of achieving Azure AD firewall authentication and Guest Wi-Fi on the same FortiGate?

Thanks!
MarcusCope
Explorer
March 10, 2022

I've changed the order that the 'Captive' records appear in the Entry table and now 10.1.10.1 is always returned first. 

MarcusCope_0-1646924644305.png

This works out better for me because the Azure AD firewall auth gets used much more than the Guest Wi-Fi does.


9 replies

Esteemed Contributor III
March 7, 2022

Hello MarcusCope, 


Thank you for using the Community Forum. I will seek to get you an answer or help. We will reply to this thread with an update as soon as possible. 


Thanks, 

Raja- Fortinet Community Team 

 
Debbie_FTNT
Staff & Editor
Staff & Editor
March 7, 2022

Hey Marcus,

I haven't found any way to force a specific hostname to IP resolution on FortiGate, but I am not an expert; perhaps someone else can provide some information.

The only workaround I can suggest is to exempt the IPs in captive portal settings:
- on the LAN interface, exempt the WiFi interface IP
- on the WiFi interface, exempt the LAN interface IP

-> this should make captive portal reachable on both interfaces no matter which IP the hostname resolves to

MarcusCope
Explorer
March 8, 2022

Hi Debbie, thanks for the reply! I've already tried something similar to your suggestion. I created a firewall rule that allowed traffic from the Guest Wi-Fi LAN to the Captive Portal on the LAN network and another from the LAN to the Captive Portal on the Guest Wi-Fi network. The issue is that Captive Portal setting for each network are set on the Interface, therefore when trying to connect to the Guest Wi-Fi it tries to authenticate to Azure AD.   

Debbie_FTNT
Staff & Editor
Staff & Editor
March 8, 2022

Hey Marcus,

that is why I suggested the exemption on the interface itself :)

Basically this:

Debbie_FTNT_0-1646737354437.png

This allows traffic to the other interface IP to bypass captive portal requirements, and hit the captive portal on the other interface instead.

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT


