

bascheew
Visitor III
March 17, 2020
Question

Multiple SD-WAN groups. What are your thoughts?

  • March 17, 2020
  • 3 replies
  • 7917 views

We're in the process of helping a client simplify their network and had a thought during the design phase.


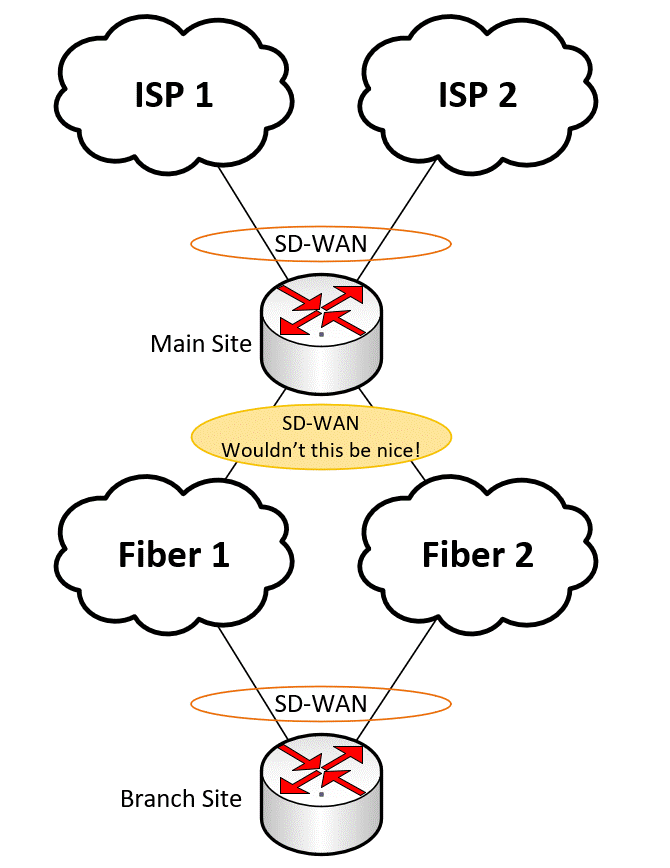
SD-WAN will be used at the main site for their internet circuits - that part's easy.  They also have multiple 1Gbit fiber circuits with different carriers that connect to their remote campuses.  Normally we would choose one of the following:

[ol]
  • Use a routing protocol - probably OSPF in this case.
  • Use an SLA and monitor the health of the link and drop the static routes if the link goes down.[/ol]

    We really like SD-WAN - the abstraction is very helpful and so easy to setup!  What if we could leverage SD-WAN for the internal fiber links?  I don't see a way to add another SD-WAN (virtual-wan-link) to a Fortigate, so it appears we're limited to just one.  We could turn up another VDOM and use SD-WAN there for the fibers, but that adds a layer of complexity to troubleshooting that I don't want to put on the client.  Any thoughts?  Is this crazy talk?  See the diagram for clarity.
     

    • 3 replies

      bascheew
      bascheewAuthor
      Visitor III
      March 17, 2020

      As a followup to this for those that want the full picture.


      We will have multiple VDOMs on the main Fortigate with matching VDOMs on the branch campus Fortigates (employees, residents, clients).  This traffic should remain separated, so we're using EMAC VLANs and assigning each EMAC VLAN to the appropriate VDOM.  Then the default route for the branch employee VDOM is the employee VDOM at the main site, the route for the branch resident VDOM is the main resident VDOM, etc.  If you've done a design like this before let us know your experience.

      Toshi_Esumi
      SuperUser
      SuperUser
      March 17, 2020

      That's the complaint I made to a FTNT SE. With the current only-one-instance design, only thing you can do is to use members in a rule, like rule#1 includes only wan1 and wan2, rule# includes internal4 and internal5, etc., which could easily confuse admins and high probability of misconfiguration.

      James_G
      New Member
      March 17, 2020
      Remember routing between SD-WAN interface members is totally open and not firewalled, ouch I have also asked se for multiple SD-WAN interfaces
      Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
      Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!

