Multiple IPsec tunnels between head and branches, using SDWAN
Hello,
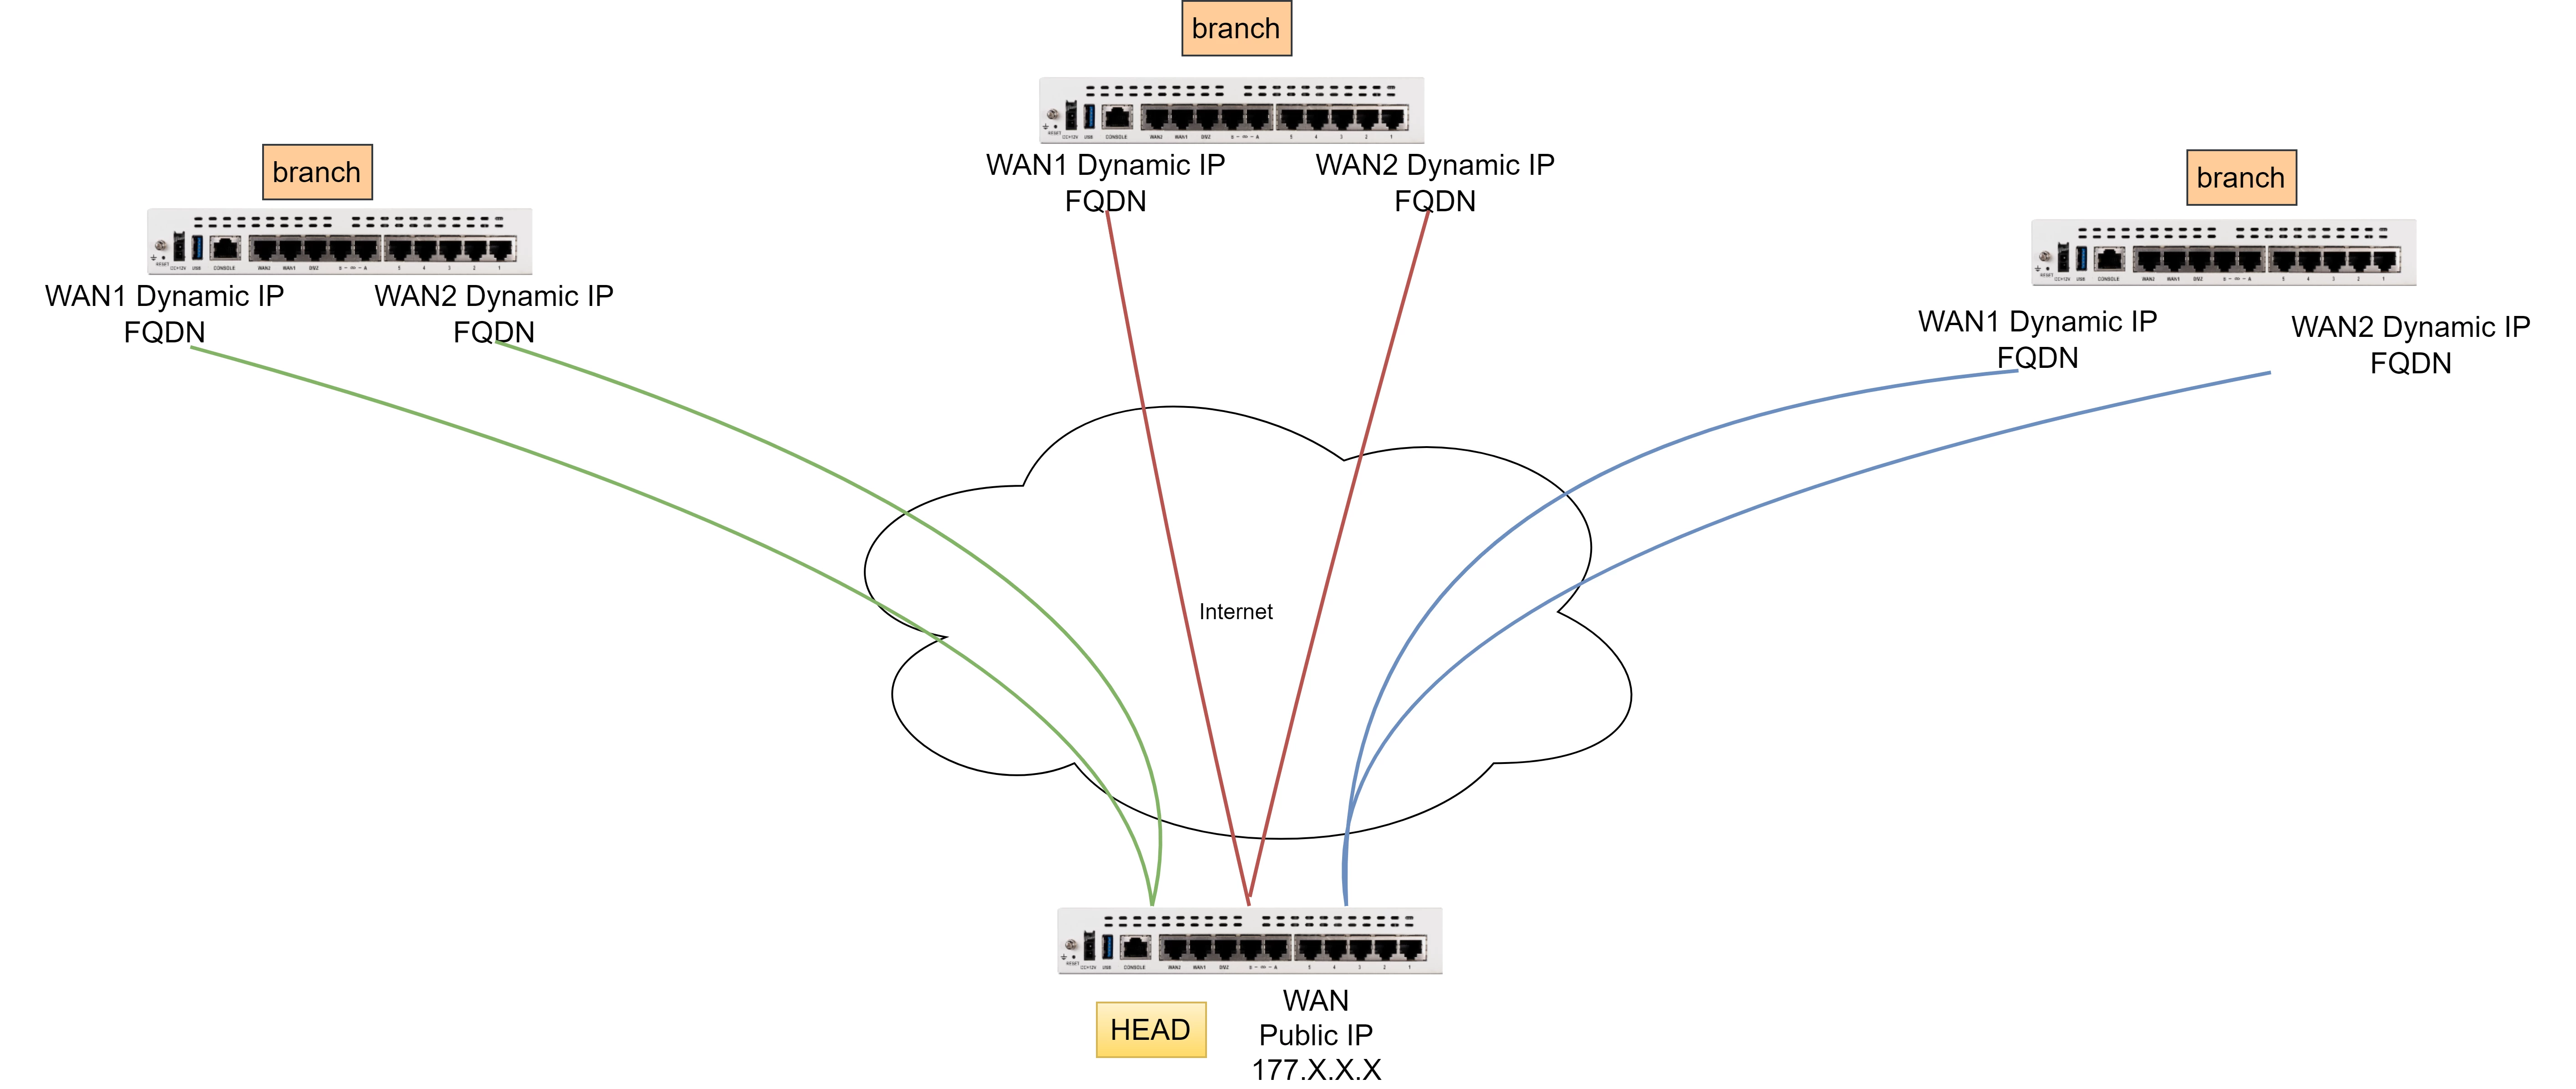
I am implementing a scenario where I will have a headquarters and several branches, connected through IPSec tunnels.
In the headquarters firewall I will have a fixed public IP address and in the branches I will have internet links with dynamic IP addresses (CGNAT and LTE/4G).
I need to connect two IPsec tunnels per branch with the headquarters, one tunnel for each WAN and I need to use SDWAN to control this traffic and define the SLA for each tunnel.
I already have this working format using IPsec SDWAN, where I create 1 tunnel for each link.
However, at headquarters, I only have one WAN interface and I use it in all tunnels with branches. Could this cause me some kind of problem? I've already noticed that when I make a change on the matrix side in a tunnel, it momentarily "drops" the connection in the other tunnels.
What is correct on the head office side, considering that I only have 1 WAN interface, is to have 1 tunnel for each branch?
Today I have 1 tunnel for each branch link, for example, branch 1 has two WANs, so I have an IPsec tunnel for WAN1 and another IPsec tunnel for WAN2, and so on. Always using FQDN because the public IP is dynamic on the branch side.
My question is whether this configuration I am using is recommended for this connection format.