migrate my SSL full tunnel VPN from using an Address IP List
Good day, I am trying to migrate my SSL full tunnel VPN from using an Address IP List (10.0.3.0/21) to issue IPs to VPN users to using an external Microsoft DHCP server, I need to do this as the FortiGate can’t add DNS records for VPN users as it does not support this.
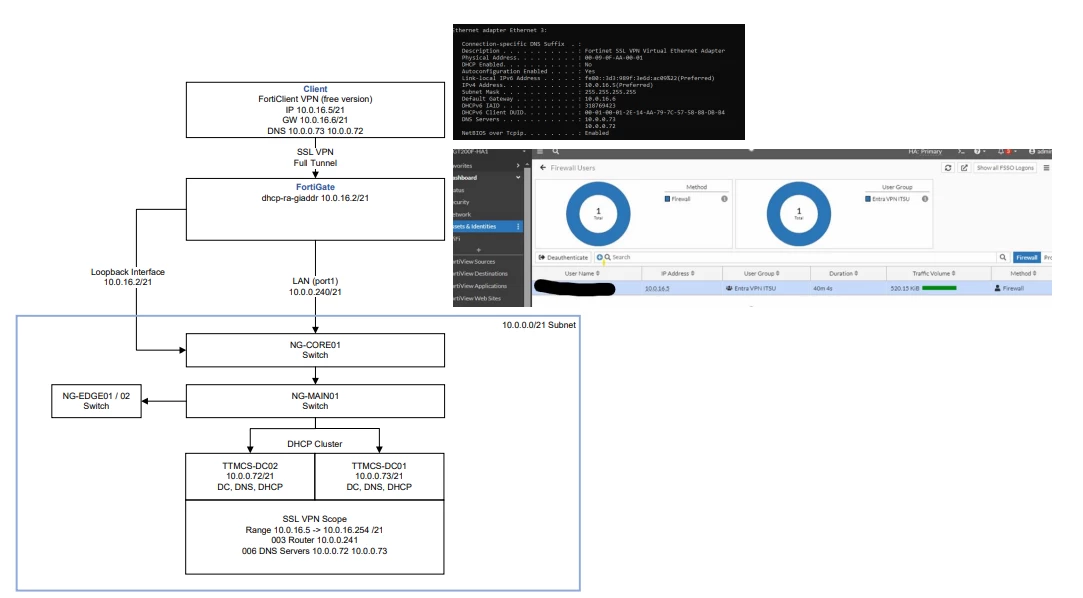
I have set up a new scope on the Microsoft DHCP server 10.0.16.0/21 as shown in the screenshot, my local subnet is 10.0.0.0/21, I can’t use the existing Subnet as it conflicts with the DHCP server.
The issue I am facing is that when I connect to the SSL VPN once I have migrated, I am unable to access any devices on the 10.0.0.0/21 subnet, I updated the Firewall policies to the new Subnet and updated the VPN settings following the Fortigate guide here https://community.fortinet.com/t5/FortiGate/Technical-Tip-SSL-VPN-with-external-DHCP-Server/ta-p/215644.
I noticed that when connected to the SSL VPN the client gets two IP’s for example in the screenshot on my test device I got 10.0.16.5 as my IP and 10.0.16.6 as the Gateway which I don’t understand if the SSL VPN assigns 10.0.16.6 as my gateway what should I set the gateway to in the Microsoft DHCP server?
Also, as I am using a Subnet outside of the local Subnet, I am not sure if I need to add any routing. I have tried to add a Static route for the SSL.root interface but not sure what the Destination or Gateway IPs would be because of the Gateway 10.0.16.6 issued to the client above.