

NAS
New Member
October 21, 2025
Question

Major lags with enabled web filter on FortiGate 70G (FortiOS 7.4.8 & 7.4.9)

  • October 21, 2025
  • 17 replies
  • 3623 views

I have a FortiGate 70G (tested with FortiOS 7.4.8 & 7.4.9) in use at a customer site. The FortiGate is connected to FortiClient EMS Cloud and FortiAnalyzer Cloud. When I enable the most basic web filter (in the policy’s security profiles: only Web Filter: “Default” and SSL Inspection: “certificate-inspection”), websites take an extremely long time to load for users — and eventually they just pop up all at once.


Following the packet flow, where you can see that it takes 23 seconds before the next data packets appear.
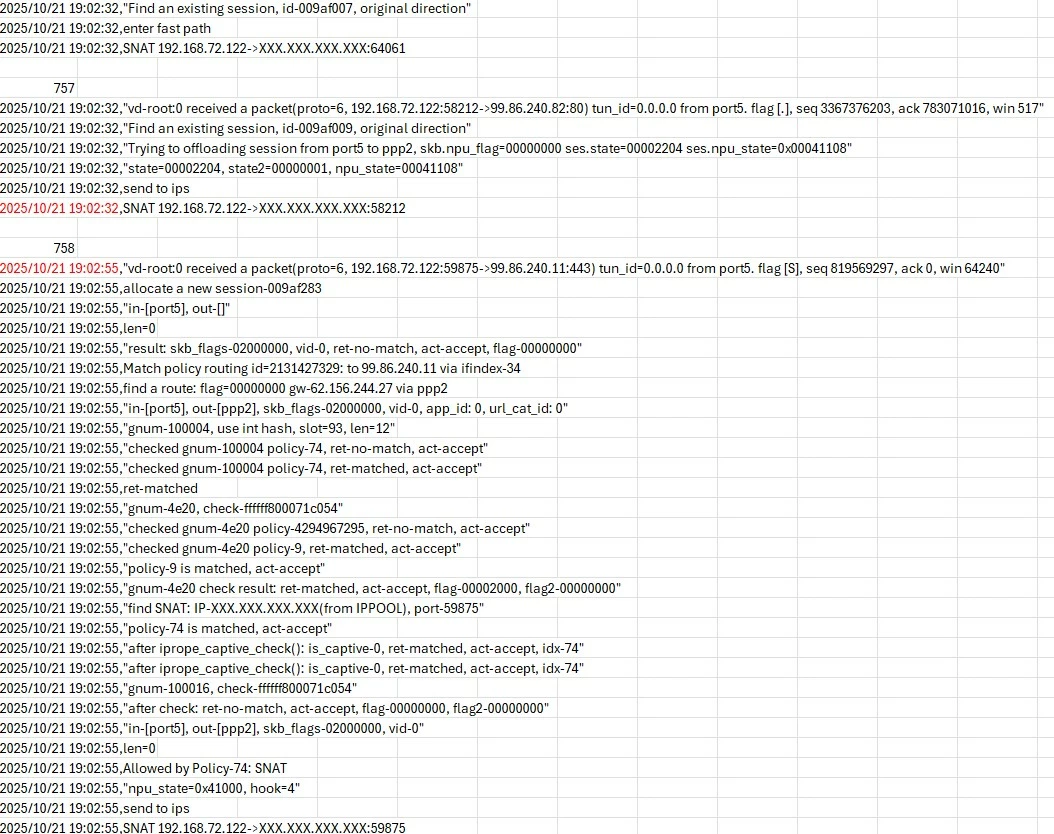

webfilterlags_debugflow.jpg


I can’t explain this behavior and don’t really know how to analyze it further in detail — maybe someone has an idea or suggestions for additional analysis. I’ve already checked the processes (wad), but couldn’t identify any anomalies there.
The accessed page was timebutler.de, but the issue also occurs on other sites. If I remove the web filter, everything runs completely normal. The logs don’t show that anything is being blocked when the web filter is enabled.


It would be great if you have any ideas or suggestions — thanks!


Best regards,
Karsten

17 replies

AEK
SuperUser
SuperUser
October 21, 2025

I see the first session is http and the second is https (a redirection?) and the delay seems just before it.

Is it the same behavior when you use https from the initial request?

AEK
NAS
NASAuthor
New Member
October 21, 2025

It seems to be the same behavior

Toshi_Esumi
SuperUser
SuperUser
October 21, 2025

Would it work normally if you disable offloading at the policies using the webfilter profile?

config firewall policy
  edit [n]

    set auto-asic-offload disable
  next
 ...
end

Then, likely another NP7/NP7Lite related bug.

Toshi

NAS
NASAuthor
New Member
October 21, 2025

I tested it — with auto.asic.offload disabled in the policy, I don’t have the issue. **bleep** :(

I have the same setup with a FortiGate 70G and FortiOS 7.4.9 in my lab, but the issue doesn’t occur there — although the configuration is much simpler overall. I already had a problem with the FortiGate at the customer site and had to downgrade from FortiOS 7.4.9 to 7.4.8 because of FortiAnalyzer Cloud. Maybe that downgrade caused some kind of issue?

Toshi_Esumi
SuperUser
SuperUser
October 21, 2025

Open a TAC ticket to get the symptom matched with any known issues. If not, they might file a new bug report.
Those symptoms might be very conditional and if NPU is the issue, I wouldn't be able to tell if 7.2.x would work better. We just experienced one of NP7 issues with 7.2.11 on some of our 1000Fs while others haven't experienced yet. 7.2.12 fixed that particular problem though.
But TAC should have suggestions which direction you can go once the symptom is identified.

Toshi 

BillH_FTNT
Staff
Staff
October 21, 2025

send to ips.pngHi @NAS 

After checking the logs, it seems that the issue has not been offloaded to the NPU yet; it was sent to the IPS instead. The slowness or blockage is likely caused by the IPS engine. If you already have a ticket number, please share it with me. I will retrieve the logs and configuration from the ticket to reproduce the issue in my lab. Alternatively, if you're okay with it, you can share the logs and configuration directly with me via my official email at bhoang@fortinet.com. I will use them to replicate the issue and investigate further. Thank you


NAS
NASAuthor
New Member
October 22, 2025

Good morning from Germany, Bill,
I just came across an article in the knowledge base that describes exactly the behavior I’m seeing.

Web pages not loading or taking too long ... - Fortinet Community

I’ll test it again later and let you know whether the solution suggested in the KB helps. Otherwise, I’ll share the configuration and logs with you by email.


Thanks and best regards,
Karsten

AEK
SuperUser
SuperUser
October 22, 2025

Nice doc.

It mentions 3 options:

  • Option 1: Disable TLS 1.3 hybridized Kyber support on the Google Chrome/Edge Browser
    Option 2: Change the firewall policy inspection mode from flow-based to proxy-based
    Option 3: Change the tcp-mss for sender and receiver to a value less or equal to 1450 for the related firewall policy

If you can test each of them and share the result it would be great.

AEK
Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!
