Question
libcertd.so is missing 7.4 vpn-only client, not able to use SAML
Hello Team, as per my admin team, I needed to install VPN only package, which I installed. Below is my output, in first you can see beginig of output, where is saying some file is missing.
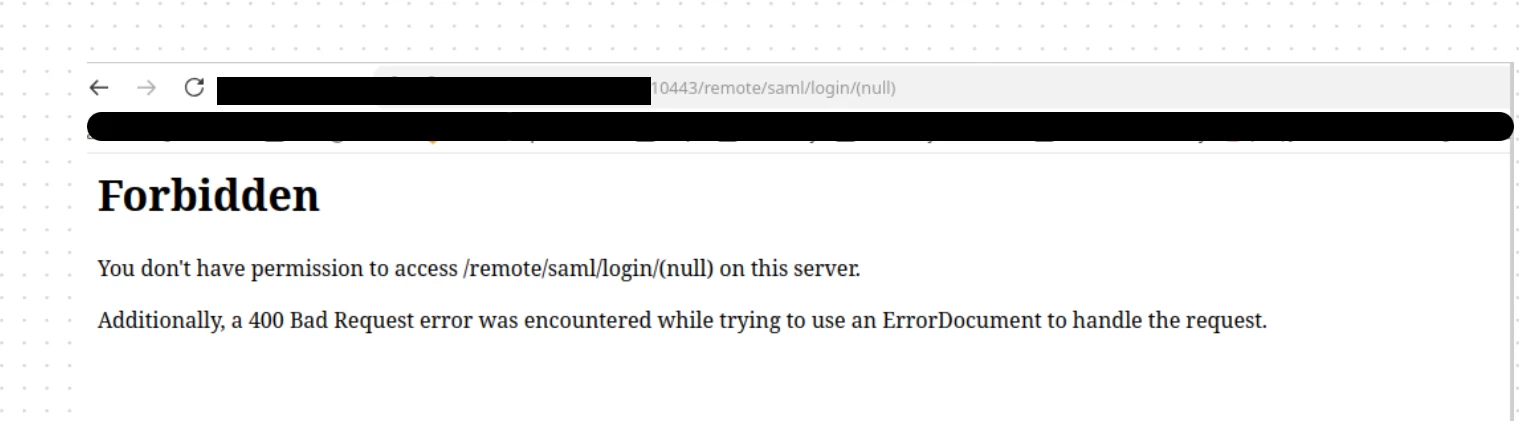
At my current company, we are using Forti vpn-only client, I don't have any experience with Forti, as I am working as DevOps engineer, in past I used local created user in forti device, but now they are removed and I need to use SSO, which is NOT working for me. I am using xUbuntu 24.04.
Please assist.
forticlient gui ERROR: Failed to add module "FortiClient ZTNA". Probable cause : "/opt/forticlient/libcertd.so: cannot open shared object file: No such file or directory". 15:25:23.076 › Failed to add libcertd.so: Error: Command failed: /usr/bin/modutil -add "FortiClient ZTNA" -dbdir sql:/home/nedeljko-scepanovic/.pki/nssdb -libfile /opt/forticlient/libcertd.so -force ERROR: Failed to add module "FortiClient ZTNA". Probable cause : "/opt/forticlient/libcertd.so: cannot open shared object file: No such file or directory".In second output, is whole output.
forticlient $ forticlient gui ERROR: Failed to add module "FortiClient ZTNA". Probable cause : "/opt/forticlient/libcertd.so: cannot open shared object file: No such file or directory". 15:28:05.816 › Failed to add libcertd.so: Error: Command failed: /usr/bin/modutil -add "FortiClient ZTNA" -dbdir sql:/home/my-user/.pki/nssdb -libfile /opt/forticlient/libcertd.so -force ERROR: Failed to add module "FortiClient ZTNA". Probable cause : "/opt/forticlient/libcertd.so: cannot open shared object file: No such file or directory". 15:28:05.898 › Server init() port number is 15:28:05.898 › Fail to retrieve port number from file. 15:28:06.901 › Server init() port number is 46047 15:28:06.902 › Main process - Websocket open ws://127.0.0.1:46047/websocket 15:28:06.905 › WindowManager handlePossibleProtocolLauncherArgs argv=["/opt/forticlient/gui/FortiClient"] 15:28:06.906 › WindowManager handleCreateMainWindow 15:28:06.919 › MAIN Starting FortiTray 15:28:06.920 › MAIN MainWindow - createWindow Platform detected: ubuntu 15:28:06.933 › web-contents-created contents.id=1 15:28:06.939 › Saml - init 15:28:06.939 › Saml - listenSamlLoginRequest 15:28:06.940 › Server init() port number is 46047 Connected 15:28:07.141 › Renderer process - Websocket open ws://127.0.0.1:46047/websocket 15:28:07.142 › compliance configDir=/home/my-user/.config/FortiClient/config 15:28:07.144 › MAIN did-finish-load 15:28:07.152 › MAIN ready-to-show 15:28:07.741 › IPC_RENDERER_REQUEST.LOADED 15:28:07.742 › WindowManager handleWindowLoaded 15:28:08.243 › WindowManager handlePossibleProtocolLauncherArgs argv=["/opt/forticlient/gui/FortiClient"] 15:28:08.244 › WindowManager handleCreateMainWindow 15:28:09.586 › Vpn - start doSamlConnect [33742:0112/152809.707108:ERROR:cert_issuer_source_aia.cc(34)] Error parsing cert retrieved from AIA (as DER): ERROR: Couldn't read tbsCertificate as SEQUENCE ERROR: Failed parsing Certificate 15:28:09.723 › remoteInfo=[object Object] 15:28:09.723 › Saml - IPC_RENDERER_REQUEST.SAML_LOGIN url=https://forti.my_company.com:10443//remote/saml/start?realm=WSR 15:28:09.724 › Server init() port number is 46047 15:28:09.729 › Saml - doSamlAuth samlReq={"connection_name":"my-comany-vpn","url":"https://forti.my_company.com:10443/remote/saml/start?realm=WSR","authTimeout":"240","ignoreCert":false,"type":1,"redirect":true,"redirectUrl":"https://forti.my_company.com:10443//remote/saml/auth_id","sso_port":"8020"} 15:28:09.729 › Saml - closeServer 15:28:09.729 › Saml - startServer sso_port=8020 15:28:09.731 › Server running on http://localhost:8020 15:28:09.731 › Saml - openExternal url=https://forti.my_company.com:10443/remote/saml/start?realm=WSR&redirect=1
Here is error which I get when I try to login via SSO, google workspace is used for SSO.