
UnderscoresAndDashes
Explorer
September 12, 2022
Solved

Issue with using multiple ports in a FortiLink interface

(Using a 300E on FortiOS 7.0.6) When I try to use multiple ports in a FortiLink interface, switches do show up in an unauthorized state, but after authorizing the switches, only one of the switches are able to come online. Each switch is connected to a different port with in the FortiLink interface, and still only one comes online.
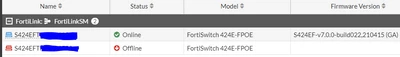
FortilinkSwitchStatus.png


As you can see below, I have "Split interface disabled" I believe this is correct.

The switch that is online is in port 23.
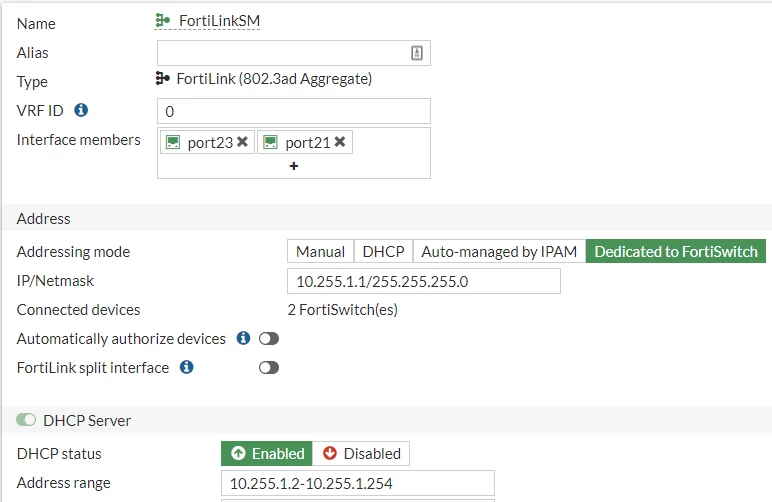
Fortilink.PNG


Why is this? If I enable "Split Interface" then I know only one of the 2 ports will work (the first one (left to right) listed).


Is there a feature I have not enabled somewhere?


gfleming
gflemingAnswer
Staff
September 12, 2022

I believe this is by design. I am not a FortiLink expert but in general FortiGate FortiLink interface connects to one switch and from there you extend to more downstream switches.


In your case you would want to enable the split interface. Connect the two switches together as well. And in this topology you have a loop that is managed by STP. Your second FortiLink interface remains down/blocking and all traffic goes through the inter-switch link and the primary fortilink interface. If either primary fortilink interface goes down or the ISL goes down, then the secondary fortilink interface comes up again.


If you want both FortiLink interfaces active at the same time you should look at using MC-LAG.


Here's what you are doing today (just two switches in your case instead of the five shown on the diagram): https://docs.fortinet.com/document/fortiswitch/7.0.4/devices-managed-by-fortios/801204/single-fortigate-unit-managing-a-stack-of-several-fortiswitch-units


Here's what you can consider doing instead: https://docs.fortinet.com/document/fortiswitch/7.0.4/devices-managed-by-fortios/801208/transitioning-from-a-fortilink-split-interface-to-a-fortilink-mclag

1 reply

gfleming
Staff
gflemingAnswer
Staff
September 12, 2022

I believe this is by design. I am not a FortiLink expert but in general FortiGate FortiLink interface connects to one switch and from there you extend to more downstream switches.


In your case you would want to enable the split interface. Connect the two switches together as well. And in this topology you have a loop that is managed by STP. Your second FortiLink interface remains down/blocking and all traffic goes through the inter-switch link and the primary fortilink interface. If either primary fortilink interface goes down or the ISL goes down, then the secondary fortilink interface comes up again.


If you want both FortiLink interfaces active at the same time you should look at using MC-LAG.


Here's what you are doing today (just two switches in your case instead of the five shown on the diagram): https://docs.fortinet.com/document/fortiswitch/7.0.4/devices-managed-by-fortios/801204/single-fortigate-unit-managing-a-stack-of-several-fortiswitch-units


Here's what you can consider doing instead: https://docs.fortinet.com/document/fortiswitch/7.0.4/devices-managed-by-fortios/801208/transitioning-from-a-fortilink-split-interface-to-a-fortilink-mclag

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT


