

Nelvin
New Member
April 29, 2019
Question

Issue: SSLVPN Connected But Can't Access to Internal Server

  • April 29, 2019
  • 4 replies
  • 10700 views

Hi everyone,

I connected forticlient-SSLVPN and get the connection.

But the problem is I unable access to my internal server.

Configuration for Fortigate 100E as attached :
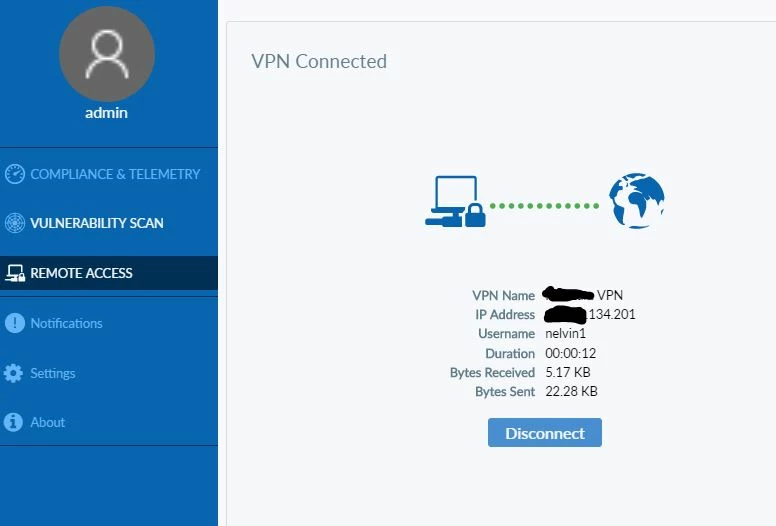


Should I add remote groups for the internal server?


Does anyone got solutions for me to try? thanks in advance =)

 

    4 replies

    Toshi_Esumi
    SuperUser
    SuperUser
    April 29, 2019

    Is it "split-tunnel" or "no split". If split, check your PC's routing table w/ "route print" to see if server IP/subnet is there. The destinations have nothing to do with remote groups. It's decided by 1) routing (in case split) and 2) policy for ssl.root->internal interface.

    Nelvin
    NelvinAuthor
    New Member
    May 2, 2019

    Hi Toshi Esumi,


    Thanks for your suggestion.

    I didn't enable the split-tunnel function.

    And I checked and opened all the services in IPv4 policy, ssl.root --> Internal LAN.


    Finally, I found out the issue.

    My company network IP range is 192.168.1.X, internal server 192.168.1.254.

    Branch site router IP range also 192.168.1.X.

    Both network conflicted. 


    lotfi_boucherit
    New Member
    April 30, 2019

    I'm having same problem with an IPsec VPN.

    It is connected, but no traffic is working.

    Toshi_Esumi
    SuperUser
    SuperUser
    April 30, 2019

    This thread was for SSL VPN. Open a new case with a proper subject including a word "IPSec" and share the proper info about topology and config. Otherwise, nobody can't comment on with just "not working".

    Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
    Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
