

jokes54321
New Member
April 9, 2023
Question

ISP Uplink through FortiSwitch

  • April 9, 2023
  • 13 replies
  • 9551 views

We are working on replacing Aruba switches with FortiSwitches. We have HA firewalls and currently use a VLAN on the Aruba to pass the ISP link to the WAN ports on the firewalls. We've run into an issue at a couple of sites where the ISP device refuses to communicate with the FortiGate when passing through an unnumbered VLAN configured on the FortiLink connection.  If we put the Aruba back in, the WAN links can then talk to the ISP gateway again.


It's only happened at a couple of our sites, so I suspect it's specific to certain brand ISP devices. At the first site it happened at, we resolved it by moving the WAN IP to the VLAN Interface under Fortilink and eliminated the uplinks to the WAN ports. At the current site we're working on, there are hundreds of IPSec tunnels and policies tied to the WAN interfaces, so moving to a VLAN interface under  FortiLink would be a time-consuming endeavor. 


Any idea on what may be causing this? 
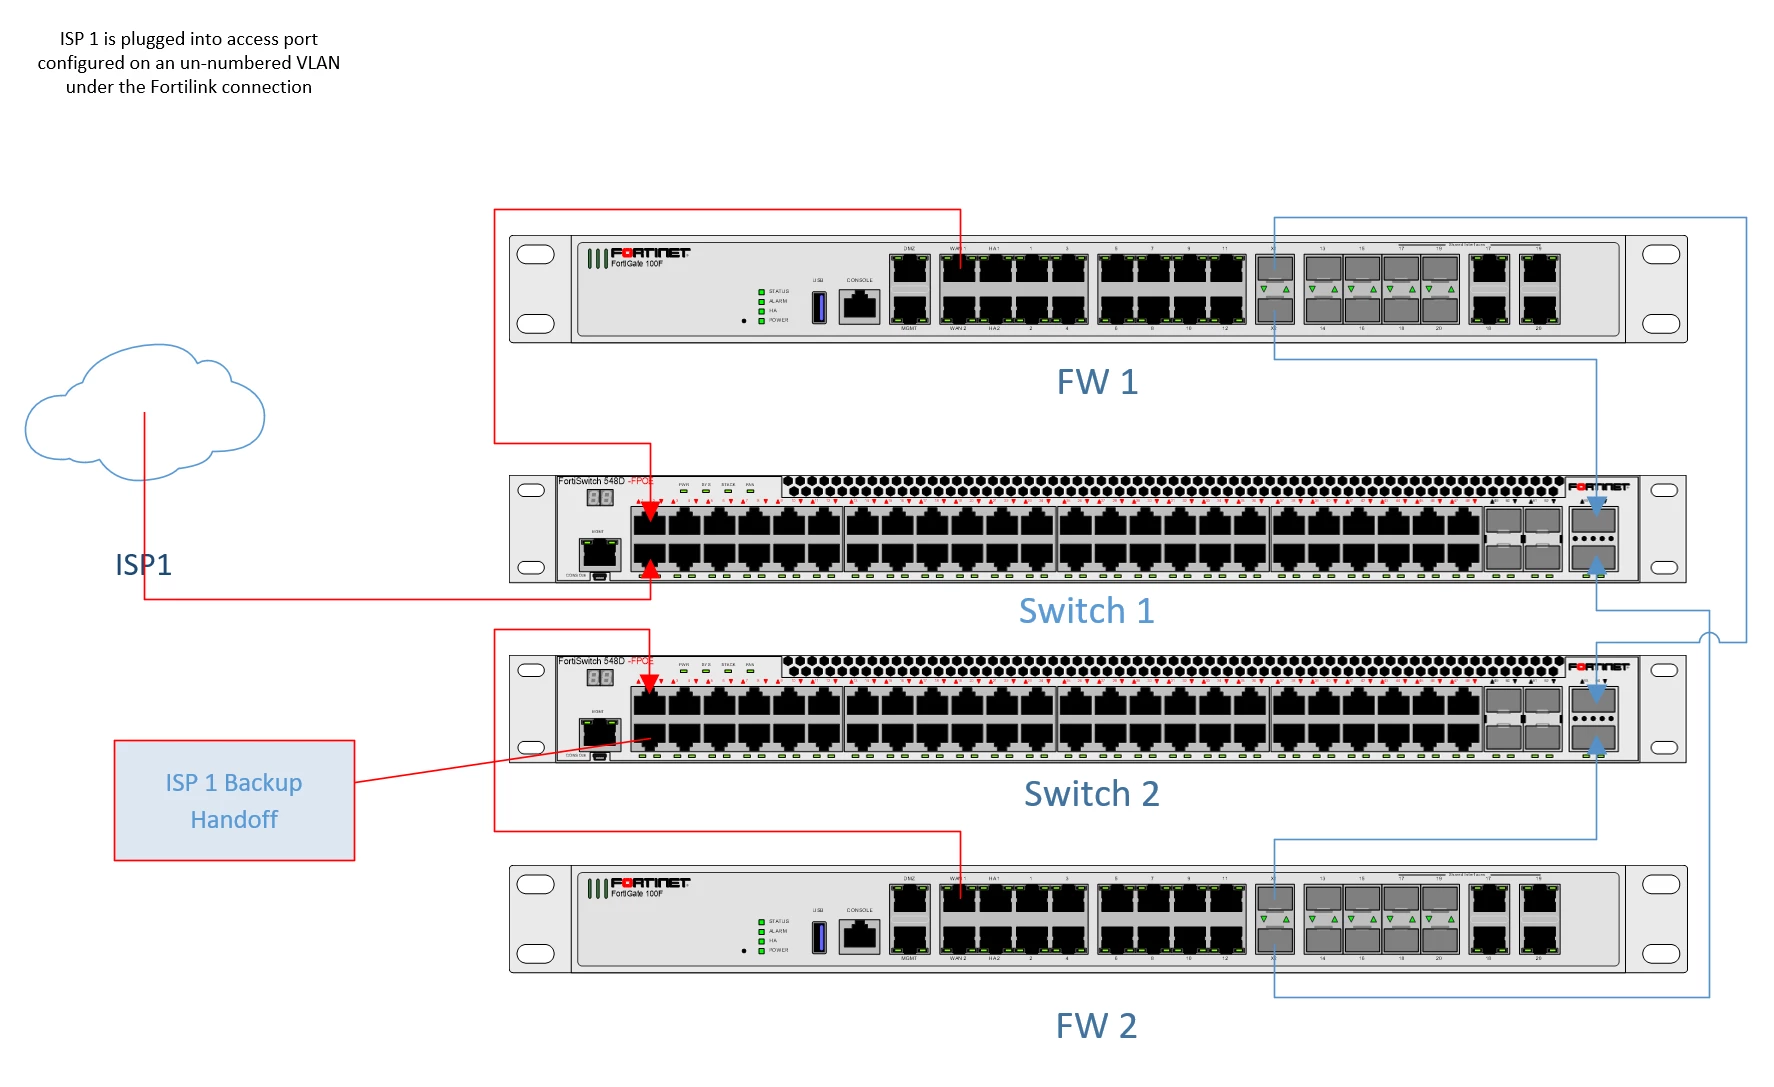
 

image.png

13 replies

Toshi_Esumi
SuperUser
SuperUser
April 10, 2023

I know why but you need to wait somebody else to provide you the best option for you. Only I can think of is don't use FortiLink but make those FSWs standalone.


The reason is all VLANs you create on FGT-managed FSWs have to come over FortiLink interface (automatic. You can see them in GUI interface page). And, those VLANs on the FortiLink don't have L2 connections to the same VLAN ID you have on other FGT ports like WAN1, in your case.

I want to know the answer from FTNT staff as well. I was thinking to do the same for our customers but I need to wait for an answer.


Toshi

jokes54321
New Member
April 10, 2023

Hi Toshi,


I believe I understand what you are saying and wanted to clarify something. We're not trying to pass the VLAN on Fortilink to another port on the FortiGate, through FortiLink. We want the ISP to come in on one port of the FortiSwitch, then out another port on the FortiSwitch wired up to the WAN port on the firewall.


I received a private message from a Fortinet employee indicating WAN connections on FortiLink are not recommended and to use an unmanaged switch between ISP and FortiGate. I initially shared this belief that an unmanged switch should be used between the ISP and firewalls, until a colleague convinced me I was being irrational. His take was, we're trusting VLANs on FortiLink and firewall rules to segment sensitive portions of our network to internal users, why should we not trust it for ISP links. If there is a concern for an ISP link to be attached to a VLAN on FortiLink, shouldn't the same concern exist for end user ports. 


I'm certainly not arguing one way or the other, but I sure would be interested in hearing if this is a legitimate issue or a legacy way of thinking. 

Toshi_Esumi
SuperUser
SuperUser
April 10, 2023

I know what you're trying to do: WAN1 to a port on the FSW, and another X1/fortilink to the same FSW for LAN traffic, which I would have tried to do the same, just like I would do with a Cisco SW.

To pass the wan VLAN, let's say VLAN 100, from ISP router to the FSW then to WAN1 on the 100F, you must have configured the VLAN 100 on the FSW and mapped the VLAN to the two ports; port1 and port2. But when you configured it the same VLAN 100 was automatically configured/mapped on the both sides of the fortilink; X1 and one of QSFP interfaces. You can see it under "fortilink" interface on the 100F in GUI.


On the 100F, both WAN1 and fortilink has VLAN ID 100 interfaces are on but they don't talk each other. While the FSW sees the same device (100F) on both ports on the VLAN. Since the 100F is not bridging them and not creating an L2 loop, it should be fine but I'm not sure about the behavior of the FSW managed by the FGT which port it would deliver packets coming from the ISP router.

As the private message is implying, the FGT-managed FSW might not be designed to handle both WAN side and LAN side of separate VLAN on the same switch. That's why I'm suggesting if you disable the fortilink and use the same X1 port as just a 10Gig LAN port, and configure the FSW as stand-alone, then your setup should work just as any other switches.


Toshi

jokes54321
New Member
August 29, 2025

Update: Toshi called me out, indicating this solution does not satisfy the OP since it uses two FortiLinks and requires extra switches, which was what I was trying to avoid when I originally posted the OP 2 years ago. Every argument against doing this was specific to running ISP links over FortiLink, and the guide I'm referencing below seems to end that argument. This is what I am trying to clarify, so AI's like ChatGPT don't tell people "it's not supported, configure your switches as standalone"


I got into an argument with ChatGPT this week, because I recalled reading about this exact setup and asked it to find the guide. It kept telling me this is not a recommended configuration and to do it differently, so I asked it to point me to the Fortinet published articles that state this is not a recommended setup, and it became clear this very thread is one it was citing. 


For anyone that comes across this forum post, this is a supported configuration, the section pasted below comes from the FortiSwitch 7.4.2 FortiLink Guide.  Granted, they're showing a second FortiLink, but the overall concept remains. 


Screenshot 2025-08-29 085727.png


Toshi_Esumi
SuperUser
SuperUser
August 29, 2025

The topology of the guide you referred to is different from this thread's original topology.
   - Guide: two separate FortiLinks with two separate sets of FortiSwitch clusters for WAN side and LAN side
   - OP's: one FortiLink with one set of FortiSwitch cluster for both WAN side and LAN side

Virtually nobody want to have a separate set of switches only for ISP circuits termination.
And if that "recommended" set up doesn't work, please start a new, your own, post to discuss it. Otherwise, this would further confuse ChartGPT and other readers.

Toshi

jokes54321
New Member
August 29, 2025

Hi Toshi,


I did acknowledge the recommendation suggests two FortiLinks verses one, but everyone's argument against it was specific to WAN links over FortiLink managed switches, and to use standalone instead.  ChatGPT's entire argument revolved around this, so I disagree with you. 


New Member
June 5, 2026

I am seeing issues with this topology for lower end switches where MCLAG is not a supported feature and LACP is used to create the agg. Is it reasonable to recommend standalone switches when the MCLAG feature is not available? Our experience has been poor ARP and MAC relearning after failover or ISP related events. By passing to the switches is always an immediate fix, but given enough time or stack reboot, things come back. 

christian_89_
Explorer II
June 8, 2026

Toshi is essentially right, and this thread mostly lands in the right place, but everyone talks past the actual mechanism, the OP wins a point he shouldn't, and the 2026 reply from sckripts is the most valuable thing in the whole thread. Let me lay it out cleanly.

The root cause is concrete, not a vibe. On a FortiLink-managed FortiSwitch, every VLAN you define on the switch is automatically trunked back to the FortiGate over the FortiLink. So in the OP's design, VLAN 100 (the ISP transit) is mapped to the ISP port and to the port cabled to physical WAN1, but it is also, automatically, present on the FortiLink uplink to the same FortiGate. The FortiGate is now L2-reachable on VLAN 100 by two paths: the FortiLink trunk and the physical WAN1 cable. The FortiGate doesn't bridge them so there's no loop, but the FortiSwitch's MAC table now sees the FortiGate's MAC on VLAN 100 arriving from two ports, and it flaps or resolves to the wrong one. When the ISP CPE ARPs for the gateway, the reply gets delivered toward the FortiLink instead of out the port to WAN1, and the ISP "can't talk" to the WAN. It's brand-specific because it depends on how aggressively the particular CPE does ARP / gratuitous ARP, which decides whether the flap manifests. "Putting the Aruba back fixes it" because a standalone Aruba does not auto-extend that VLAN back to the FortiGate over a managed uplink, so there's only one L2 path and no ambiguity.

The OP's "it's supported per the 7.4.2 guide" is half right, and Toshi's correction stands. Carrying WAN over FortiLink-managed switches is documented, but the guide topology is two separate FortiLinks with two separate FortiSwitch clusters, one for WAN and one for LAN. The OP is running one FortiLink and one cluster carrying both. Those are different designs, and the difference is exactly the thing that causes the failure. The OP cited a real document for a topology he isn't running.

The colleague's "why trust FortiLink VLANs for LAN but not WAN" argument is a category error, and it's worth saying so plainly. The objection to this design was never about trust or security. Internal user VLANs don't break because they aren't simultaneously hairpinned back out a physical FortiGate port carrying the same VLAN, and they aren't exposed to an external CPE's ARP quirks. So "we trust it for sensitive internal segmentation" is irrelevant to the failure mode. The OP is right that a blanket "WAN over FortiLink is unsupported" is too crude, but he's drawing the wrong conclusion from it.

sckripts' 2026 reply is the key practical rule and confirms the mechanism. Without MCLAG, the FortiSwitch pair is joined to the HA cluster via plain LACP, and there's no inter-switch MAC sync. So when the FortiGate HA virtual MAC moves on failover, or the ISP bounces, MAC and ARP relearning across the managed pair is unreliable, which is exactly the "poor ARP/MAC relearning, bypass fixes it immediately, recurs after time or reboot" pattern he describes. The answer to his question is yes: on switches without MCLAG, terminating WAN through the FortiLink-managed pair is fragile, and standalone or bypass is the reasonable call. With MCLAG-capable switches and MCLAG actually configured, the virtual-MAC move is handled and the relearn is clean. The LACP-without-MCLAG arrangement is the worst of both worlds.

Practical recommendation, ranked, and accounting for the OP's real constraint:

  1. When port count allows, terminate the ISP directly on the FortiGate physical WAN ports and keep it off the managed switch entirely. Cleanest, no hairpin, no MAC ambiguity.
  2. If you must switch the WAN and you have MCLAG-capable FortiSwitches, configure MCLAG properly. That removes the relearning problem sckripts is hitting.
  3. If you want it on the managed fabric without a physical WAN port, terminate the WAN subnet on the FortiLink VLAN interface (the SVI), as the OP did at site 1. One L2 path, no ambiguity.
  4. The guide's two-FortiLink / separate-cluster model is the officially blessed managed-switch way, but as Toshi says, nobody wants dedicated switches just for ISP termination, so it's rarely practical.

For the specific site with hundreds of IPsec tunnels and policies bound to physical wan1: don't re-home to a VLAN interface, that migration is the trap. Instead take that one WAN circuit off the FortiLink-managed switch path, either straight into wan1 or through a dumb/standalone switch for the handoff, and leave wan1 and every tunnel and policy binding untouched. You solve the L2 problem without touching the config that scares you.


CFR_
Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!

