


Joseph-M
New Member
June 20, 2023
Solved

IPSEC tunnels not working when specified the Local Gateway

  • June 20, 2023
  • 10 replies
  • 5719 views

After upgrading our FortiGate to v7.4.0 from 6.4.7 (with optional upgrade path 6.4.9 then 6.4.11 ...)


All our IPSEC tunnels are down and phase1 and phase2 are down. At the same time all other config seems to be in place...
2023_06_20_13_48_04_FortiGate_FortiGate_and_23_more_pages_Work_Microsoft_Edge.png

We found out that as soon as we choose local gateway "Specify" (our secondary WAN IP) not "Primary IP" the tunnel is down and no communication is happening between our and client FW (all WAN IPs are from one ISPs GW). We can ping clients IP.


Proposals and configuration of P1 and P2 are correct, as I mentioned as soon both sides chooses gateway (our primary IP) tunnel works. Policies are in place, traffic is accesable from both sides when tunnel is up. Routes created.


What could be the possible issues where to look. I tried to find similar issues on forums but no success. Would appreciate any ideas and help.




Best answer by Joseph-M

Ticket were created for FortiSupport.

10 replies

srajeswaran
Staff
Staff
June 20, 2023

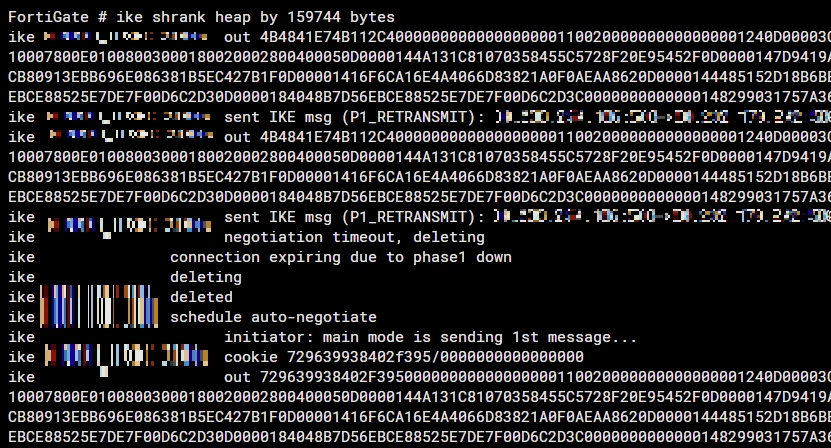
As per the debug there is no response from peer, since the configuration was working previously it could be related to route.


Can you share below output.

get router info routing-table details x.x.x.x ->peer ip

get router info kernel | grep x.x.x.x


Joseph-M
Joseph-MAuthor
New Member
June 20, 2023

# get router info routing-table details x.x.x.x (peer IP)

Routing table for VRF=0
Routing entry for 0.0.0.0/0
Known via "static", distance 10, metric 0, best
* vrf 0 x.x.x.x, via wan1


(output x.x.x.x shows our ISP gateway address)

-----------------

# get router info kernel | grep x.x.x.x (peer IP)

no output

srajeswaran
Staff
Staff
June 20, 2023

is wan1 your VPN external interface?

Can you collect sniffer

diagnose sniffer packet any "host x.x.x.x" 4 100

Joseph-M
Joseph-MAuthor
New Member
June 20, 2023

Yes WAN1 is our external interface


wan1 in x.x.x.x -> x.x.x.x: udp 292
wan1 out x.x.x.x.500 -> x.x.x.x: udp 292
wan1 out x.x.x.x -> x.x.x.x: icmp: host x.x.x.x unreachable
wan1 in x.x.x.x -> x.x.x.x: udp 292
wan1 out x.x.x.x.500 -> x.x.x.x: udp 292
wan1 out x.x.x.x -> x.x.x.x: icmp: host x.x.x.x unreachable
wan1 in x.x.x.x -> x.x.x.x: udp 292
wan1 out x.x.x.x.500 -> x.x.x.x: udp 292
wan1 out x.x.x.x -> x.x.x.x: icmp: host x.x.x.x unreachable

wan1 out x.x.x.x -> x.x.x.x: icmp: host x.x.x.x unreachable

wan1 out (PrimaryIP) -> (PeerIP): icmp: host (SpecifiedIP) uncreachable


Specified IP is the one we want to use in our ipsec configuration 


there is som 500 packets becouse it tries to establish IPsec tunnel. 

what is interestings the ICMP timeouts

Joseph-M
Joseph-MAuthorAnswer
New Member
June 26, 2023

Ticket were created for FortiSupport.

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!