

DirkDuesentrieb
New Member
May 7, 2024
Question

IPSEC Tunnel goes down after scheduled Fortiguard update

  • May 7, 2024
  • 2 replies
  • 1218 views

Hi,

we are having a strange VPN problem with one IPSEC tunnel of a remote site. All other sites work fine. But this 200F sometimes looses VPN connectivity directly after a scheduled FortiGuard update. This can be seen in the sites eventlog, where the FAZ connection through the tunnel is lost seconds after the update message. The phase2 seems to be broken at that time and the tunnel finally recovers after more than an hour and the FAZ is reachable again. 
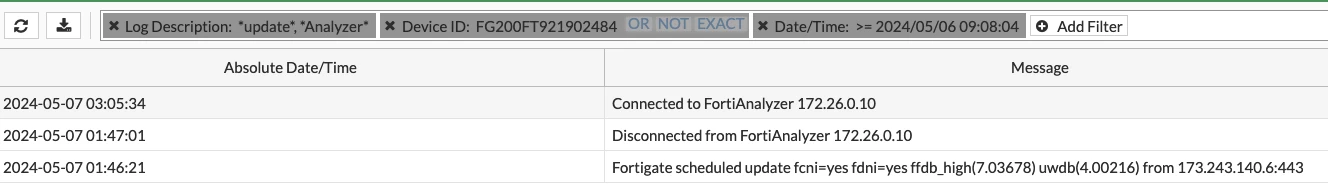
 

event log.png


There is nothing special at this site and all gatways use the same FOS7.0.15.
Have you seen this or have any ideas?

Regards,

Dirk

2 replies

hbac
Staff
Staff
May 7, 2024

Hi @DirkDuesentrieb,


Have you seen high CPU/Memory at that time? You can run this command 'di deb crashlog read' to see if there was any crash.


Regards, 

DirkDuesentrieb
New Member
May 7, 2024

Hi @hbac 
the central SNMP monitoring has a gap during that time, because it needs the tunnel to poll data, so I need to improvise here.
- The local eventlog writes perfmon data every 5 minutes; all with "CPU: 0".
- The "Memory"-widget shows data of the last 24 hours and has no peaks

I found a dump of the dhcpd in the crashlog, but this is unrelated to the event.

Dirk

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!
