



IP Pools using secondary IP
Hi,
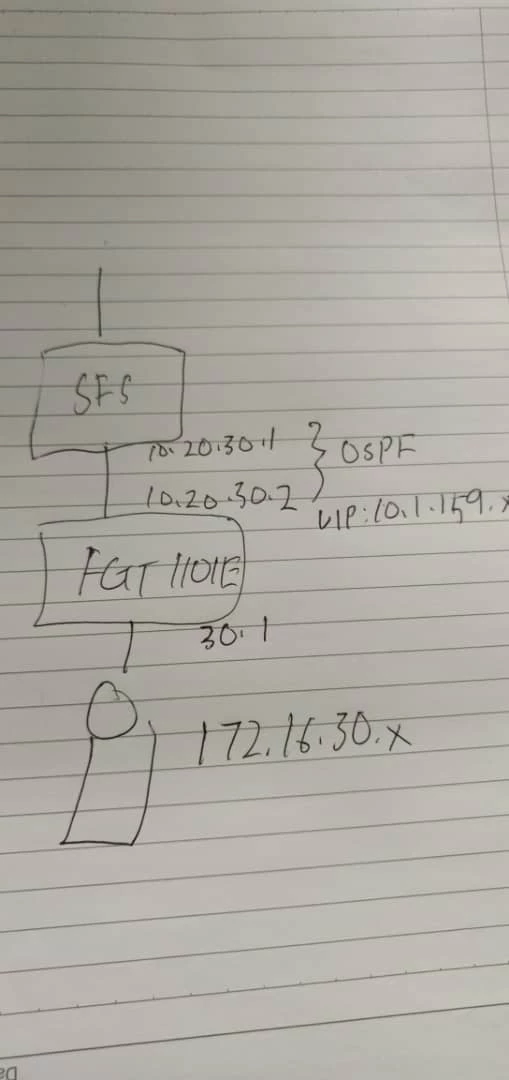
Referring to the diagram attached, FGT is connected to the upstream server farm switch with OSPF (10.20.30.2).
The interface configuration is as below:
WAN: 10.20.30.2 (OSPF interface)
LAN: 172.16.30.1
We would like to configure VIP at the internal FortiGate with IP segment 10.1.159.0/24 at the WAN interface and mapped it to the internal server.
We had tested the VIP at our labs and it is working as intended.
However, we are having some suspicious about whether the server can go to the internet or not with this configuration.
Sample config:
config system interface
edit "LACP-WAN"
set vdom "Int"
set ip 10.20.30.2 255.255.255.252
set allowaccess ping
set type aggregate
set member "internal5"
set device-identification enable
set lldp-transmission enable
set monitor-bandwidth enable
set snmp-index 49
set secondary-IP enable
config secondaryip
edit 1
set ip 10.1.159.254 255.255.255.0
set allowaccess ping
next
end
next
end
config firewall ippool
edit "Pool-25"
set startip 10.1.159.25
set endip 10.1.159.25
set comments "Test Server 01"
next
end
config firewall policy
edit 1
set name "Pool2ndIP"
set uuid 26ae67a4-81cd-51ec-4cb0-d7a20a187547
set srcintf "LACP-LAN"
set dstintf "LACP-WAN"
set srcaddr "servertest"
set dstaddr "all"
set action accept
set schedule "always"
set service "ALL"
set ippool enable
set poolname "Pool-25"
set nat enable
next
end
The objective is to allow the internal server to go to the internet with NATting to 10.1.159.254 or any other IP Pools within the 10.1.159.254 segment. Please advise if it is doable.
Thanks.
Regards,
Umar

