IKEv2 with iOS 9
Hi.
We have a problem on a Fortigate 100D with 5.2.4.
We trying to set up a IPSec VPN with IKEv2 to connect our iPhone/iPads with iOS 9.x to use the new iOS 9 Feature "per App VPN". To do that we need to use the IKEv2.
The fortigate config:
config vpn ipsec phase1-interface edit "IKEv2" set type dynamic set interface "wan1" set ike-version 2
set peerid "1"
set mode-cfg enable
set ipv4-dns-server1 10.1.4.23 set ipv4-start-ip 10.3.0.76 set ipv4-end-ip 10.3.0.100 set ipv4-netmask 255.255.255.0 set psksecret ENC ........ next end
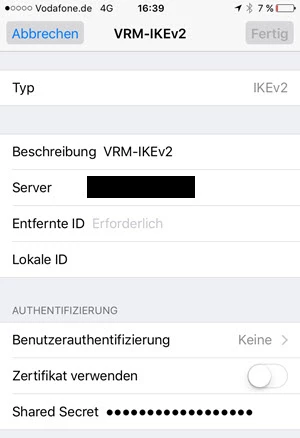
On the iPhone is the field "Remote ID" is marked as required? What to enter here? The fortigate peerid? When I do that, I get a "Phase 1 failure" in the fortigate log. Could someone please give me a hint?
iPhone IKEv2 Settings: