

yonibar81
New Member
March 3, 2017
Solved

I can't connect HP vlan to Fortigate

  • March 3, 2017
  • 24 replies
  • 43685 views

Hello

i have fortigate 80c and hp switch 1910.

my network (internal 1 ) working with 172.26.30.254/255.255.255.0.

now i created on hp switch vlan 100 with interface 172.26.0.1/255.255.0.0.

how can i connect vlan 100 to my fortigate ?
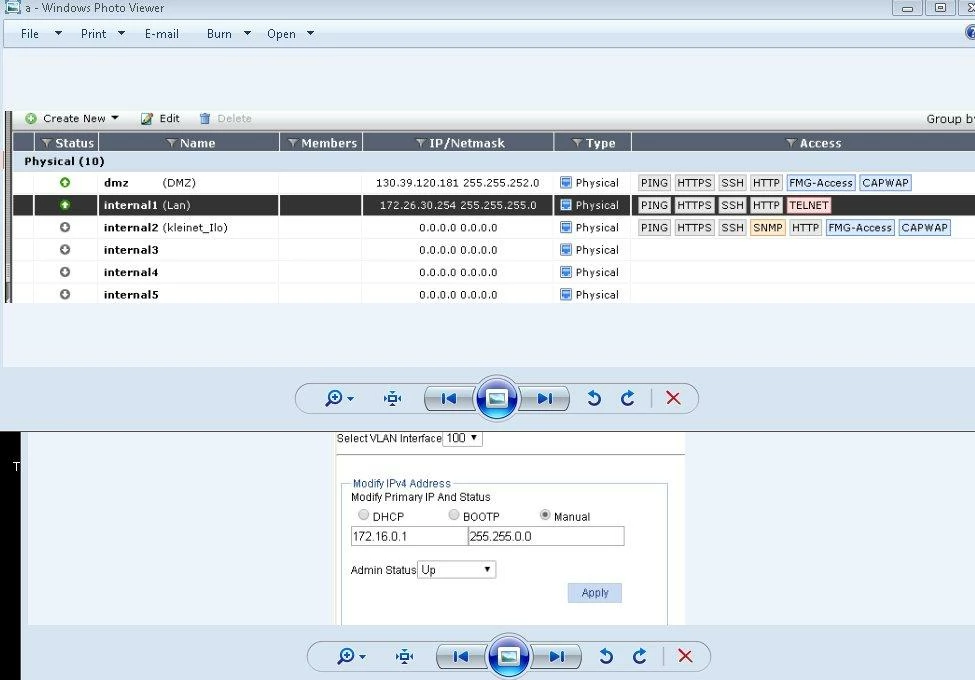


    Best answer by MikePruett

    You need to select that port that you have connected to the switch (under network interfaces) then click "new" and go to vlan.


    The Gate won't listen to a vlan using just the port being connected unless it is the default vlan of the switch. Since 100 isn't, you need to have a vlan100 configured on the physical interface of the Gate as well (which means you will get a drop down on internal1 for vlan100).

    24 replies

    MikePruett
    New Member
    March 3, 2017

    You need to select that port that you have connected to the switch (under network interfaces) then click "new" and go to vlan.


    The Gate won't listen to a vlan using just the port being connected unless it is the default vlan of the switch. Since 100 isn't, you need to have a vlan100 configured on the physical interface of the Gate as well (which means you will get a drop down on internal1 for vlan100).

    ede_pfau
    SuperUser
    SuperUser
    March 3, 2017

    Could you please explain why you define overlapping address ranges?

    You won't be able to configure that on the FGT, and for good reasons.

    yonibar81
    yonibar81Author
    New Member
    March 5, 2017

    i created vlan on hp switch and i want to connect to FW

    yonibar81
    yonibar81Author
    New Member
    March 5, 2017


    i did it but i do not ping to firewall 172.26.30.254.

    see my rules on attached

    dennisv
    New Member
    March 16, 2017

    There are two ways of connecting the HP switch to the Fortigate with VLANS.

    1) Put the switch port on vlan 100 in untagged mode.

    You do not need to configure a sub-interface on the Fortigate.

    The IP adres of the Fortigate should be in the same range as the IP adress on the vlan 100.

    (example fortigate 192.168.100.1/23 , switch 192.168.100.2/24)


    2) Put the switch port on vlan 100 in tagged mode

    Create a sub-interface on the physical port you are connecting the switch

    Set the ip adress in the same range as the IP adress of the switch in vlan 100

    (example fortigate 192.168.100.1/23 , switch 192.168.100.2/24)


    In both cases make sure the management access of the interface is set to ping.

    This will allow ping to the Fortigate without any additional policy.


    azwanarif
    New Member
    July 10, 2019

    Hi All,

    I know this is old post, recently we deploy fortigate to customer which still using the same HP switch and encounter the same issue.

    I have follow the steps and work successfully. However I would like to know why we need to tagged the switch  in order to connect with fortigate which for HP all end devices required to use untagged port?. Thanks

    dennisv
    New Member
    July 15, 2019

    Yes this seems like a configuration issue on the iDRAC side.

    You mentioned :

    "we already spoke with the server vendor and verified that only IP and gateway without vlan is configured."

    This implies the traffic from iDRAC to be untagged and HP port 1-18 should be set to untagged vlan 10.

    But in a previous post you mentioned that iDRAC was setup with vlan 10 inside iDRAC, which implies HP port 1-18 should be set to tagged vlan 10.

    Make sure you contact the server administrator and have them verify (screenshots) the proper iDRAC settings.


    Anyway, you are on the right path now and it seems the connection between the HP switch and Fortigate is ok.

    If you need any additional help with this connection, just reply to this thread and ill get a notification.

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!

