

storaid
New Member
June 22, 2015
Question

how to give the ON-Net status to DHCP client via external DHCP server??

  • June 22, 2015
  • 18 replies
  • 29939 views

hello, fortinet and everyone...

I know using code 224 option sends S/N to DHCP client and make client using FCT keep On-Net status...

but it's good working only for dhcp server function with fortigate...


I'm using windows dhcp server...

the windows dhcp server does not send it to client during dhcp prcoess even if you added this option on DHCP Standard options by setting predefined options ....

the code 224 option is not dhcp standard option, it's just a private-use option...
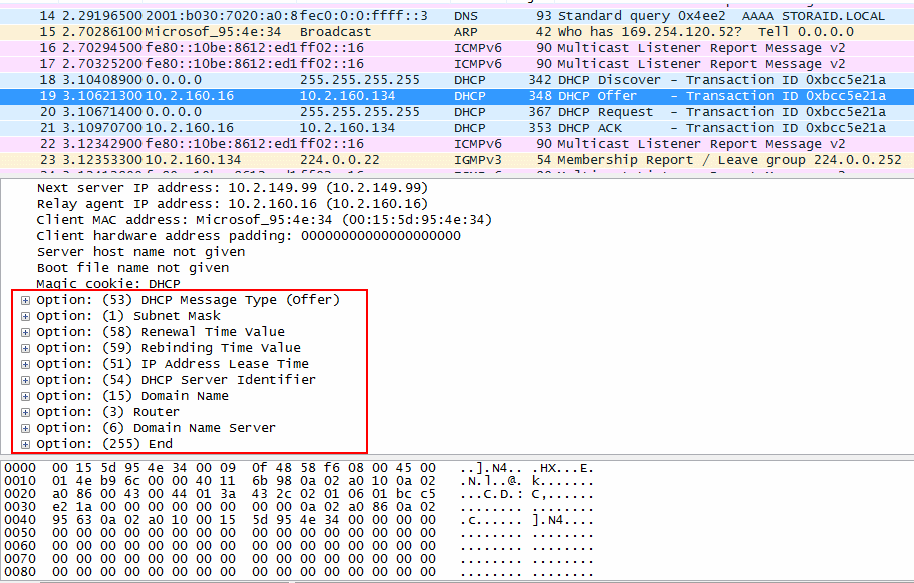
my question is

how to send this option which belong to a set of vendor-specific extension to dhcp client???

    18 replies

    Christopher_McMullan
    Staff
    Staff
    June 22, 2015

    The DHCP option 224 should work with Windows servers acting as a DHCP server. Which version is running - 2008 R2 or 2012? With 2012, you would enter the FortiGate S/N in regular text, but 2008 R2 requires you to enter it in hex.

    storaid
    storaidAuthor
    New Member
    June 22, 2015

    Christopher McMullan_FTNT wrote:

    The DHCP option 224 should work with Windows servers acting as a DHCP server. Which version is running - 2008 R2 or 2012? With 2012, you would enter the FortiGate S/N in regular text, but 2008 R2 requires you to enter it in hex.

    OS: WINDOWS 2012...

    "The DHCP option 224 should work with Windows servers acting as a DHCP server. "

    option 224 is not standard option...

    you sure the option 224 is included in the dhcp offer message for windows 2012???

    "With 2012, you would enter the FortiGate S/N in regular text, but 2008 R2 requires you to enter it in hex."

    I use the wireshark to check dhcp handshake...

    I don't find option 224 was sent to the dhcp client...


    for built-in dhcp server function with fortigate, I have confirmed this option was definitely sent to the client....


    Christopher_McMullan
    Staff
    Staff
    June 22, 2015

    It's been a while since I had to define the Windows scope options myself, but...


    In Server 2012 it should be possible this way:

    Under the DHCP MSC, with the server name expanded, right-click on IPv4 and choose Set Predefined Options, and Add on the detail window. Add option 224 with an Option name like 'FGT' with a Byte value for Data Type. Then, back under Predefined Options, select DHCP Standard Options as the Option class, '224 FGT' as the Option name, and the S/N of the FortiGate as the string.

    storaid
    storaidAuthor
    New Member
    June 22, 2015

    Christopher McMullan_FTNT wrote:

    It's been a while since I had to define the Windows scope options myself, but...


    In Server 2012 it should be possible this way:

    Under the DHCP MSC, with the server name expanded, right-click on IPv4 and choose Set Predefined Options, and Add on the detail window. Add option 224 with an Option name like 'FGT' with a Byte value for Data Type. Then, back under Predefined Options, select DHCP Standard Options as the Option class, '224 FGT' as the Option name, and the S/N of the FortiGate as the string.

    Sorry..

    are you sure the data type is Byte????..

    Christopher_McMullan
    Staff
    Staff
    June 22, 2015

    No, I'm not really sure, to be honest. I know the feature works. I was providing some best-effort steps to help configure the scope properly, but we're veering well into configuration details that are specific to Windows Server.


    Is there no way you've found to work when configuring the option *roughly* the way I've described?

    storaid
    storaidAuthor
    New Member
    June 22, 2015

    Christopher McMullan_FTNT wrote:

    No, I'm not really sure, to be honest. I know the feature works. I was providing some best-effort steps to help configure the scope properly, but we're veering well into configuration details that are specific to Windows Server.


    Is there no way you've found to work when configuring the option *roughly* the way I've described?

    I don't know how can I input the string text for Byte type????


    storaid
    storaidAuthor
    New Member
    June 22, 2015

    well, looks like the problem is windows dhcp server does not send all otpions..

    most solutions I found is using option 43 VCI to write additional messages...

    but it is useless for my case...

    now this problem kicks my ass..:(


    Christopher_McMullan
    Staff
    Staff
    June 23, 2015

    Try adding the option as type String instead of Byte.

    storaid
    storaidAuthor
    New Member
    June 23, 2015

    Christopher McMullan_FTNT wrote:

    Try adding the option as type String instead of Byte.

    yesterday I have tried it as your mentioned...

    but I don't think that's a problem...

    the problem is windows dhcp server does not send all options I added....


    Christopher_McMullan
    Staff
    Staff
    June 24, 2015

    I personally don't have any more answers about that.


    Opening the question up to the wider (monitoring) community...


    Otherwise, there's always Stack Exchange.

    storaid
    storaidAuthor
    New Member
    June 24, 2015

    Christopher McMullan_FTNT wrote:

    I personally don't have any more answers about that.


    Opening the question up to the wider (monitoring) community...


    Otherwise, there's always Stack Exchange.

    hello, I don't understand why...

    but now dhcp client can correctly receive option 224 from dhcp server...


    dhcp client<==> FSW224B-POE<==>FGT200B-POE

    dhcp server<=====||

    I just try the following steps:

    1. enable dhcp snooping (default: diabled)

    2. disable dhcp snooping, again

    3. done, and test again..


    ylemage_FTNT
    Staff
    Staff
    August 31, 2015

    Hi,


    Any idea what the value should be in case of a FortiGate cluster? We are talking about 2 SN's. Can we put both? How should they be seperated?


    Brgds

    Yves

    kolawale_FTNT
    Staff
    Staff
    September 2, 2015

    Put both FortiGate serial numbers in the configuration. The separator is either space or semicolon.

    --

    Consider creating a new Forum posting when your question is different from the original posting (as in this case).

    mstenner
    New Member
    November 4, 2015

    Hi,


    I am experiencing a similar issue. Did you manage to resolve?


    Thanks,


    Martin

    bgillon
    New Member
    November 23, 2017

    Dear,


    can you explain how to configure dhcp option on windows server ?

    did you have create string, byte array ?

    i try with my serial number of (Fortigate or FortiEMS) but on-net is not detected by forticlient ?


    regards

    mstenner
    New Member
    November 24, 2017

    1. Set a predefined option for each DHCP server of Option ID 224 with a name of FortiClientStatus. It needs to be a string and an array (select the tickbox).

    For the array values, enter the serial number(s) of your FortiGates.

    2. Apply the new option to the required scope.


    See screenshot for example.

    bgillon
    New Member
    November 24, 2017

    perfect.

    it's works ;)

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!
