

Lipe79
New Member
May 13, 2020
Solved

High Availability between 2 Fortigates 301E connected to 2 ISP links ?

  • May 13, 2020
  • 10 replies
  • 12459 views

Hi everyone! 


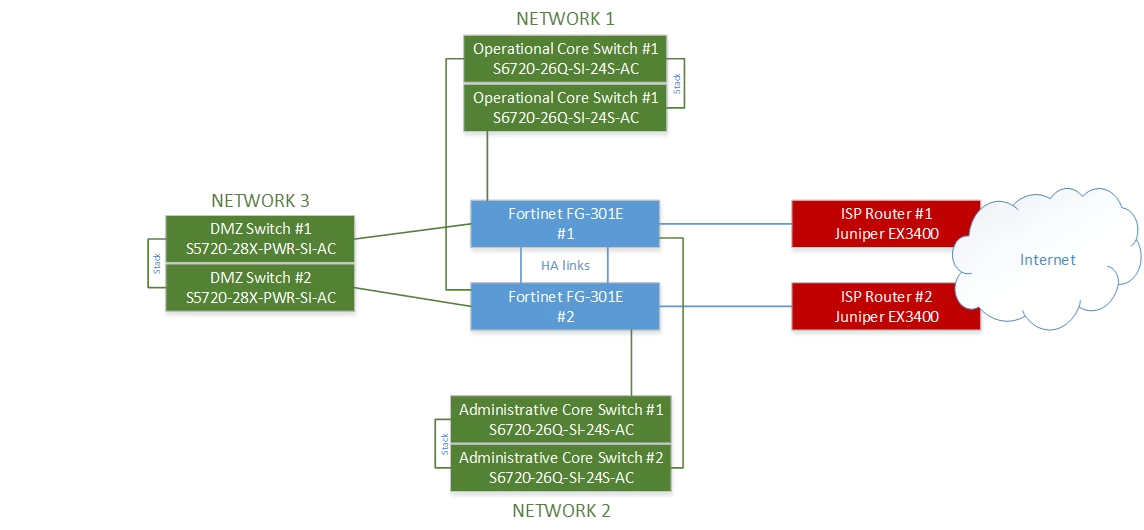
I need your precious help about this scenario, please see attached diagram below.


What do you recommend as being the best way to configure HA on these 2 Fortigates to work properly?

Active-Active or active-passive

Each one of the Firewalls is connected to ISP through only 1 link and the ISP is the same but has configured VRRP between ISPRouter1 and ISPRouter2.


Thank you so much!  Regards!
    Best answer by James_G

    The centralised vdom in in an HA pair, it should never be down, and doesn't matter what node it's running on

    10 replies

    lobstercreed
    New Member
    May 19, 2020

    Based on the info provided, I don't think you'll see any difference either way.  Just make sure the link to the ISP router uses the same port on both FortiGates.


    See here for a list of best practices for HA:

    https://help.fortinet.com/fos50hlp/54/Content/FortiOS/fortigate-high-availability-52/HA_FGCP_best_practices.htm


    This link specifically addresses the difference between AA and AP:

    https://help.fortinet.com/fos50hlp/54/Content/FortiOS/fortigate-high-availability-52/HA_FGCP_ap_aa.htm

    Lipe79
    Lipe79Author
    New Member
    June 15, 2020

    Hi Lobstercreed,


    Thank you for your help, I have configured active-passive mode but now I have a problem regarding this scenario I need to force the wan link to down when other interface that is being monitored goes down because the fortigate1 is changing the service to fortigate2 but the WAN interface stays up and the ISP Router are not changing to Router 2 when a failure occurs on another interface.


    What is the best way to accomplish this?


    Thank you so much!


    Regards, 

    Filipe

    lobstercreed
    New Member
    June 15, 2020

    The typical solution is to put a switch between the HA cluster and each ISP router, creating a mesh.   You can use a couple of cheap unmanaged switches for this purpose to avoid a single point of failure.


    This will give you some additional redundancy in case ISP1 fails at the same time FG2 fails, then ISP2 can still talk to FG1. 


    It should also address your scenario where FG1 goes down (artificially due to monitored interface)...you'll still be able to use ISP1.


    You may need to configure a couple additional interfaces on the firewall depending on how you set it up.

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!

