



Fortiwifi 60C to Checkpoint IPSEC VPN Phase 1 Issues
Hi All,
I am having an issue trying to get a Site-to-Site VPN up and running between a Fortiwifi 60c and a Checkpoint firewall. I have triple checked the settings and they are all correct (See images below). The first image is the checkpoint firewall and the second is the fortiwifi 60c. I am getting a phase one policy mismatch. The engineer I am working with says he doesn't see anything in his logfiles that even indicate that I am trying to connect, but I get the following in the Fortiwifi VPN logs:
date=2021-11-19 time=09:52:36 logid=0101037128 type=event subtype=vpn level=error vd="root" logdesc="progress IPsec phase 1" msg="progress IPsec phase 1" action=negotiate remip=199.253.xxx.xxx locip=67.53.xxx.xxx remport=500 locport=500 outintf="wan1" cookies="40b9e860259787fa/0000000000000000" user="N/A" group="N/A" xauthuser="N/A" xauthgroup="N/A" assignip=N/A vpntunnel="N/A" status=failure init=remote mode=main dir=inbound stage=1 role=responder result=ERROR
date=2021-11-19 time=09:52:36 logid=0101037124 type=event subtype=vpn level=error vd="root" logdesc="IPsec phase 1 error" msg="IPsec phase 1 error" action=negotiate remip=199.253.xxx.xxx locip=67.53.xxx.xxx remport=500 locport=500 outintf="wan1" cookies="40b9e860259787fa/0000000000000000" user="N/A" group="N/A" xauthuser="N/A" xauthgroup="N/A" assignip=N/A vpntunnel="N/A" status=negotiate_error reason="peer SA proposal not match local policy" peer_notif="NOT-APPLICABLE"
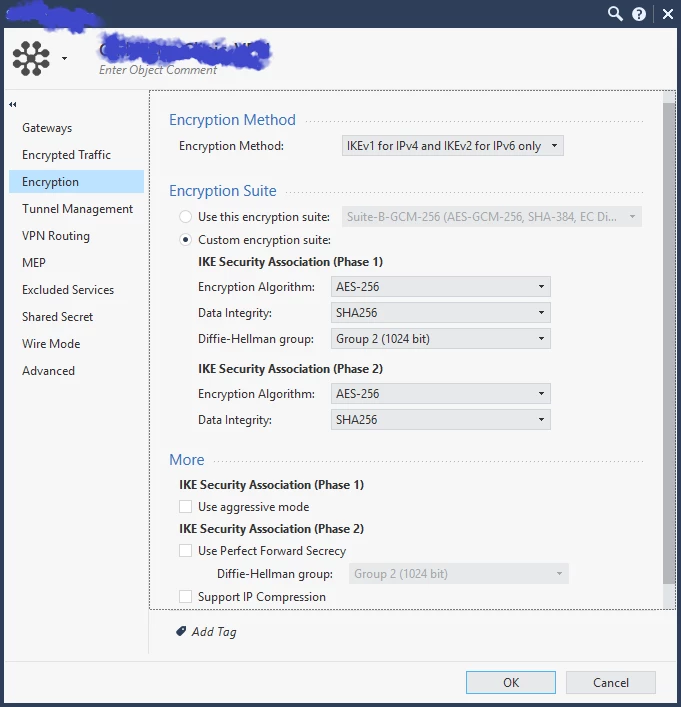
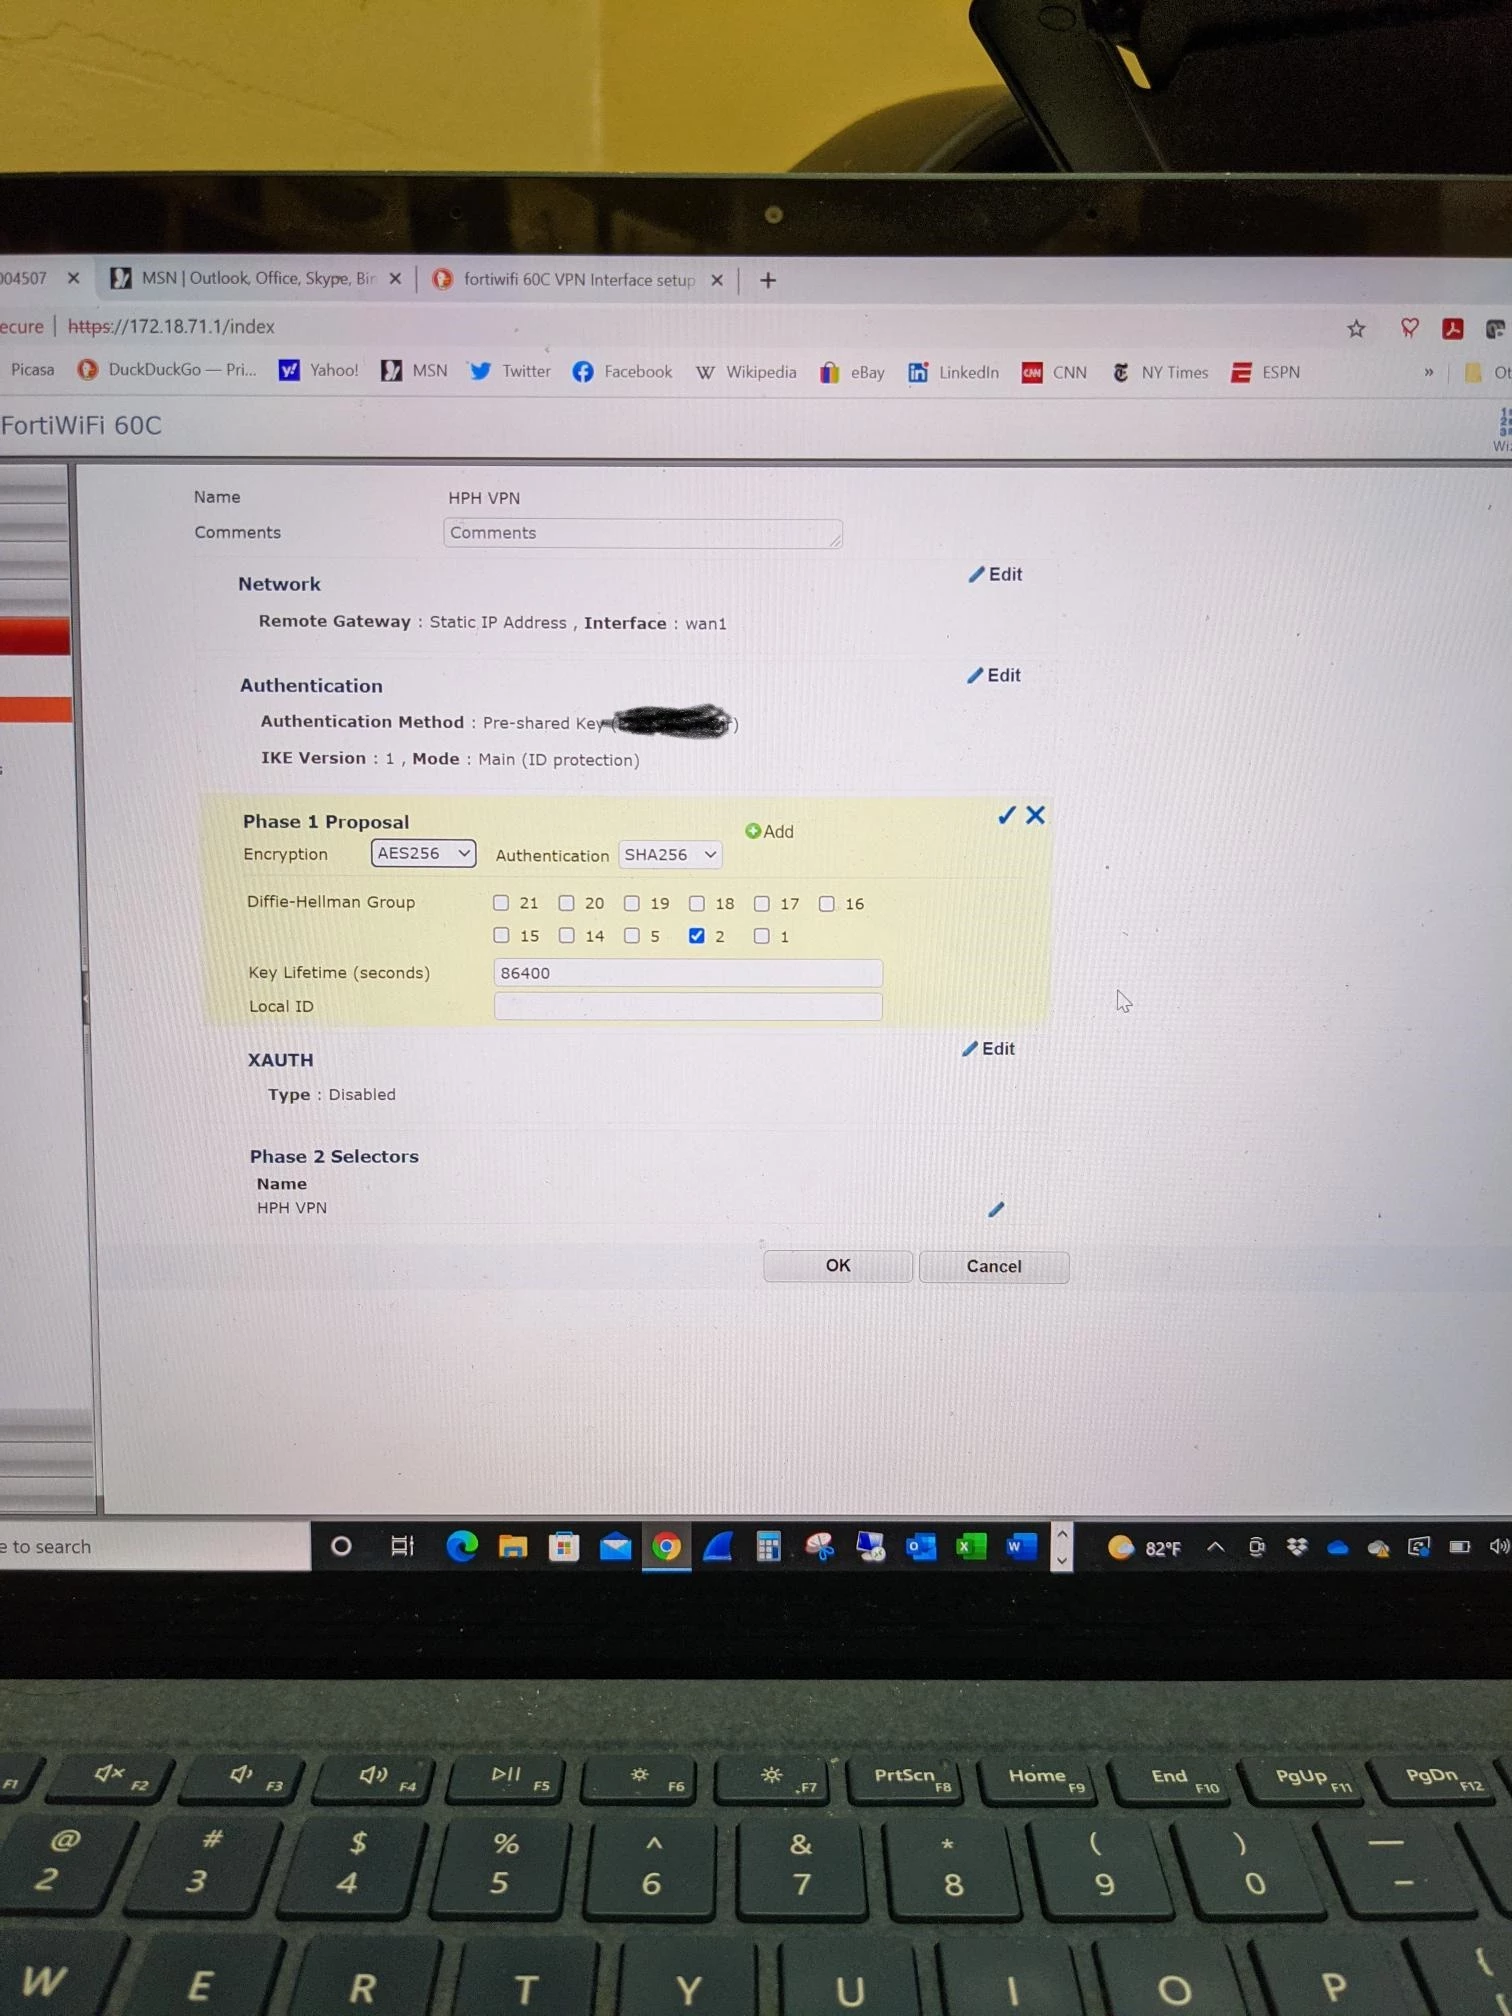
If anyone has any input that they think would be useful, I would appreciate it if you'd drop it below.
TIA
Don

