Solved
FortiWeb detecting Wordpress as XSS
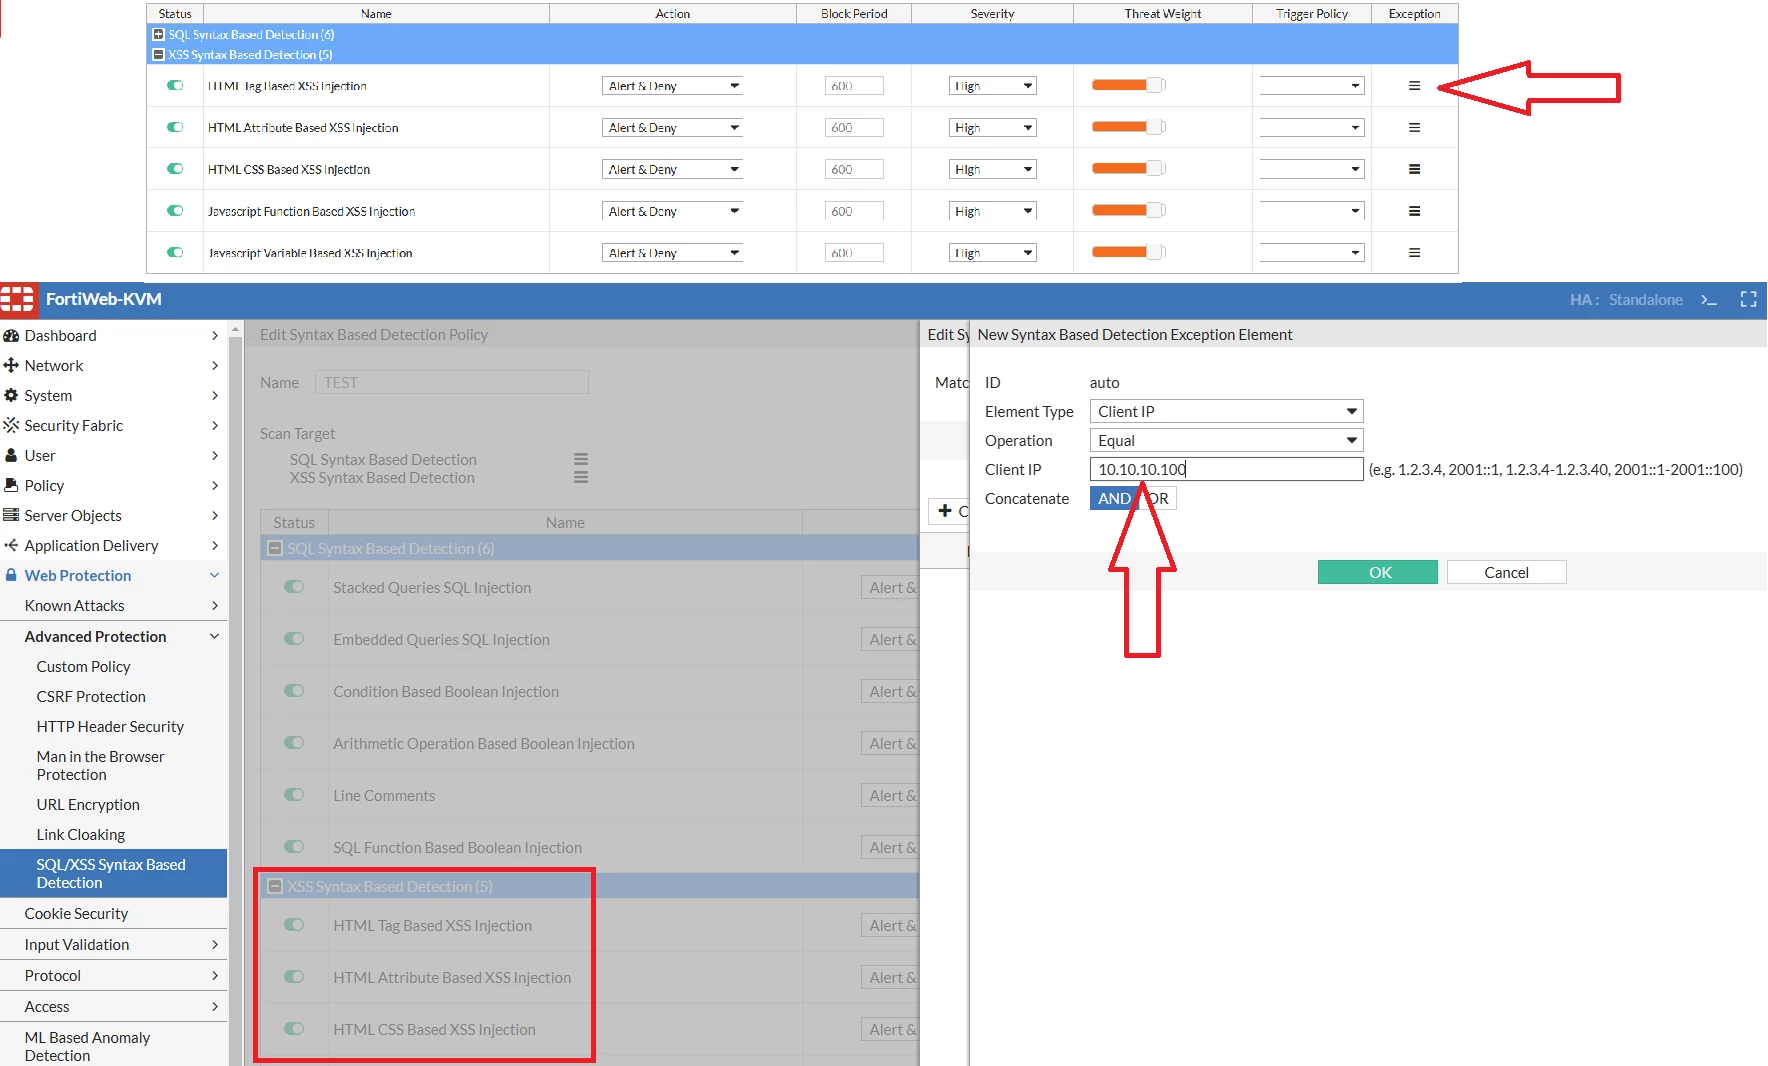
We got a team who manage the content of our corporate website. And everytime the push or publish their design/changes via wordpress. The fortiweb detected it as XSS.
Is there a way to exempt the user ip source for any XSS detection or any better approach to fix this.