


FortiSwitch Dynamic Port Policy – Dynamic VLAN not flushed immediately after legitimate device is disconnected
I have configured a FortiSwitch Dynamic Port Policy (DPP) to allow only 3 specific MAC addresses on a switch port. When one of the legitimate MAC addresses is connected, the DPP identifies the device and assigns the configured dynamic VLAN successfully.
However, I am experiencing an issue when the legitimate device is disconnected and an unauthorized device is connected to the same port shortly afterward.
My test scenario is:
- Connect legitimate device (Test_MAC1).
- DPP identifies Test_MAC1 and assigns the dynamic VLAN.
- Test_MAC1 is disconnected from the switch port.
- Within a few seconds, connect an unauthorized device (Test_MAC4).
- Test_MAC4 is not included in the DPP allowed MAC list.
- However, Test_MAC4 still receives an IP address from the previously assigned dynamic VLAN and can access the network.
It appears that the dynamic VLAN assignment/state is not being flushed immediately when the legitimate device is removed from the port.
Is there any way to Fix this?
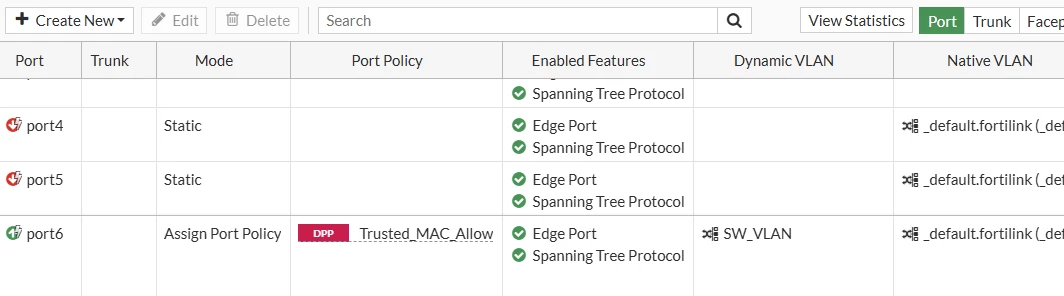
Dynamic port policy Configuration
config switch-controller dynamic-port-policy
edit "fortilink"
set description ''
set fortilink "fortilink"
next
edit "Trusted_MAC_Allow"
set description ''
set fortilink "fortilink"
config policy
edit "Test_MAC1"
set description ''
set status enable
set category device
set match-type dynamic
set mac "F0:CC:FD:A6:A4:1B"
set hw-vendor ''
set type ''
set family ''
set host ''
set lldp-profile ''
set qos-policy ''
set 802-1x ''
set vlan-policy "SW_VLAN"
set bounce-port-link enable
next
edit "Test_MAC2"
set description ''
set status enable
set category device
set match-type dynamic
set mac "E0:17:F4:EE:36:17"
set hw-vendor ''
set type ''
set family ''
set host ''
set lldp-profile ''
set qos-policy ''
set 802-1x ''
set vlan-policy "SW_VLAN"
set bounce-port-link enable
next
edit "Test_MAC3"
set description ''
set status enable
set category device
set match-type dynamic
set mac "02:DE:AD:BE:EF:01"
set hw-vendor ''
set type ''
set family ''
set host ''
set lldp-profile ''
set qos-policy ''
set 802-1x ''
set vlan-policy "SW_VLAN"
set bounce-port-link enable
next
end
next
end
Fortilink configuration
config switch-controller fortilinksettings
edit "fortilink"
set fortilink "fortilink"
set inactive-timer 15
set link-down-flush enable
set access-vlan-mode legacy
config nac-ports
set onboarding-vlan "onboarding"
set lan-segment enabled
set nac-lan-interface "nac_segment"
set nac-segment-vlans "voice" "video"
end
next
end

