Solved
Fortinet recommended malicious IPs or URLs, or Malware Hash source
Hello Team,
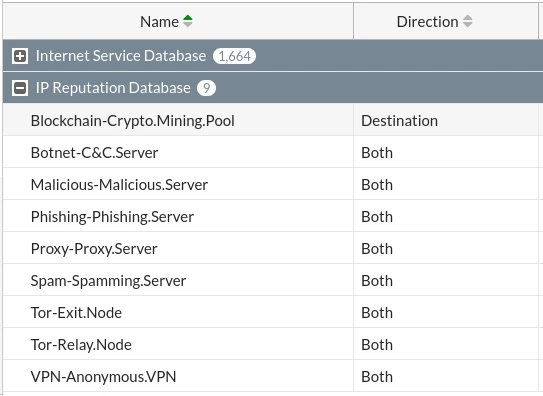
I am paloalto more guy and I used to utilize Paloalto's EDLs, so I wanted to ask about any Dynamic group that contains Malicious IP addresses, URLs, or domain lists that are included in the FortiOS and I can use them in my policies.
If not, what are recommeded other sources "feeds" to add as External groups as feed that I can use for more protection in my policies?
or also any Malware Hash feeds that are valuable.
TIA