rg_586
New Member
December 11, 2022
Solved

Fortinet 201E - v7.2.2 - Configure Dedicated Management Port - Active/ Passive - Problem

  • December 11, 2022
  • 4 replies
  • 6954 views

Hi I have a problem with dedicated management port setup with my Fortinet 201E running version 7.2.2

Please can someone take a look at my problem when I am trying to setup a dedicated management port. I have an Active/ Passive setup and I would like to configure a different IP Address on each box. I would like to see on the Monitoring tool that both devices are up and not just the cluster, and also to be able to login to both Active/ Passive device.

I was configuring the dedicated management port and I keep getting the error in the screen shots that I have provided.

https://community.fortinet.com/t5/FortiGate/Technical-Note-How-to-dedicate-an-interface-to-management/ta-p/189625

The setup is as follows;

Root - is not the management VDOM, the was changed to have FIREWALL-1 context as the management VDOM.

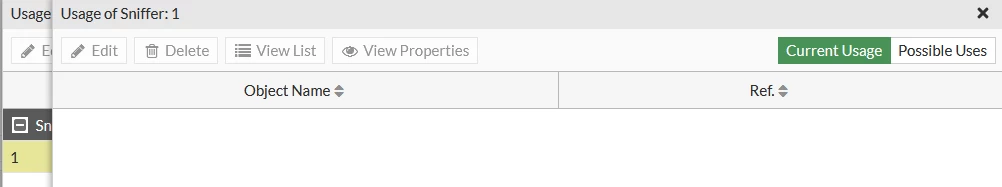
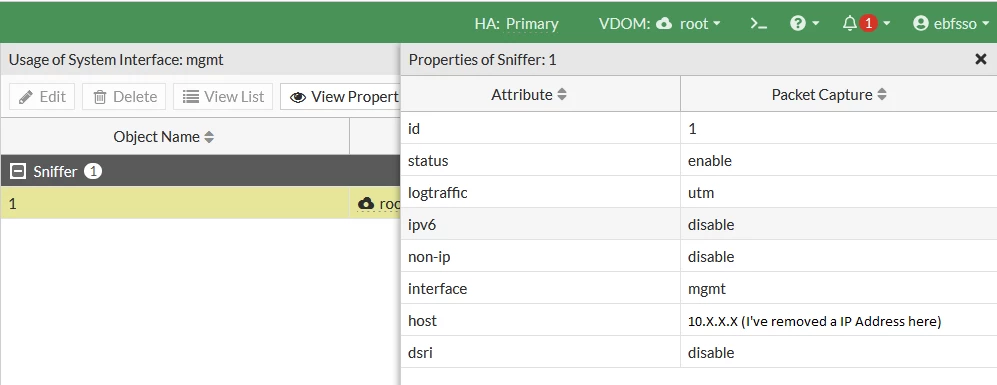
Everything is working well with the setup, except I have a reference attached to the management port, a “Sniffer” object type, I have provided screen shots,


When I follow the link that I just posted for configuring a dedicated management port, I run into an error, and I believe this could be because I have a reference attached to the mgmt port.

If I could get help with;

- Any direction on how to setup dedicated management port on each device
- How to remove the reference on the mgmt port or even reset the port
- I have attached my the port configuration in the image, and I have added the “sniffer” reference images
- I have attached the image when I am trying to configure a dedicated management port, not sure how to get around that error if it is not related to port reference

Note: I have checked the Sniffer section and this has never been used
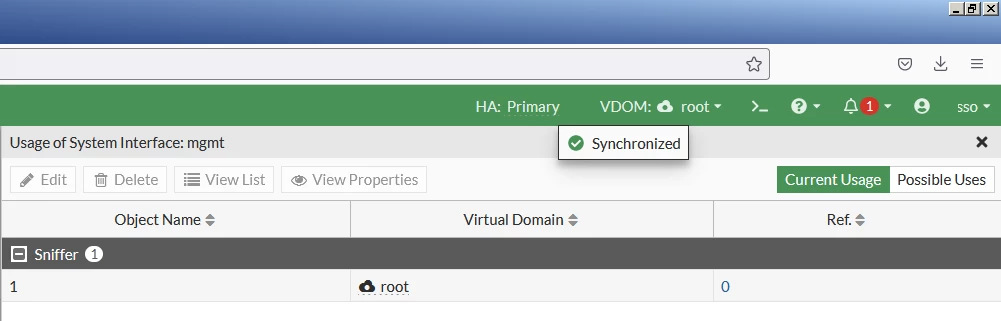
 

Fortinet_mgmt_1.PNGFortinet_mgmt_2.PNGFortinet_mgmt_3.PNG

Best answer by gfleming

Interface references are external to the interface's configuration. In this case you have a sniffer configuration as a reference to the MGMT interface. So we need to go to the sniffer config to remove it.


show firewall sniffer


You should see an ID # there that is referencing your MGMT port. Just delete it and you should be good.


config firewall sniffer
  delete <#>
end


4 replies

gfleming
Staff
Staff
December 12, 2022

HEre are details for setting up dedicated management interfaces for each node:

https://docs.fortinet.com/document/fortigate/7.2.3/administration-guide/313152/out-of-band-management-with-reserved-management-interfaces


To remove the reference just highlight the listed reference (in this case the sniffer item) and click the "Delete" button.

rg_586
rg_586Author
New Member
December 12, 2022

@gfleming 

The delete button is greyed out, that was my first option through the screen shots that I posted, I followed through the reference and ended up with Properties of Sniffer and all greyed out options.


I would like to delete this reference or reset the port, I did remove all properties linked to this port as you can see in my txt file, but I am lost with the error.

FIREWALL-1 # config global  FIREWALL-1 (global) # config system interface   FIREWALL-1 (interface) # edit mgmt  FIREWALL-1 (mgmt) # show config system interface     edit "mgmt"         set vdom "root"         set ip 192.168.1.99 255.255.255.255         set allowaccess ping snmp         set type physical         set dedicated-to management         set lldp-reception disable         set lldp-transmission disable         set role lan         set snmp-index 1         set trust-ip-1 192.168.1.0 255.255.255.0     next end  FIREWALL-1 (mgmt) # show full-configuration  config system interface     edit "mgmt"         set vdom "root"         set vrf 0         set distance 5         set priority 1         set dhcp-relay-interface-select-method auto         set dhcp-relay-service disable         set dhcp-classless-route-addition disable         set management-ip 0.0.0.0 0.0.0.0         set ip 192.168.1.99 255.255.255.255         set allowaccess ping snmp         set fail-detect disable         set arpforward enable         set broadcast-forward disable         set bfd global         set l2forward disable         set icmp-send-redirect enable         set icmp-accept-redirect enable         set reachable-time 30000         set vlanforward disable         set stpforward disable         set ips-sniffer-mode disable         set ident-accept disable         set ipmac disable         set subst disable         set substitute-dst-mac 00:00:00:00:00:00         set status up         set netbios-forward disable         set wins-ip 0.0.0.0         set type physical         set dedicated-to management         set netflow-sampler disable         set sflow-sampler disable         set src-check enable         set sample-rate 2000         set polling-interval 20         set sample-direction both         set explicit-web-proxy disable         set explicit-ftp-proxy disable         set proxy-captive-portal disable         set tcp-mss 0         set inbandwidth 0         set outbandwidth 0         set egress-shaping-profile ''         set ingress-shaping-profile ''         set disconnect-threshold 0         set spillover-threshold 0         set ingress-spillover-threshold 0         set weight 0         set external disable         set description ''         set alias ''         set ike-saml-server ''         set device-identification disable         set lldp-reception disable         set lldp-transmission disable         set estimated-upstream-bandwidth 0         set estimated-downstream-bandwidth 0         set measured-upstream-bandwidth 0         set measured-downstream-bandwidth 0         set bandwidth-measure-time 0         set monitor-bandwidth disable         set vrrp-virtual-mac disable         set role lan         set snmp-index 1         set secondary-IP disable         set preserve-session-route disable         set auto-auth-extension-device disable         set ap-discover enable         set switch-controller-igmp-snooping-proxy disable         set switch-controller-igmp-snooping-fast-leave disable         set eap-supplicant disable         config ipv6             set ip6-mode static             set nd-mode basic             set ip6-address ::/0             unset ip6-allowaccess             set icmp6-send-redirect enable             set ra-send-mtu enable             set ip6-reachable-time 0             set ip6-retrans-time 0             set ip6-hop-limit 0             set vrrp-virtual-mac6 disable             set vrip6_link_local ::             set ip6-send-adv disable             set autoconf disable         end         set dhcp-relay-request-all-server disable         set defaultgw enable         set dns-server-override enable         set dns-server-protocol cleartext         set speed auto         set trust-ip-1 192.168.1.0 255.255.255.0         set trust-ip-2 0.0.0.0 0.0.0.0         set trust-ip-3 0.0.0.0 0.0.0.0         set trust-ip6-1 ::/0         set trust-ip6-2 ::/0         set trust-ip6-3 ::/0         set mtu-override disable         set wccp disable         set drop-overlapped-fragment disable         set drop-fragment disable     next end  FIREWALL-1 (mgmt) # end  FIREWALL-1 (global) # config system dedicated-mgmt   FIREWALL-1 (dedicated-mgmt) # set status enable   FIREWALL-1 (dedicated-mgmt) # set interface mgmt entry not found in datasource  value parse error before 'mgmt' Command fail. Return code -3  FIREWALL-1 (dedicated-mgmt) # set interface "mgmt" entry not found in datasource  value parse error before 'mgmt' Command fail. Return code -3  FIREWALL-1 (dedicated-mgmt) # 


gfleming
Staff
gflemingAnswer
Staff
December 13, 2022

Interface references are external to the interface's configuration. In this case you have a sniffer configuration as a reference to the MGMT interface. So we need to go to the sniffer config to remove it.


show firewall sniffer


You should see an ID # there that is referencing your MGMT port. Just delete it and you should be good.


config firewall sniffer
  delete <#>
end


Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!