

miciti
Visitor III
August 26, 2024
Solved

Fortigate: Virtual IPs with FQDN (internal / external DNS server)

  • August 26, 2024
  • 5 replies
  • 3748 views

Hello everyone,


Our Firewall was configured with several virtual IPs (static NATs) to forward internet traffic do our internal services.

Currently we do have three public IP adresses but I want to merge them.


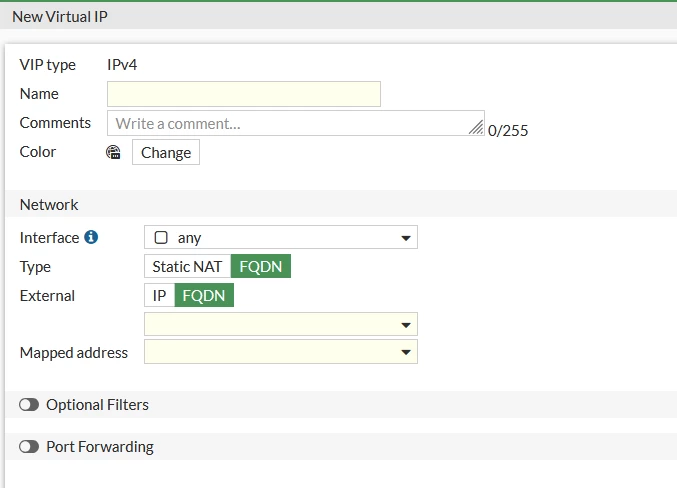
So I do want to use virtual IPs with FQDN.

I guess I need to enter the External FQDN in the top field, and the internal fqdn in the bottom field (mapped address).


We use windows DNS server for internal name resolution (so that our clients can find each other). When we do intern name resolution the public domain name gets overwritten with the internal IP address... (e.g. service.company.at gets an private IP adress in our company lan and no the public one) so traffic does not have to use the internet.


So I guess I somehow need to add two different DNS to FortiGate - one for public dns name and one for the private IP adress (=mapped address). Does that even work when both names are identically?

 

NSTUJAgIzO.png

Best answer by Nchandan

Hi Miciti,


You can check  This approach  a split DNS setup, where the same FQDN resolves to different IP addresses depending on whether the request originates from inside or outside the network.

https://community.fortinet.com/t5/FortiGate/Technical-Tip-Implement-split-DNS-for-Local-and-Global-domain/ta-p/225443

DNS Forwarding: You could configure FortiGate to forward DNS queries to the appropriate DNS server based on the source of the query. For instance, internal DNS queries go to the internal DNS server, and external ones are handled differently

https://community.fortinet.com/t5/FortiGate/Technical-Tip-DNS-conditional-forwarding/ta-p/196821


Regards 

Chandan

5 replies

Mrinmoy
Staff
Staff
August 26, 2024

As you are using an internal DNS server, the DNS server should resolve it as per its config, not the FortiGate.

rahul_p1
Staff
Staff
August 27, 2024

Hi Miciti,


Yes, it does work with identical names, as long as:

  • Internal clients use the internal DNS server that resolves the FQDN to the internal IP.
  • External clients use a public DNS that resolves the FQDN to the public IP.

The key is to ensure that internal and external clients are using the correct DNS servers, which provide different responses based on where the query originates.


Regards 

Rahul

miciti
micitiAuthor
Visitor III
August 29, 2024

Hm I did a testing and it didn't seem to work.

I strongly think because our FortiGate is set up to resolve everything via the internal DNS...

Nchandan
Staff
NchandanAnswer
Staff
August 27, 2024

Hi Miciti,


You can check  This approach  a split DNS setup, where the same FQDN resolves to different IP addresses depending on whether the request originates from inside or outside the network.

https://community.fortinet.com/t5/FortiGate/Technical-Tip-Implement-split-DNS-for-Local-and-Global-domain/ta-p/225443

DNS Forwarding: You could configure FortiGate to forward DNS queries to the appropriate DNS server based on the source of the query. For instance, internal DNS queries go to the internal DNS server, and external ones are handled differently

https://community.fortinet.com/t5/FortiGate/Technical-Tip-DNS-conditional-forwarding/ta-p/196821


Regards 

Chandan

miciti
micitiAuthor
Visitor III
August 29, 2024

Thank you very much! I will give this a try

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!
