

Jin-Gyu
Explorer
July 28, 2025
Solved

Fortigate TP Mode Broadcast Drop

  • July 28, 2025
  • 6 replies
  • 957 views

Hi

I use Fortigate 101F with v7.0.12 in TP mode, but broadcast drops occur.

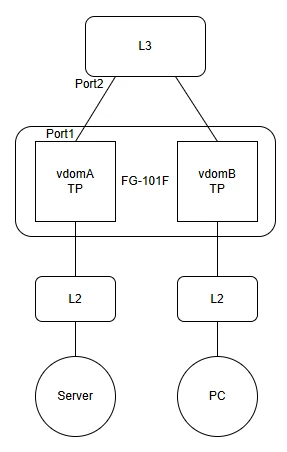
The configuration diagram is as follows.
스크린샷 2025-07-28 142106.png

Normally, there is no problem and when I reboot the server, the communication between the PC and the server side L2 does not work.

As a result of checking, the MAC address of L3 was not learned in vdomA.

So I put the mac-address of L3 port2 into the mac-address-table of vdomA statically and it works normally.


This doesn't happen very often, it happens very occasionally.

I enabled broadcast-forward, why does this happen?



Best answer by AEK

Normally ARP broadcast is the only one allowed by default.

But can you try this one (for troubleshooting) just to see if it helps? The tech tip is for DHCP but you need you adapt it for ARP.

https://community.fortinet.com/t5/FortiGate/Technical-Note-How-to-allow-the-flow-of-transit-DHCP-traffic-in/ta-p/191769

Hope it helps.

6 replies

AEK
SuperUser
SuperUser
July 28, 2025

Hi Jin

Normally when you try ping from PC to Server for the first time, L3 sends ARP query like "who has x.x.x.x", and here VDOM A should learn it.

When you try "diag sniffer packet port1" do you see those ARP broadcasts from L3?

AEK
Jin-Gyu
Jin-GyuAuthor
Explorer
July 28, 2025

packet flow request is pc > l2 > vdomB > l3 > vdomA > l2 > server

response is server > l2 > vdomA broadcast drop

AEK
SuperUser
SuperUser
July 28, 2025

ARP (in transparent mode): by default, ARP broadcasts and ARP reply packets are flooded/forwarded on all ports or VLANs belonging to the same forwarding domain, without the need of firewall policies between the ports. This default behavior is necessary to allow the population of the FDB and allow further firewall policy lookup (see section Transparent mode Firewall processing for more details). This option is configurable at the interface settings level with the parameter arpforward (enabled by default).


Ref: https://fortinetweb.s3.amazonaws.com/docs.fortinet.com/v2/attachments/5aa37c8a-1a11-11e9-9685-f8bc1258b856/fortigate-transparent-mode-56.pdf

(this is for old FortiOS but I couldn't find newer).


On the other hand, when you enable traffic log in the implicit deny rule, do you see the ARP replies are blocked?

AEK
AEK
SuperUser
AEKAnswer
SuperUser
July 28, 2025

Normally ARP broadcast is the only one allowed by default.

But can you try this one (for troubleshooting) just to see if it helps? The tech tip is for DHCP but you need you adapt it for ARP.

https://community.fortinet.com/t5/FortiGate/Technical-Note-How-to-allow-the-flow-of-transit-DHCP-traffic-in/ta-p/191769

Hope it helps.

AEK
Jin-Gyu
Jin-GyuAuthor
Explorer
July 29, 2025

Thank you for your answer. 

I can't try it now because it's not my equipment, but I'll apply it next time the same phenomenon occurs.

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!
