Sat-Cit-Ananda
New Member
August 6, 2026
Solved

FortiGate successfully authenticates against LDAP server, but cannot browse users

  • August 6, 2026
  • 9 replies
  • 126 views

Hello,


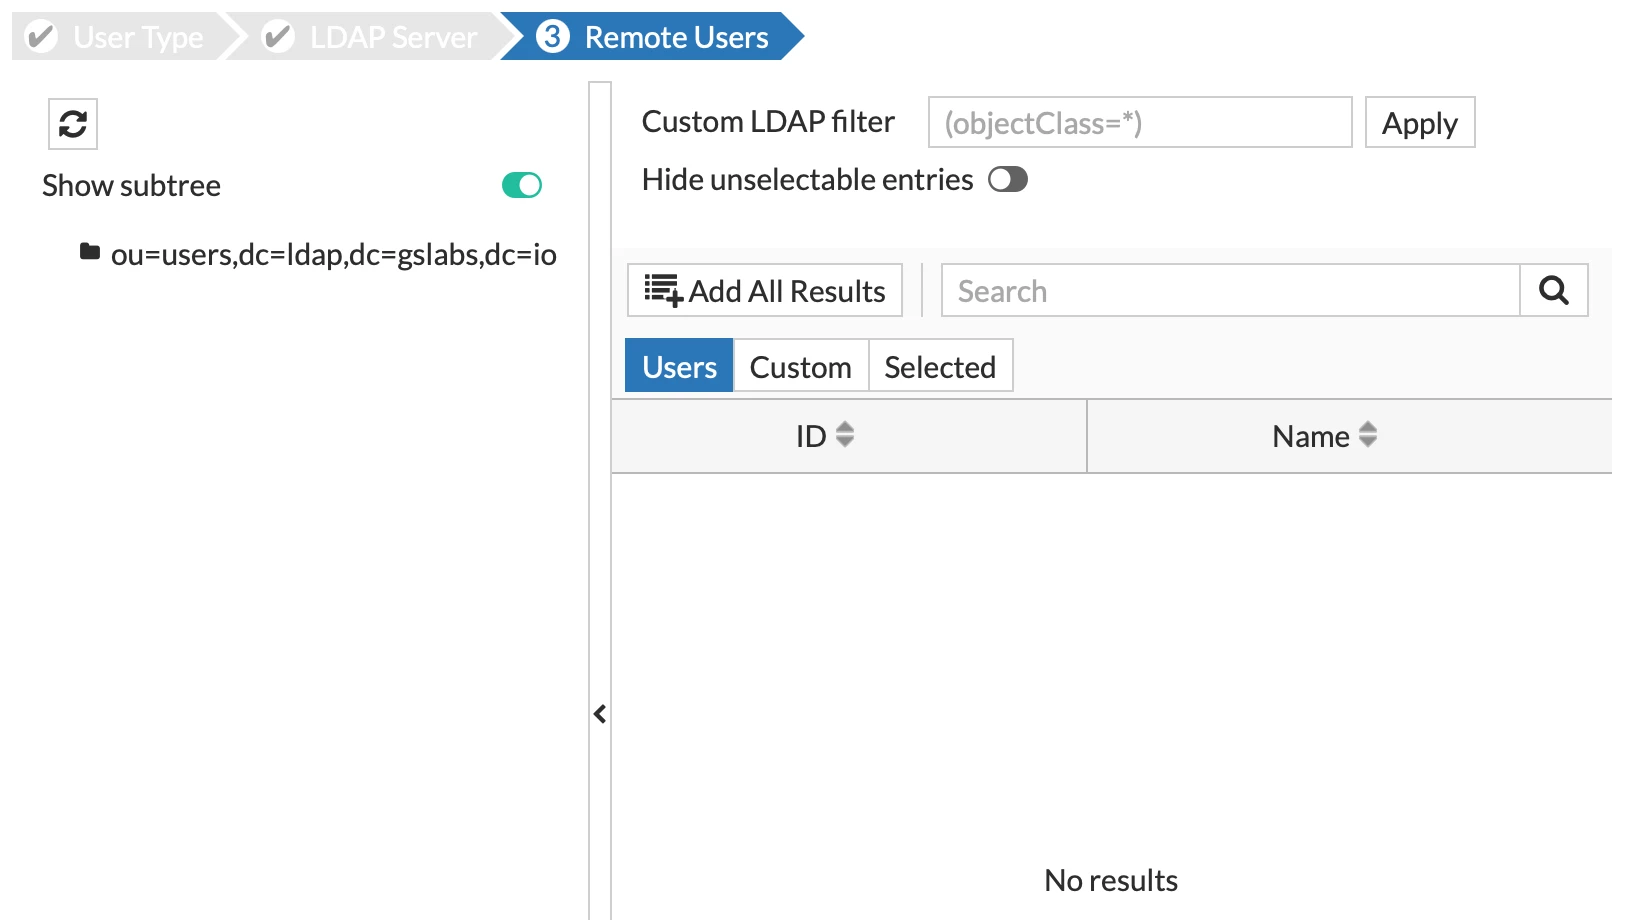
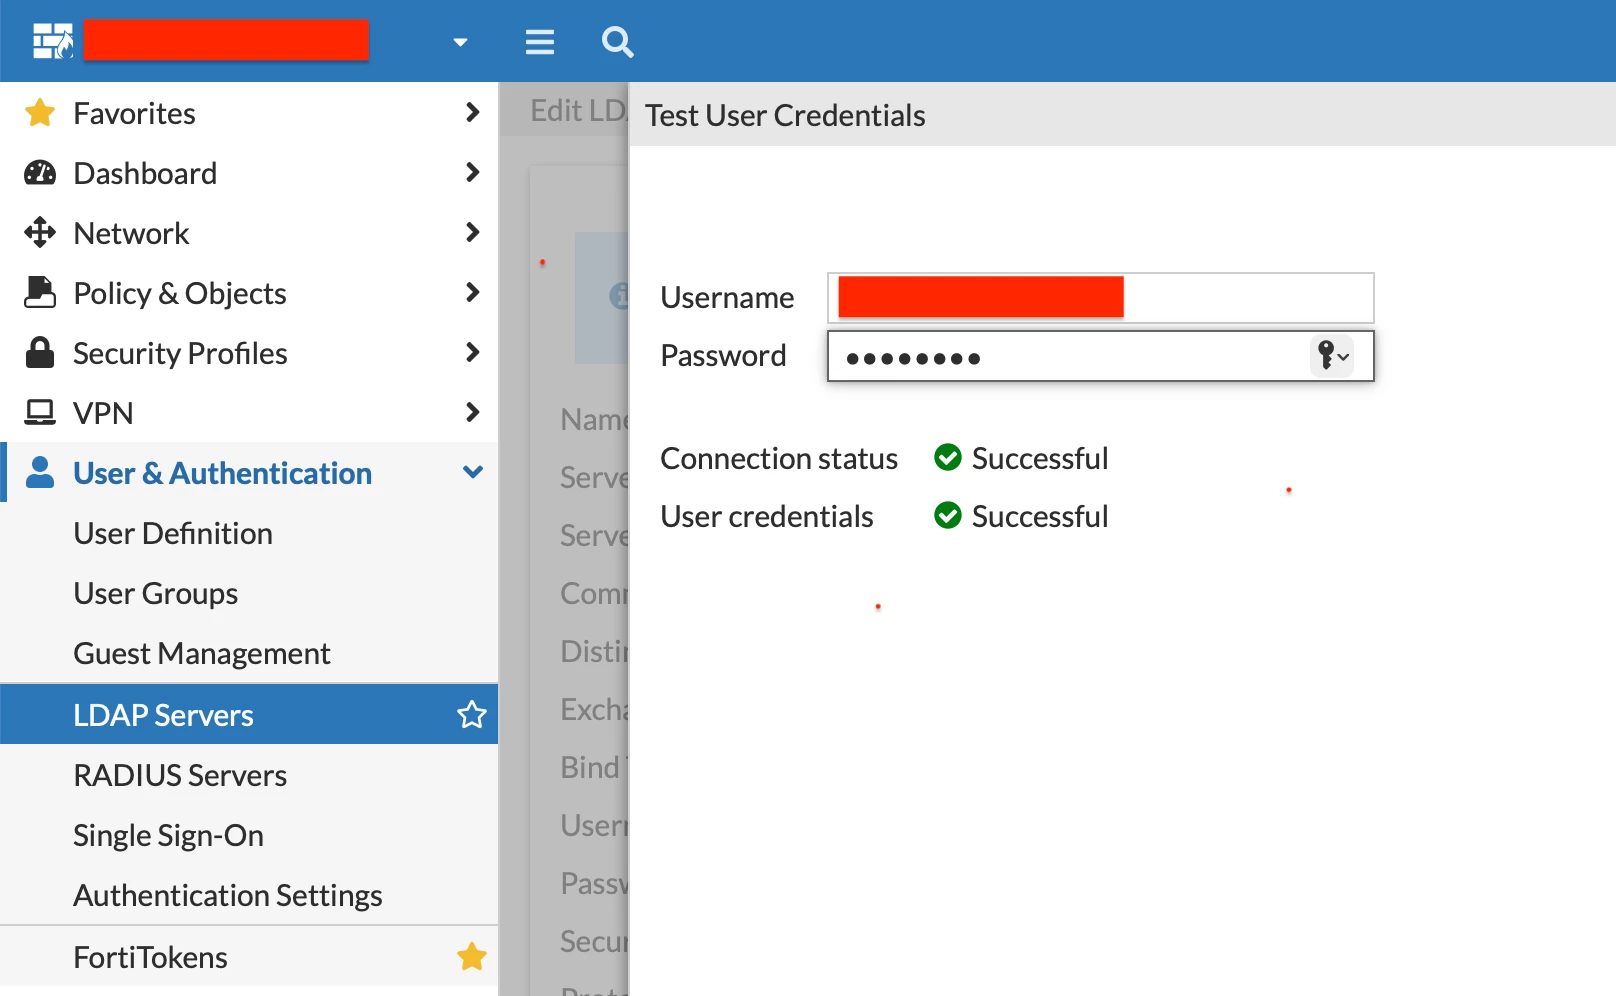
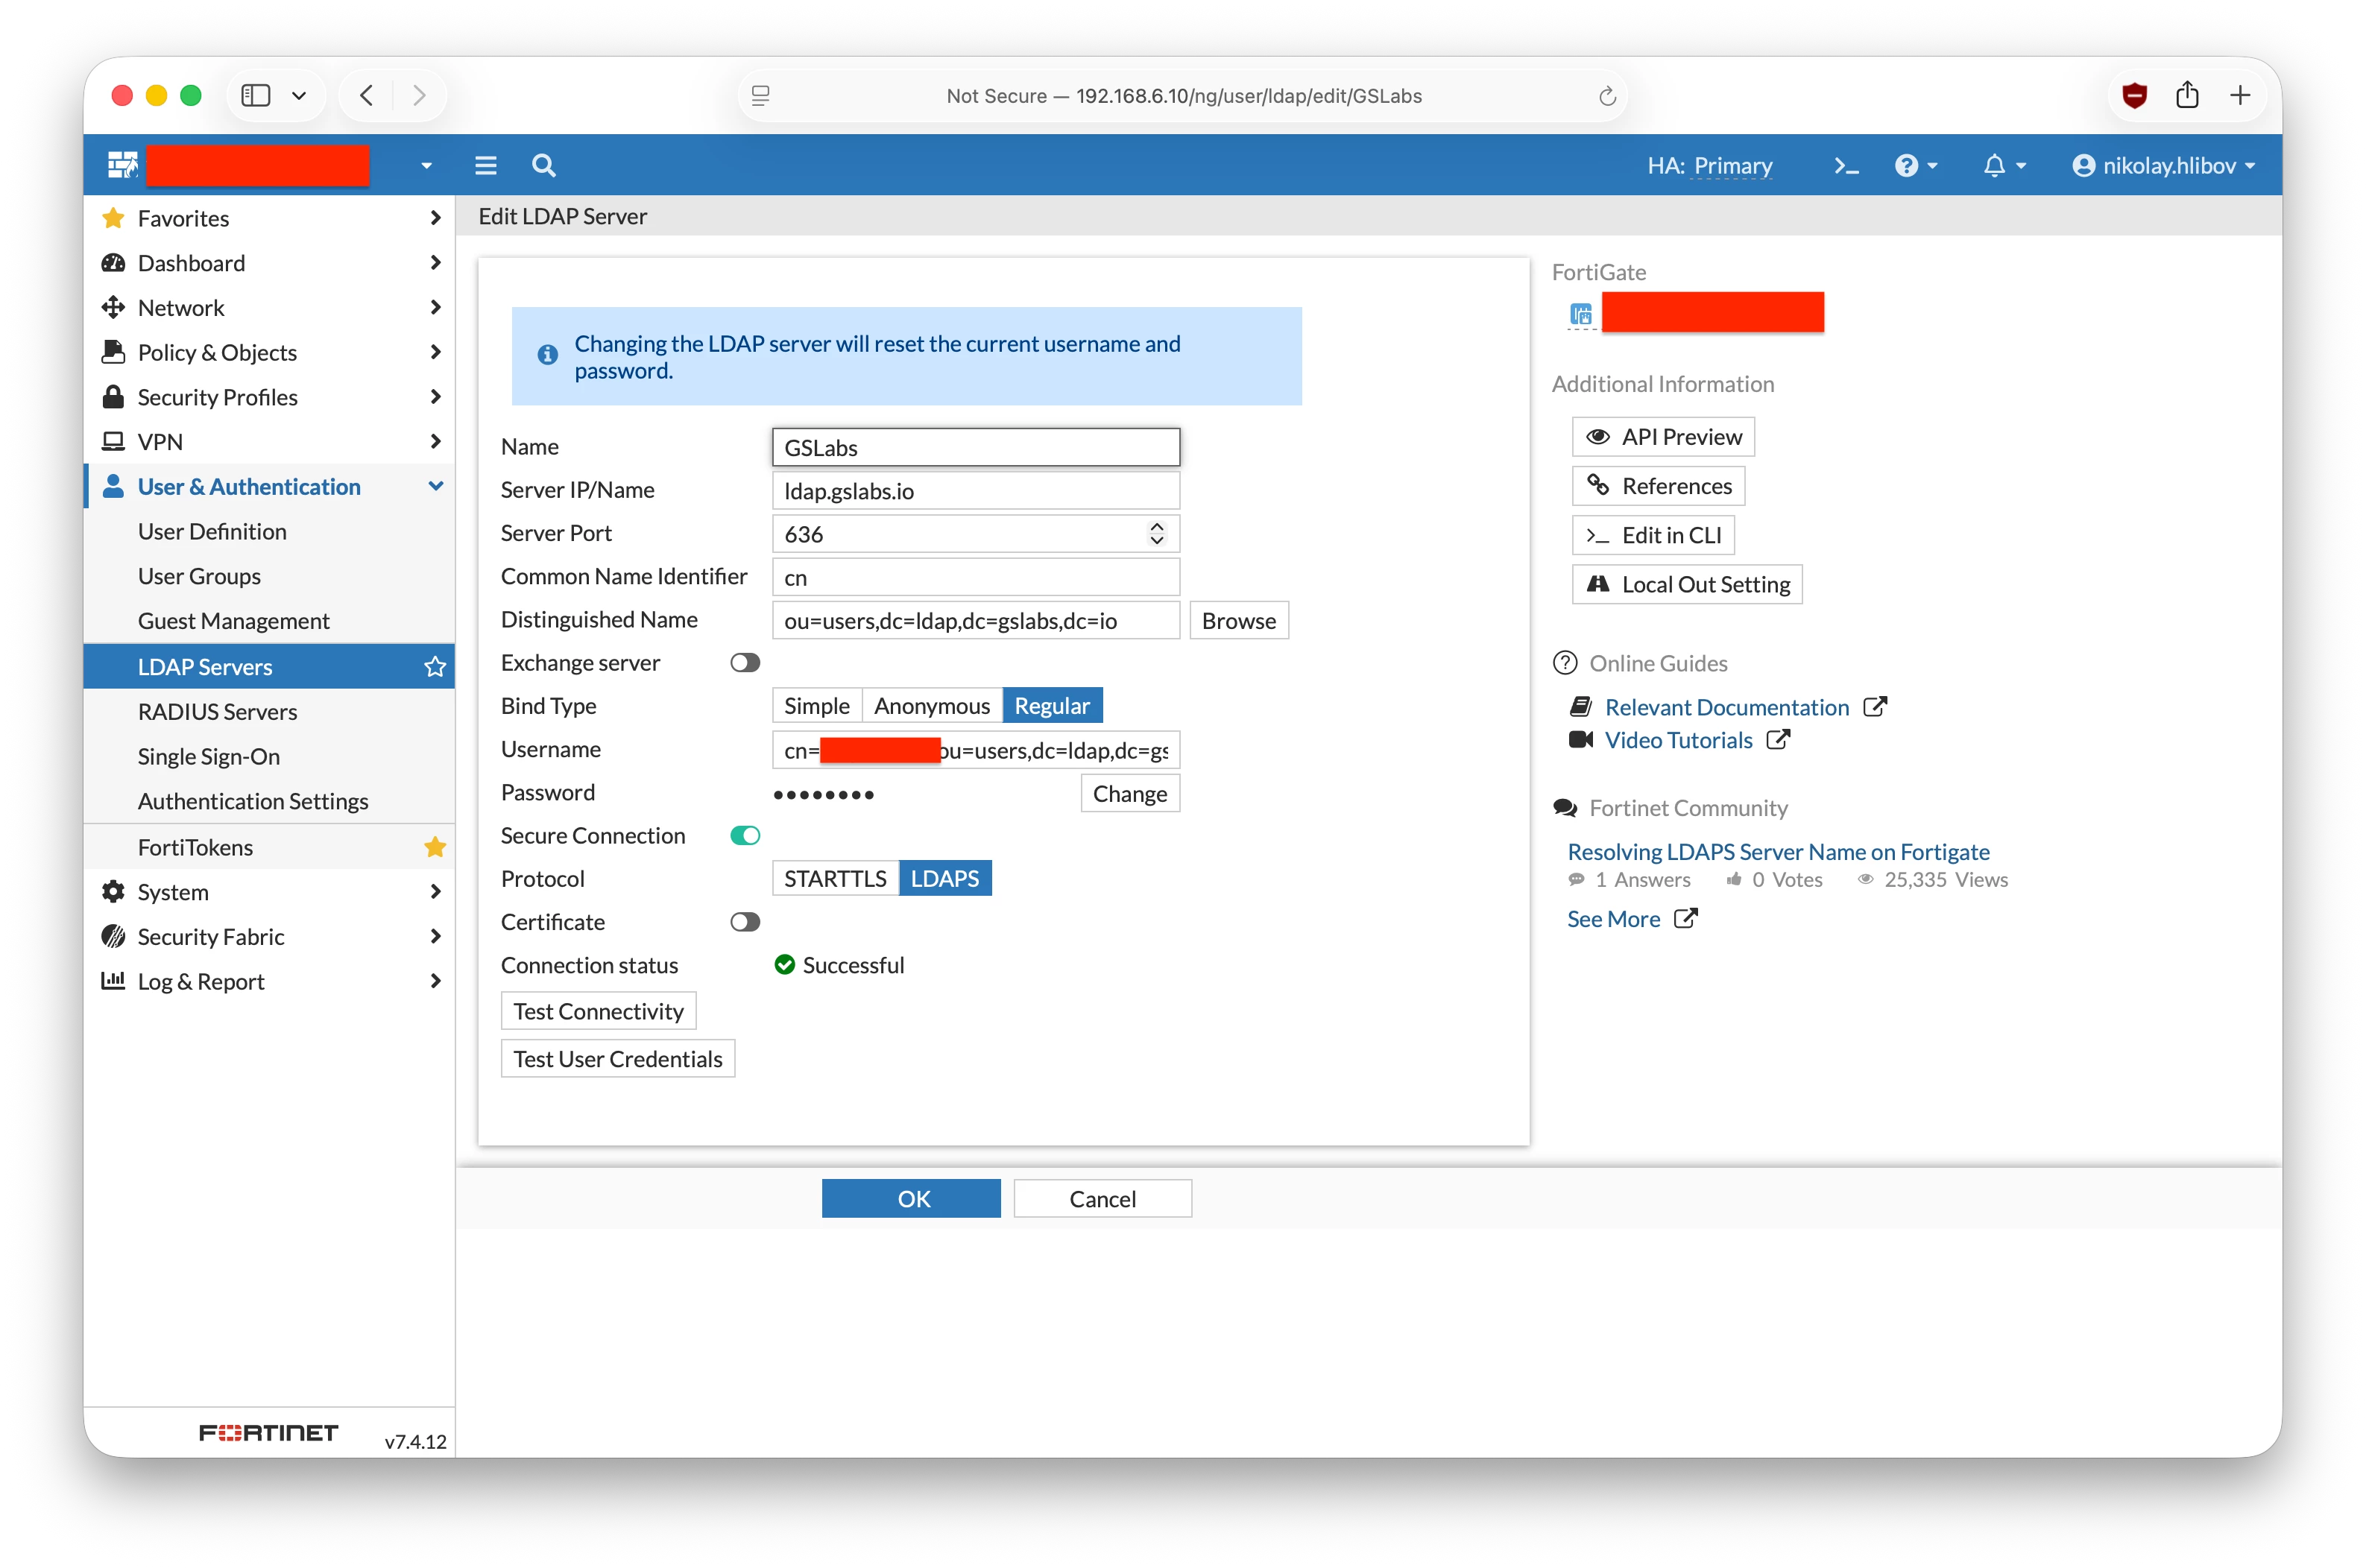
I have a frustrating case where a H-A cluster successfully authenticates against an external LDAP server using port 636, but is not able to browse the users in it.

Testing a user is successful as well. Look at the attached screenshots.

I changed the “cnid” field several times, including “sAMAccountName”.

The version we are using is 7.4.12.
 

Best answer by AEK

I’d first ask LDAP admin which LDAP type is this (Novell, OpenLDAP, AD), and then try find the integration procedure with FGT for this LDAP type. On the other hand I’d try integrate this LDAP with other equipment to see if the issue is related to FGT.

9 replies

Sat-Cit-Ananda
New Member
August 6, 2026

Did anyone had such an issue before? Any help will be appreciated.

AEK
SuperUser
SuperUser
August 6, 2026

Can you try with a domain admin? just to see if it is related to some rights.

AEK
Sat-Cit-Ananda
New Member
August 6, 2026

I’m actually trying with the domain admin account.

AEK
SuperUser
SuperUser
August 6, 2026

Is it active directory or other? And which version?

AEK
Sat-Cit-Ananda
New Member
August 7, 2026

IT is not an Active Directory. It is en external LDAP provider called GSLabs. It’s like Google directory.

I have tried the same connection from some of our servers, and it is working fine. The servers are able to browse the directory with the same account name I’m trying now.

AEK
SuperUser
SuperUser
August 7, 2026

If it is OpenLDAP then try uid as CNID.

AEK
Sat-Cit-Ananda
New Member
August 7, 2026

If I try to use uid, I cannot authenticate users against the LDAP.

AEK
SuperUser
AEKAnswer
SuperUser
August 7, 2026

I’d first ask LDAP admin which LDAP type is this (Novell, OpenLDAP, AD), and then try find the integration procedure with FGT for this LDAP type. On the other hand I’d try integrate this LDAP with other equipment to see if the issue is related to FGT.

AEK
Sat-Cit-Ananda
New Member
August 7, 2026

I think I found the answer. Unfortunately, not completely positive.

The LDAP provider is Authentik (https://goauthentik.io). It turns out they have a long story of LDAP integration problems. Look at this GitHub thread:

https://github.com/goauthentik/authentik/issues/7985

This is exactly the same issue as mine. Authentik does not support Samba scheme in their LDAP, and because of that, full integration with FortiGate (or any other vendor) is impossible. The funny part is that they even reject feature requests to integrate Samba:

https://github.com/goauthentik/authentik/issues/8711


I spoke with my DevOps colleagues and we agreed to integrate a subordinate LDAP service using OpenLDAP. It will sync the directories with Authentik. Then I will integrate the FGT with OpenLDAP. I know it will works, because I did such integrations in the past successfully.

AEK, thank you for the support.

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!