

anru
New Member
May 16, 2025
Question

Fortigate SSLVPN "some users are not using two factor authentication"

  • May 16, 2025
  • 8 replies
  • 1889 views

My FG has SSLVPN service configured that gives remote users access with username/password via LDAP with Mobile FortiToken or OTP via email double authentication activated for all users.

Some users have reported to me that they can access by simply entering only username and password and is not asked to enter the token.

How can this happen if all users have enabled double authentication for access to SSLVPN?


Attached the error shown on FG (firmware version 7.0.17).

User configuration:


# show user local xyz
config user local
edit "xyz"
set type ldap
set two-factor fortitoken
set fortitoken "FTKMOB11016D9D2B"
set email-to "xyz@xyz.com"
set ldap-server "LDAP"
next
end
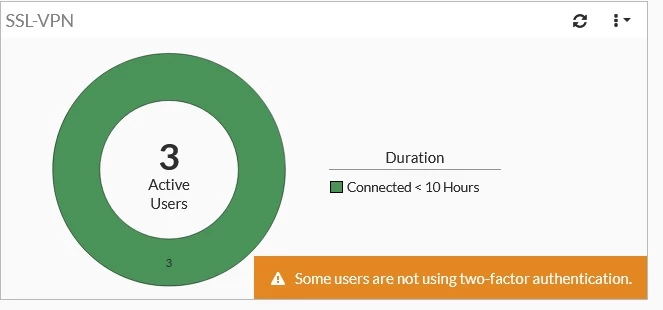

 

FG_warning_message.jpg


8 replies

funkylicious
SuperUser
SuperUser
May 16, 2025

i would start by looking at the users that are logged but w/o MFA.

it should be shown to you which are connected only with user and password and start looking into them.

"jack of all trades, master of none"
anru
anruAuthor
New Member
May 16, 2025

I analyzed the users who reported the problem but their configuration is correct and the same as the others.
Then for 99.9% of users the access to SSLVPN is correct after entering username+password+token, while for a few random users they manage to access without token.

users.jpg


funkylicious
SuperUser
SuperUser
May 16, 2025

i assume that web connections are w/o MFA ?

"jack of all trades, master of none"
Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!
