Fortigate Policy Order – Malicious Traffic Not Matching First Policy
Hello,
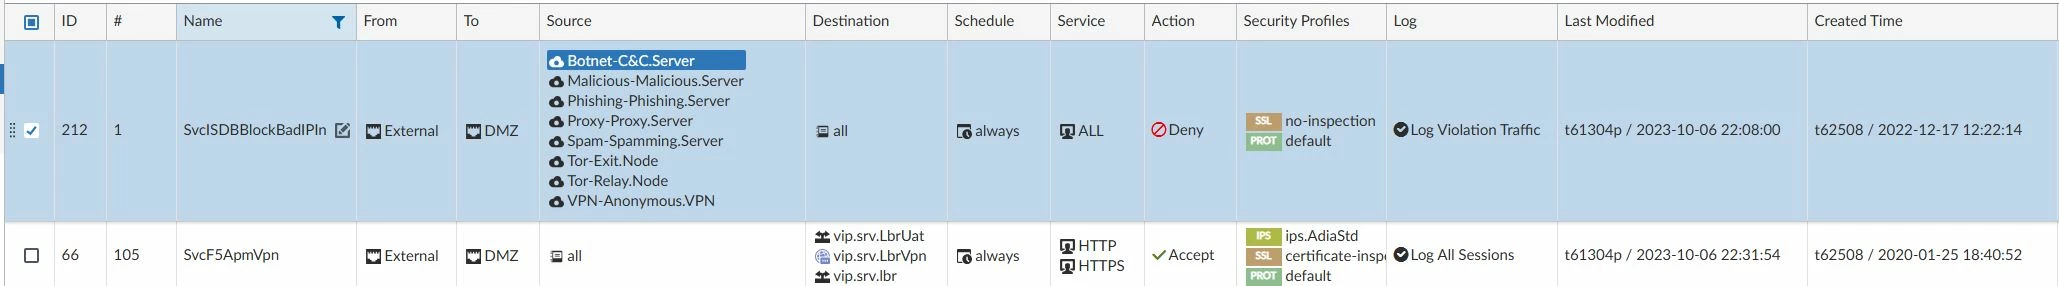
I have configured two firewall policies on Fortigate running on 7.2.10,build1706
- Policy 1: Blocks all malicious traffic using the Fortigate Internet Service Database.
- Policy 2: Allows traffic required to access specific destination public IPs.
The issue I’m facing is that:
- All traffic matching the destination public IP is hitting Policy 2 directly.
- Traffic only hits Policy 1 if there is no NAT IP match.
It seems that the destination public IP traffic bypasses the malicious traffic block in Policy 1 and goes straight to Policy 2.
Questions:
• Is this expected Fortigate behavior due to policy order or NAT configuration?
• How can I ensure that malicious traffic is always blocked by Policy 1 before being allowed by Policy 2?
• Do I need to adjust policy sequence, NAT rules, or apply security profiles differently?
Any guidance or best practices would be appreciated.
Thanks in advance!
Below are the details
vip.srv.LbrUat 198.184.54.58 --> 172.16.28.58
vip.srv.LbrVpn 198.184.54.59 --> 172.16.28.59
vip.srv.lbr 198.184.54.60 --> 172.16.28.60