



Fortigate not routing request from client
Good evening,
Experiencing an issue with FG Routing can anyonn assist,
I have the following setup on a Proxmox node:
1. Ubuntu (Client)
2. Foritgate Firewall
The Client has two interfaces attached with the following networks:
1. 192.168.61.X for management
2. 192.168.10.x (shared network to reach the Fortigate) LAN
The Fortigate has three interfaces attached with the following networks:
1. 192.168.61.X for management
2. 192.168.10.x (shared network to reach the client ) LAN
3. 192.168.100.x (WAN Interface to reach wan router)
I cannot get internet on the client through the FG. I can ping between both the client and the FG on the 192.168.10.0 network but if i try to ping an external network from the client with the FG as the gateway there is no reply.
After running sniffers and debug flow i can see the packet reaching the Fortigate with the following output:
FortiOS-VM64-KVM # diag deb en FortiOS-VM64-KVM # diag sniffer packet any 'host 192.168.10.2' Using Original Sniffing Mode interfaces=[any] filters=[host 192.168.10.2] 0.262386 192.168.10.2 -> 8.8.8.8: icmp: echo request 1.286294 192.168.10.2 -> 8.8.8.8: icmp: echo request 2.310243 192.168.10.2 -> 8.8.8.8: icmp: echo request 3.333913 192.168.10.2 -> 8.8.8.8: icmp: echo request 4.357761 192.168.10.2 -> 8.8.8.8: icmp: echo request 5.382364 192.168.10.2 -> 8.8.8.8: icmp: echo request 6.406127 192.168.10.2 -> 8.8.8.8: icmp: echo request 7.430170 192.168.10.2 -> 8.8.8.8: icmp: echo request 8.453941 192.168.10.2 -> 8.8.8.8: icmp: echo request 9.478245 192.168.10.2 -> 8.8.8.8: icmp: echo request 10.502422 192.168.10.2 -> 8.8.8.8: icmp: echo request 11.526356 192.168.10.2 -> 8.8.8.8: icmp: echo request 12.549849 192.168.10.2 -> 8.8.8.8: icmp: echo request 13.574263 192.168.10.2 -> 8.8.8.8: icmp: echo request 14.598060 192.168.10.2 -> 8.8.8.8: icmp: echo request ^C 18 packets received by filter 0 packets dropped by kernel FortiOS-VM64-KVM # diag deb en FortiOS-VM64-KVM # diag deb flow filter saddr 192.168.10.2 FortiOS-VM64-KVM # diag debug flow trace start 100 FortiOS-VM64-KVM # id=20085 trace_id=1 func=print_pkt_detail line=5742 msg="vd-root:0 received a packet(proto=1, 192.168.10.2:7->8.8.8.8:2048) from port2. type=8, code=0, id=7, seq=89." id=20085 trace_id=1 func=init_ip_session_common line=5913 msg="allocate a new session-0000047c" id=20085 trace_id=1 func=vf_ip_route_input_common line=2621 msg="find a route: flag=04000000 gw-192.168.100.1 via port1" id=20085 trace_id=2 func=print_pkt_detail line=5742 msg="vd-root:0 received a packet(proto=1, 192.168.10.2:7->8.8.8.8:2048) from port2. type=8, code=0, id=7, seq=90." id=20085 trace_id=2 func=init_ip_session_common line=5913 msg="allocate a new session-0000047d" id=20085 trace_id=2 func=vf_ip_route_input_common line=2621 msg="find a route: flag=04000000 gw-192.168.100.1 via port1" id=20085 trace_id=3 func=print_pkt_detail line=5742 msg="vd-root:0 received a packet(proto=1, 192.168.10.2:7->8.8.8.8:2048) from port2. type=8, code=0, id=7, seq=91." id=20085 trace_id=3 func=init_ip_session_common line=5913 msg="allocate a new session-0000047e" id=20085 trace_id=3 func=vf_ip_route_input_common line=2621 msg="find a route: flag=04000000 gw-192.168.100.1 via port1" id=20085 trace_id=4 func=print_pkt_detail line=5742 msg="vd-root:0 received a packet(proto=1, 192.168.10.2:7->8.8.8.8:2048) from port2. type=8, code=0, id=7, seq=92." id=20085 trace_id=4 func=init_ip_session_common line=5913 msg="allocate a new session-0000047f" id=20085 trace_id=4 func=vf_ip_route_input_common line=2621 msg="find a route: flag=04000000 gw-192.168.100.1 via port1" id=20085 trace_id=5 func=print_pkt_detail line=5742 msg="vd-root:0 received a packet(proto=1, 192.168.10.2:7->8.8.8.8:2048) from port2. type=8, code=0, id=7, seq=93." id=20085 trace_id=5 func=init_ip_session_common line=5913 msg="allocate a new session-00000480" id=20085 trace_id=5 func=vf_ip_route_input_common line=2621 msg="find a route: flag=04000000 gw-192.168.100.1 via port1" id=20085 trace_id=6 func=print_pkt_detail line=5742 msg="vd-root:0 received a packet(proto=1, 192.168.10.2:7->8.8.8.8:2048) from port2. type=8, code=0, id=7, seq=94." id=20085 trace_id=6 func=init_ip_session_common line=5913 msg="allocate a new session-00000481" id=20085 trace_id=6 func=vf_ip_route_input_common line=2621 msg="find a route: flag=04000000 gw-192.168.100.1 via port1" id=20085 trace_id=7 func=print_pkt_detail line=5742 msg="vd-root:0 received a packet(proto=1, 192.168.10.2:7->8.8.8.8:2048) from port2. type=8, code=0, id=7, seq=95." id=20085 trace_id=7 func=init_ip_session_common line=5913 msg="allocate a new session-00000482" id=20085 trace_id=7 func=vf_ip_route_input_common line=2621 msg="find a route: flag=04000000 gw-192.168.100.1 via port1" id=20085 trace_id=8 func=print_pkt_detail line=5742 msg="vd-root:0 received a packet(proto=1, 192.168.10.2:7->8.8.8.8:2048) from port2. type=8, code=0, id=7, seq=96." id=20085 trace_id=8 func=init_ip_session_common line=5913 msg="allocate a new session-00000483" id=20085 trace_id=8 func=vf_ip_route_input_common line=2621 msg="find a route: flag=04000000 gw-192.168.100.1 via port1" id=20085 trace_id=9 func=print_pkt_detail line=5742 msg="vd-root:0 received a packet(proto=1, 192.168.10.2:7->8.8.8.8:2048) from port2. type=8, code=0, id=7, seq=97." id=20085 trace_id=9 func=init_ip_session_common line=5913 msg="allocate a new session-00000484" id=20085 trace_id=9 func=vf_ip_route_input_common line=2621 msg="find a route: flag=04000000 gw-192.168.100.1 via port1" id=20085 trace_id=10 func=print_pkt_detail line=5742 msg="vd-root:0 received a packet(proto=1, 192.168.10.2:7->8.8.8.8:2048) from port2. type=8, code=0, id=7, seq=98." id=20085 trace_id=10 func=init_ip_session_common line=5913 msg="allocate a new session-00000485" id=20085 trace_id=10 func=vf_ip_route_input_common line=2621 msg="find a route: flag=04000000 gw-192.168.100.1 via port1"
there is a statiic route on the Fortigate using the WAN interface and from the FG i can ping anything on the internet so there is internet access on the firewall:
FortiOS-VM64-KVM # exe ping 8.8.8.8 PING 8.8.8.8 (8.8.8.8): 56 data bytes 64 bytes from 8.8.8.8: icmp_seq=0 ttl=114 time=46.1 ms 64 bytes from 8.8.8.8: icmp_seq=1 ttl=114 time=46.3 ms ^C --- 8.8.8.8 ping statistics --- 2 packets transmitted, 2 packets received, 0% packet loss round-trip min/avg/max = 46.1/46.2/46.3 ms FortiOS-VM64-KVM # exe ping www.google.com PING www.google.com (142.251.35.228): 56 data bytes 64 bytes from 142.251.35.228: icmp_seq=0 ttl=113 time=46.6 ms 64 bytes from 142.251.35.228: icmp_seq=1 ttl=113 time=46.6 ms 64 bytes from 142.251.35.228: icmp_seq=2 ttl=113 time=46.4 ms ^C --- www.google.com ping statistics --- 3 packets transmitted, 3 packets received, 0% packet loss round-trip min/avg/max = 46.4/46.5/46.6 ms FortiOS-VM64-KVM # get router info routing-table connected Routing table for VRF=0 C 192.168.10.0/24 is directly connected, port2 C 192.168.61.0/24 is directly connected, mgmt C 192.168.100.0/24 is directly connected, port1 FortiOS-VM64-KVM # get router info routing-table all Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP O - OSPF, IA - OSPF inter area N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2 E1 - OSPF external type 1, E2 - OSPF external type 2 i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2, ia - IS-IS inter area * - candidate default Routing table for VRF=0 S* 0.0.0.0/0 [5/0] via 192.168.100.1, port1 C 192.168.10.0/24 is directly connected, port2 C 192.168.61.0/24 is directly connected, mgmt C 192.168.100.0/24 is directly connected, port1 FortiOS-VM64-KVM # get router info routing-table details show routing table details information all show all routing table entries rip show rip routing table ospf show ospf routing table bgp show bgp routing table isis show isis routing table static show static routing table connected show connected routing table database show routing information base FortiOS-VM64-KVM # get router info routing-table database Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP O - OSPF, IA - OSPF inter area N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2 E1 - OSPF external type 1, E2 - OSPF external type 2 i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2, ia - IS-IS inter area > - selected route, * - FIB route, p - stale info Routing table for VRF=0 S *> 0.0.0.0/0 [5/0] via 192.168.100.1, port1 S 192.168.10.0/24 [10/0] via 192.168.10.1, port2 C *> 192.168.10.0/24 is directly connected, port2 C *> 192.168.61.0/24 is directly connected, mgmt C *> 192.168.100.0/24 is directly connected, port1
Based on the debugs it seems fortigate cannot find a route once the intial packet comes from the LAN network but has no trouble if the traffic initiates from itself.
can anyone assist in troubleshooting issue.
Here is how the interfaces are setup on the host (Proxmox).
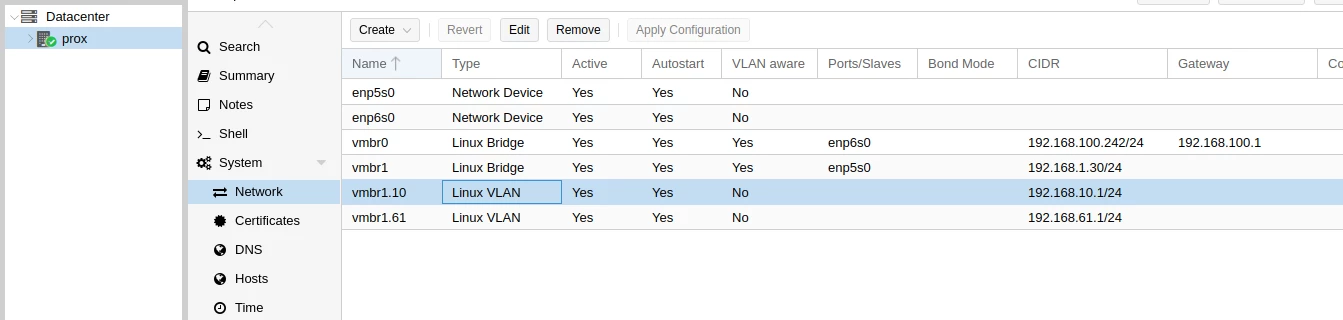
thanks for your assistance.
regards,
#fortigate, #proxmox


