
Frederic-Chaussee
New Member
Jan 10, 2024 9:35 AM UTC
Solved

Fortigate Multi-VDOM/Hub'n Spoke/SDWAN

Hi everyone,


Here is my use case :


I set up a Hub'n Spoke topology with Hub in azure and physical appliance in offices.

In one of theses office, we share Internet acces with tenants.


So, I activate multi-vdom on this Fortigate but, I'm stuck on how to configure Internet acces, how to set up this FGW as a spoke.


At this time everything is in the root VDOM.

I want to set up a VDOM for my Company and a VDOM for tenants.

Tenants only need to access Internet.

And Of course My company need to access Internal ressource throgh Hub'n Spoke topology.
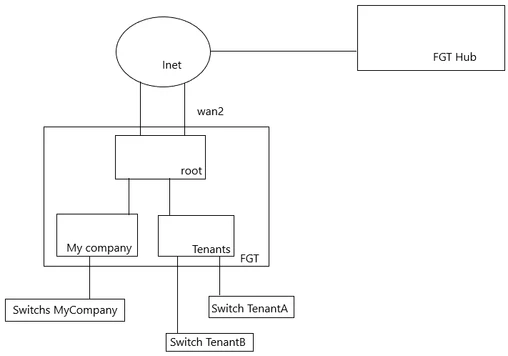


image.png


So my questions are :

- Where should be may hub'n Spoke logic (Tunnels and SDWan rules) in Root or MyCompany VDOM?

- How do I share Internet access (VDOM Link, VLAN on NPU Vdom Link assigned to each VDOM)?

- What are the best practices for this scenario.


PS.: FortiOS is 7.0.13


Thanks for your help,

Frederic.

rarumugam
rarumugamAnswer
Staff
Jan 10, 2024 10:38 AM UTC

Hello Frederic,

I would suggest to use vlans on NPU vlinks to provide internet access for the custom vdoms via the root vdom. The reason is that the regular VDOM links are kernel based links with 1 Gbps line rate and the traffic flowing via these links cannot be offloaded. Regarding the Tunnels and SDWAN configuration, suggest to do it on the Company Vdom and terminate VPN tunnel on the NPU vlink.
We don't require any DNAT to be done on the root(Internet Vdom) for the tunnel establishment as it is a spoke and tunnel is always initiated from the spoke.

I would suggest to upgrade the firmware to FortiOS 7.2.7(expected to be released during the last of Feb, 2024) as it contains couple of improvements for IPSEC tunnels bound on NPU vlinks.


Cheers,

2 replies

rarumugam
Staff
rarumugamAnswer
Staff
Jan 10, 2024 10:38 AM UTC

Hello Frederic,

I would suggest to use vlans on NPU vlinks to provide internet access for the custom vdoms via the root vdom. The reason is that the regular VDOM links are kernel based links with 1 Gbps line rate and the traffic flowing via these links cannot be offloaded. Regarding the Tunnels and SDWAN configuration, suggest to do it on the Company Vdom and terminate VPN tunnel on the NPU vlink.
We don't require any DNAT to be done on the root(Internet Vdom) for the tunnel establishment as it is a spoke and tunnel is always initiated from the spoke.

I would suggest to upgrade the firmware to FortiOS 7.2.7(expected to be released during the last of Feb, 2024) as it contains couple of improvements for IPSEC tunnels bound on NPU vlinks.


Cheers,

Translate
Frederic-Chaussee
New Member
Jan 15, 2024 7:57 AM UTC

Hi Rarumugam,

Thanks a lot for your help. even if I didn't choose this solution, it makes me go on the right way (I think).


In stead of using NPU vLink, I create EMAC VLAN in VDOMs on my Wan Interface and, everything is working as expected.


Best regards,

Frederic

Translate
Risk and Resilience in the Age of AI. An OT Thought Leadership Summit for Houston's Critical Infrastructure Leaders. Date: Thursday, December 3, 2026. Time: 8:30 am - 1:30 pm (CT). Location: The Westin Houston, Memorial City | 945 Gessner Road, Houston, TX 77024
