Question
Fortigate Firewall Policies Best Practices
Hello everybody,
I would like to get some info's how you are dealing with Firewall Policies.
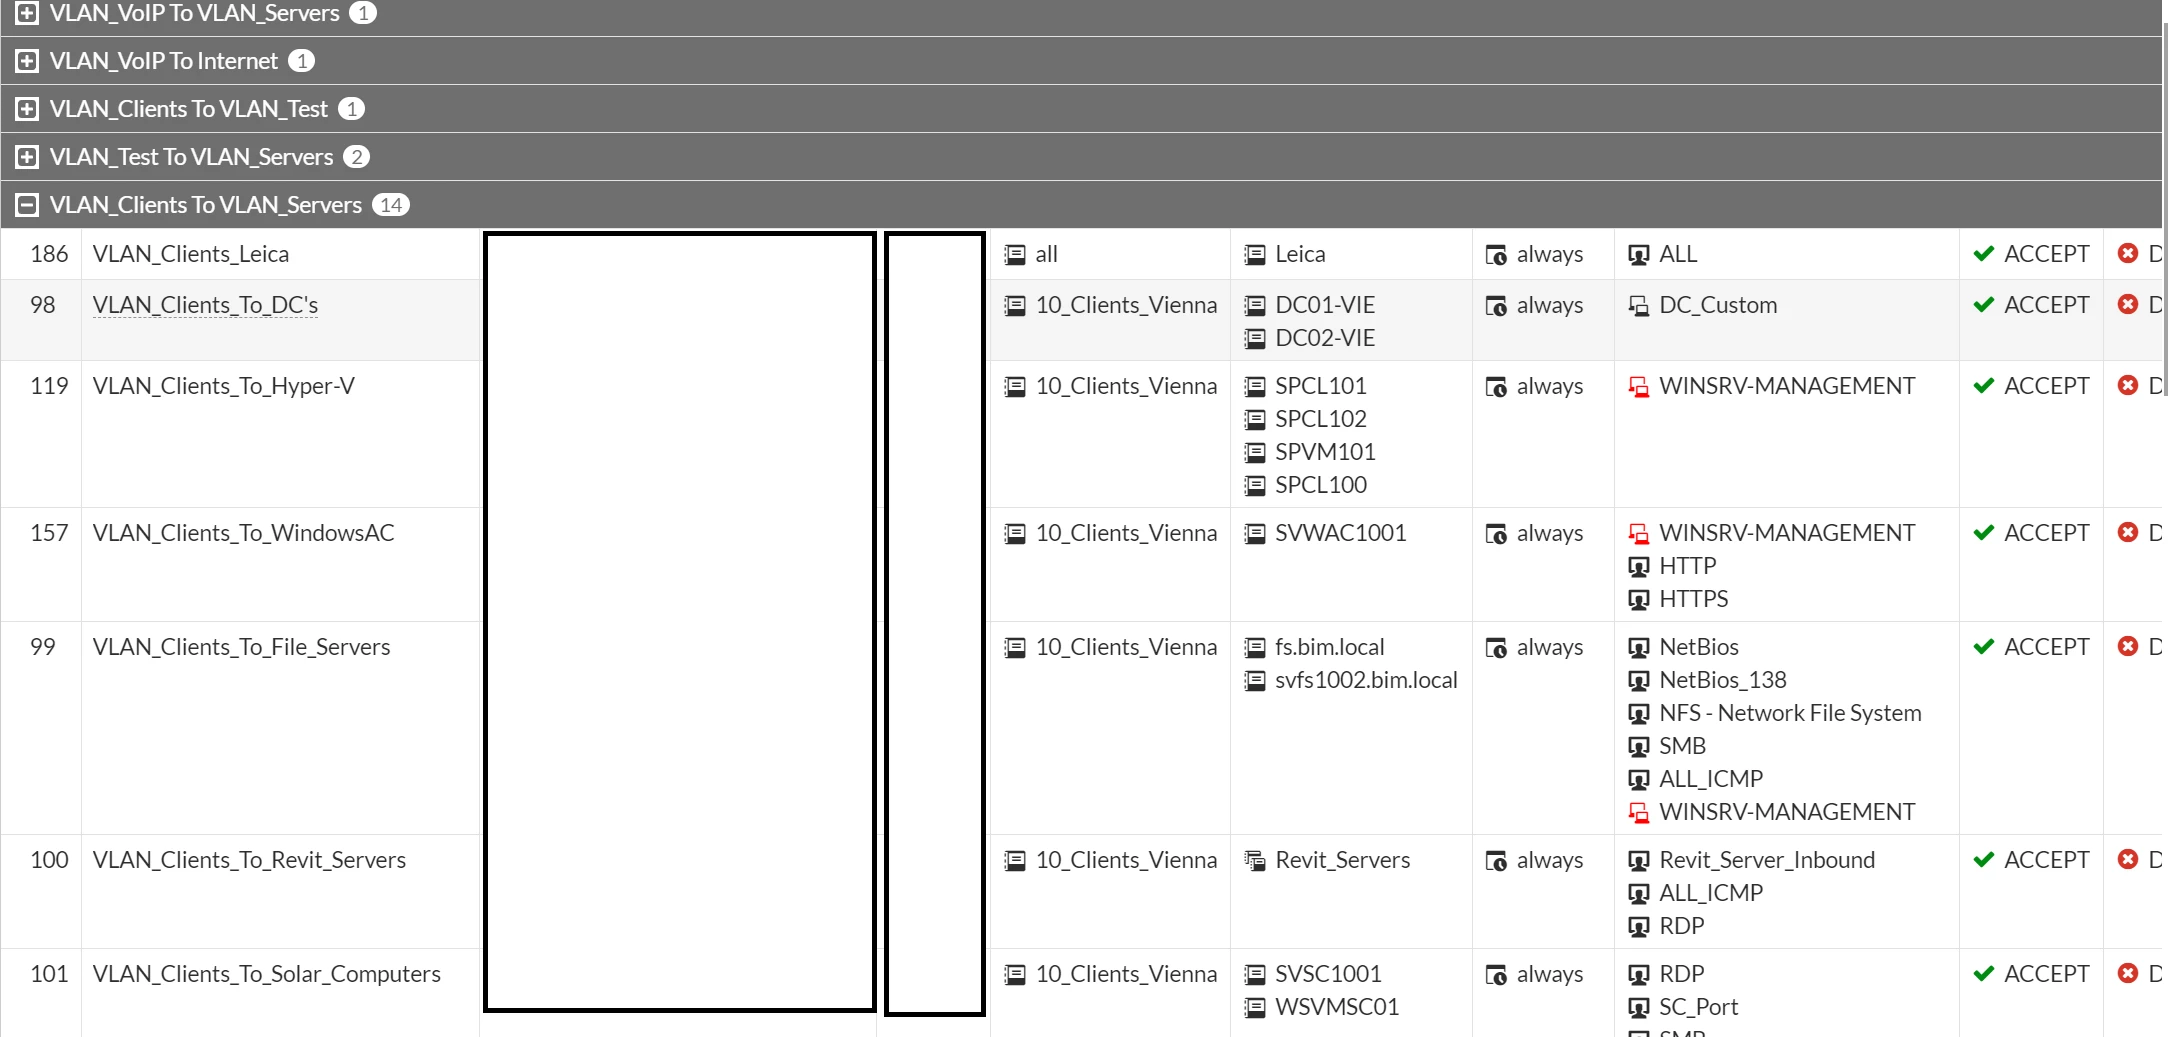
In our infrastructure we have multiple VLANs (clients, printers, servers, voip, etc), and from vlan to vlan I created separate firewall policies.
Example would be:
Sequience grouping: VLAN_CLIENTS to VLAN_SERVERS
1. Clients_To_FileServers - then I restricted from which VLAN to which VLAN, source and destination also, and we also restrict only the needed services.
It's the same principle for every other traffic that is needed.
Now when I look at the Firewall Policies, for somebody else it can be difficult to manage it way trough policies.
How I can make it less complicated but still as secure as it can be.
Example of our policies: