adrianlego
New Member
December 30, 2024
Solved

Fortigate - Bypass host negated vpn-ssl configuration

  • December 30, 2024
  • 1 reply
  • 1545 views

Hi Forum,
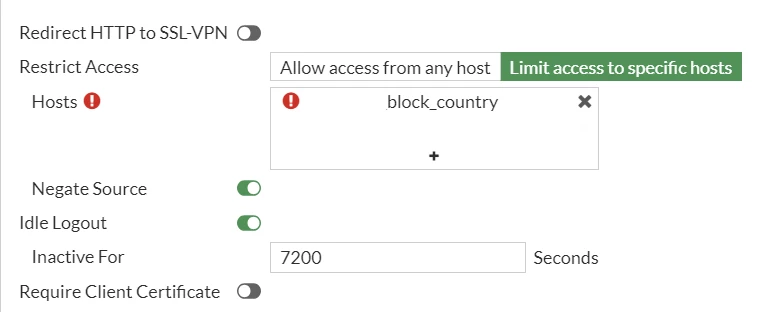
I have configured "host negated" and added a group of countries (block_country) on vpn-ssl settings to avoid ssl failed login attacks but a user need to connect permanently from a country who is on the group mentioned above.


Is there a trick to bypass the current config and allow a remote ip from a country forbidden ?

Thank you for your help.
Regards

2024-12-30 10 35 37.png

Best answer by kaman

Hi adrianlego,

The Restrict Access (aka source-address) configuration can be modified without disrupting existing SSL VPN connections, though only if the modifications continue to allow a given user's source address to connect. For example:

If the Restrict Access option is set to Limit access to specific hosts, and the Hosts include Canada and USA Geography Address objects, then users in Canada and the USA will be able to connect to the SSL VPN.

If Canada is then removed from this config and the changes are applied, any connected Canadian Users will be disconnected (since they have become disallowed).

On the other hand, adding a Mexico Geography Address object to the allowed hosts will not disrupt any existing connections for USA/Canadian VPN users.

NOTE: If the original public source IP is not visible to the FortiGate then the geo-ip location-based restriction will not work. For example, if there is an uplink device that is doing a source NAT on the SSL VPN incoming connections then the geo-ip-based restriction will not work and the access to the SSL VPN gets blocked.

Please refer to the below document for more information:
https://community.fortinet.com/t5/FortiGate/Technical-Tip-Restricting-SSL-VPN-connectivity-from-certain/ta-p/191997

https://community.fortinet.com/t5/FortiGate/Technical-Tip-FortiGate-SSL-VPN-best-practices-guide/ta-p/331260

If you have found a solution, please like and accept it to make it easily accessible to others.


Regards,
Aman

1 reply

kaman
Staff
kamanAnswer
Staff
December 30, 2024

Hi adrianlego,

The Restrict Access (aka source-address) configuration can be modified without disrupting existing SSL VPN connections, though only if the modifications continue to allow a given user's source address to connect. For example:

If the Restrict Access option is set to Limit access to specific hosts, and the Hosts include Canada and USA Geography Address objects, then users in Canada and the USA will be able to connect to the SSL VPN.

If Canada is then removed from this config and the changes are applied, any connected Canadian Users will be disconnected (since they have become disallowed).

On the other hand, adding a Mexico Geography Address object to the allowed hosts will not disrupt any existing connections for USA/Canadian VPN users.

NOTE: If the original public source IP is not visible to the FortiGate then the geo-ip location-based restriction will not work. For example, if there is an uplink device that is doing a source NAT on the SSL VPN incoming connections then the geo-ip-based restriction will not work and the access to the SSL VPN gets blocked.

Please refer to the below document for more information:
https://community.fortinet.com/t5/FortiGate/Technical-Tip-Restricting-SSL-VPN-connectivity-from-certain/ta-p/191997

https://community.fortinet.com/t5/FortiGate/Technical-Tip-FortiGate-SSL-VPN-best-practices-guide/ta-p/331260

If you have found a solution, please like and accept it to make it easily accessible to others.


Regards,
Aman

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.