



Fortigate AWS VPN Site to Site with RUT951 is up, but communication not bidirectional on sites.
I have a site to site vpn mounted with my private subnet (10.0.1.0/24) and Teltonika router RUT951 subnet (192.168.10.0/24) which is connected to internet through dial up (SIM Card Telcel). The site to site is up and successfully running on phase1 and phase2 selectors..... But I canNOT ping or telnet from server in private net to the router RUT951 itself nor any device behind the router.
But I am able to do ping or telnet successfully from router RUT951 to server in private net.
From Fortigate CLI tried to do ping on 192.168.10.1, but no luck.
My guess is the issue should be on the firewall of the router RUT951, but I am new on this so I need help.
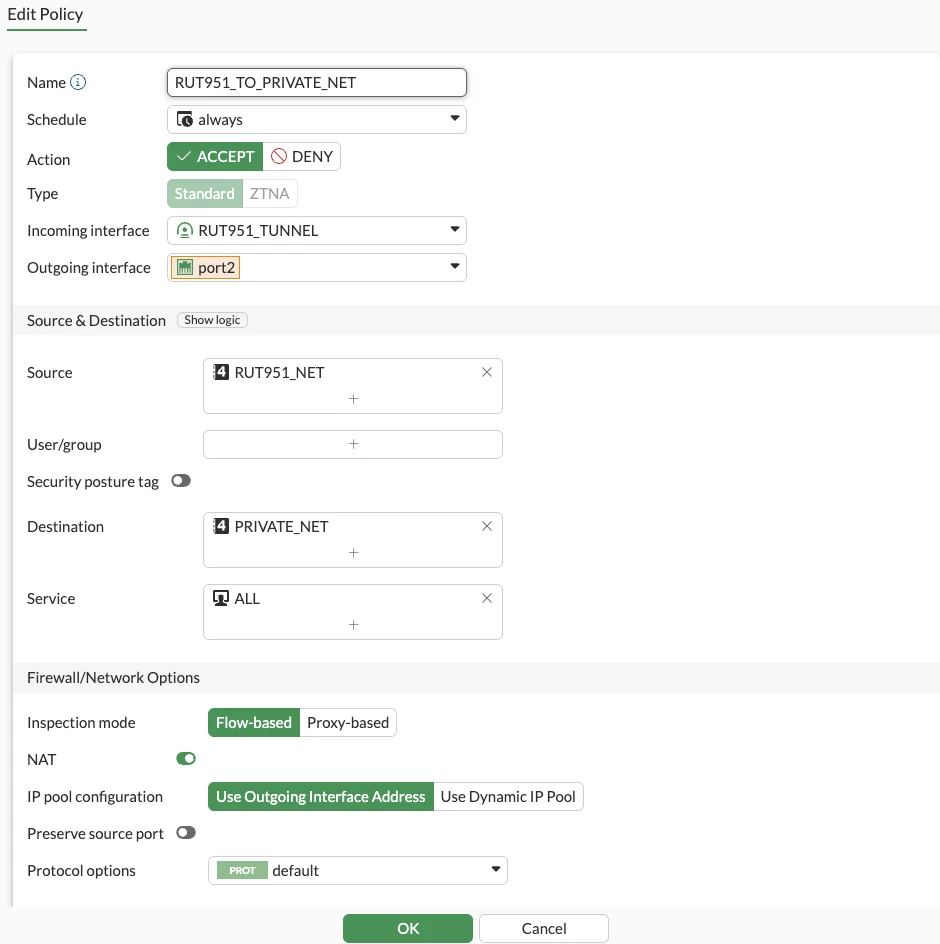
I have both policies allowing all access from RUT951 -> PRIVATE NET and PRIVATE NET -> RUT951 like below:
PRIVATE NET -> RUT951 Policy (This one does not work if doing ping or telnet disabling or enabling NAT, same result).
RUT951 -> PRIVATE NET (This one works perfect i can do ping or telnet)
Static Routes

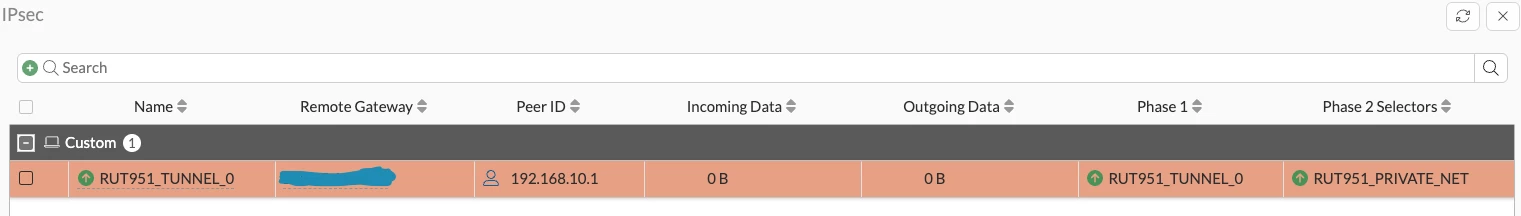
IPSEC TUNNEL SITE TO SITE SUCCESS STATUS.
More context:
Fortigate in a VM in AWS.
Private subnet as 10.0.1.0/24 where private server resides.
Public facing subnet 10.0.0.0/24.
My Teltonika RUT951 router subnet 192.168.10.0/24 (Internet access through SIM Card Telcel, not WAN as such).
RUT951 router ip address 192.168.10.1


