
hboswell
New Member
December 28, 2013
Question

Fortigate 30D - VPN configuration

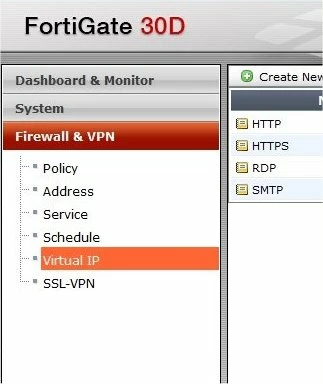
I' ve been looking at all the VPN configuration guides I can find, and for IPSEC they all refer to a VPN menu on the admin tool. But the admin tool for my 30D doesn' t have that - there' s a combined Firewall/VPN menu, and the only VPN choice seems to be SSL. Does the 30D not support IPSEC? Or is there a feature I need to enable? Thanks, Harry
    13 replies

    ede_pfau
    SuperUser
    SuperUser
    December 29, 2013
    Hi, the 30D does indeed support IPsec VPN, but configuration is CLI only. There is no option to enable the GUI pages for this. Seems they are only meant to be used as managed tunnel ends. For the exact syntax, see the ' CLI Reference' for v5 on docs.fortinet.com .
    hboswell
    hboswellAuthor
    New Member
    December 30, 2013
    I keep seeing descriptions and screenshots of this menu - or in the case, it' s on the Fortinet Youtube channel. Has it been removed in 5.0?
    ede_pfau
    SuperUser
    SuperUser
    December 30, 2013
    ??? The screenshot shows a 60C, not a 30D, and SSL-VPN, not IPsec VPN. What exactly is this telling us??? Have you read my previous post? There' s nothing more to it.
    hboswell
    hboswellAuthor
    New Member
    December 30, 2013
    I just keep getting 404-not found for the links on docs.fortinet.com. My point was, I keep seeing this menu referred to, even by the Fortinet support people, who know I' m using a 30D. It shows an IPSEC menu. So I' m a bit confused right now.
    ede_pfau
    SuperUser
    SuperUser
    December 31, 2013
    docs.fortinet.com, second tab " Log & CLI Reference" , 2 more clicks...and you end up here: http://docs-legacy.fortinet.com//fgt/handbook/cli_html/index.html Ain' t that difficult. And yes, at second glance your screenshot shows both IPsec and SSL VPN menus, on a 60C. Again, on the 30D IPsec configuration is CLI only. You need both the ' conf vpn ipsec phase1-interface' and ' conf vpn ipsec phase2-interface' commands, and a policy and a static route. Basics like this are well described in the ' FortiOS Cookbook' , both for GUI and CLI configuration. Just take one example from there and you' re done in 5 minutes.
    Jordan_Thompson_FTNT
    Staff
    Staff
    December 31, 2013
    on the 30D IPsec configuration is CLI only
    This is correct in 5.0 -- IPsec VPN configuration must be set up via the CLI on the 30D.
    Jack_Gerbs
    New Member
    January 27, 2014
    As long as you use the default setting at the main site, here is the CLI commands to build an interface-tunnel config vpn ipsec phase1-interface edit " vpn-1" set interface " wan" set proposal 3des-sha1 aes128-sha1 set remote-gw (address of remote site) set psksecret (enter key) next end config vpn ipsec phase2-interface edit " vpnP2" set phase1name " vpn-1" set proposal 3des-sha1 aes128-sha1 next end Hope this helps, Jack
    Jack_Gerbs
    New Member
    January 27, 2014
    Also forgot to mention that you will need to put policies and routes in to make it all work. The commands on my previous post are for a route based VPN (interface mode). Jack
    farolito
    New Member
    May 26, 2014
    Hi. First many thanks about the info, i was bored trying to set the vpn. I´ve got the tunnel up, but without traffic. Could you tell me how did you set the policies to the vpn? Thanks
    neonbit
    New Member
    June 11, 2014
    Hi guys, As an FYI, the 30Ds actually support policy based VPNs via the GUI, it' s only the interface based VPNs that need to be configured via the CLI. Of course if you need to reconfigure the phase1/2 after you' ve created them in the policy you' ll need to do it via the CLI.
    farolito
    New Member
    June 16, 2014
    Many thanks, the VPN rules!
    Mordak
    New Member
    August 11, 2014
    I was surprised to see the FortiWifi30D with the option to make a IPSEC VPN from the new policy window. We were buying FG40C' s and they had the option then started buying the FG30D' s as they were cheaper. A FG30D (the non wifi version) running 5.0.7 definitely does not have the GUI ability to make an IPSEC policy.
    Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
    Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
    Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT


