FortiGate 100E – SSL inspection causes NET::ERR_CERT_COMMON_NAME_INVALID on HTTPS sites (e.g. Google
Hi experts,
I am experiencing a certificate warning when users browse HTTPS websites such as Google.
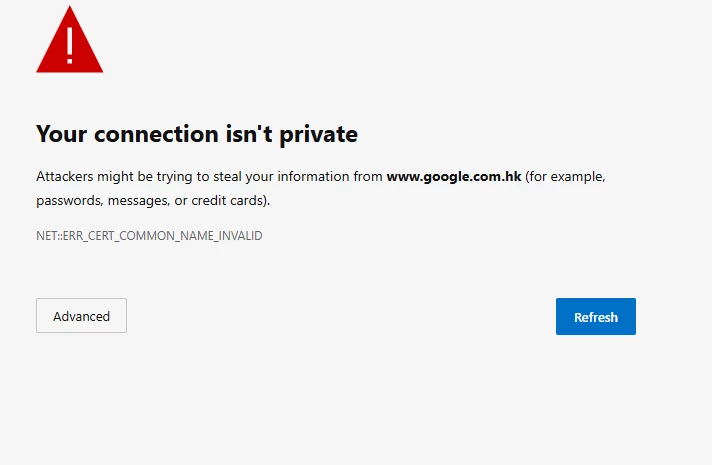
The browser shows:
Your connection isn’t private
NET::ERR_CERT_COMMON_NAME_INVALID
Device Details:
Model: FortiGate 100E
Firmware: v6.2.16 build1392 (GA)
SSL Inspection Mode: Deep inspection (certificate inspection using Fortinet_CA_SSL)
Web Filter: Enabled
FortiGate certificate is already imported into client trusted root store
FortiGate DNS cache has been flushed (diagnose test application dnsproxy 8)
Tested browsers: Chrome, Edge (same issue)
Troubleshooting Done:
Verified system time on FortiGate and client
Flushed DNS cache on FortiGate and PC
Imported Fortinet_CA_SSL into Windows and Chrome store
Checked if FortiGate is presenting a mismatched CN (shows FortiGate CA instead of Google CN)
Question:
Is this a known issue with v6.2.16 build1392?
Any official Fortinet patch or workaround to fix SSL deep inspection mismatch?