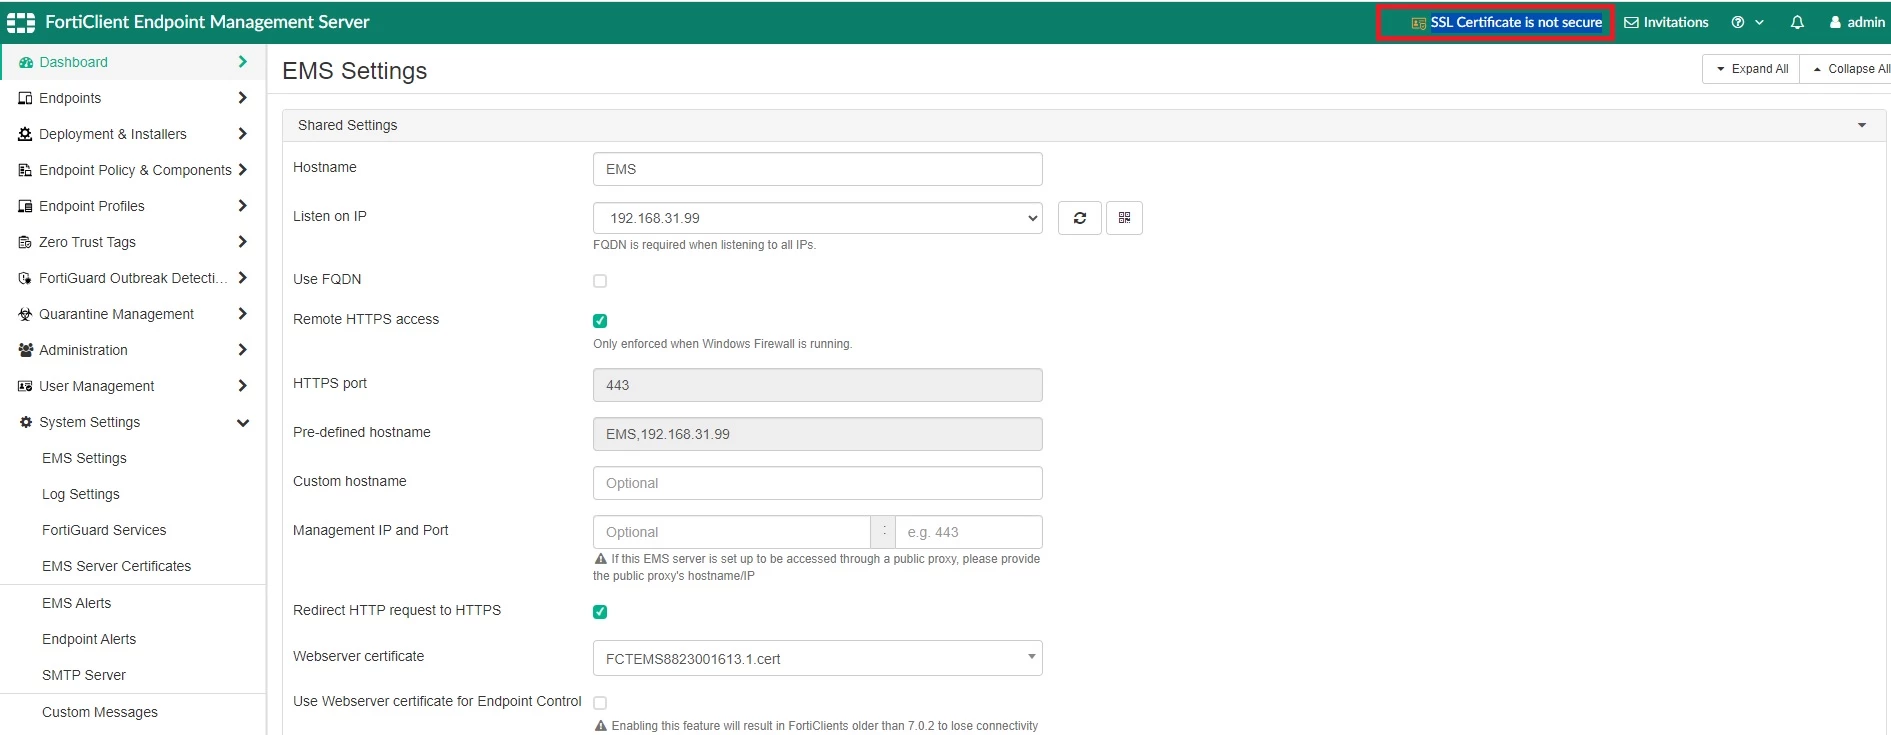
Many thanks for your kind response. On the EMS server, there are two certificates: one for the web server and the second for the endpoint certificate. I have built a local certificate using OpenSSL and used it for the endpoint control certificate. I have a problem with the webserver certificate.
First certificate built-in certificate. Because of that, this can't be compatible with ems fqdn.
You need to configure a new fqdn to FortiClient EMS on the Settings page. After that, you need to upload a certificate compatible with this fqdn. Or you can use lets encrypt for this operation.