

SeVe
Visitor III
October 28, 2022
Solved

FortiClient update deployment only for already installed clients

  • October 28, 2022
  • 3 replies
  • 2600 views

Hello everyone,


I'm just making my first steps with the FortiClient EMS. I have already installed some clients on domain PCs and would now like to update them.

But...

1. I can assign a deployment package only to a OU. But I don't want to supply all PCs in this OU with the forticlient. I only want to update not to install.

2. If I don't use the AD connection, but "only" groups, then I can deploy to the group only, but I can no longer distribute the client policy dynamically per user group.


Background: There are about 1000 PCs in different OUs and the FortiClient should only be used for SSLVPN on 50 PCs, which is why I don't want to distribute the installation to all PCs.


Is there a best practice how to do it?

How can i keep the installed clients up to date?


THX

Sebastian


Best answer by btan

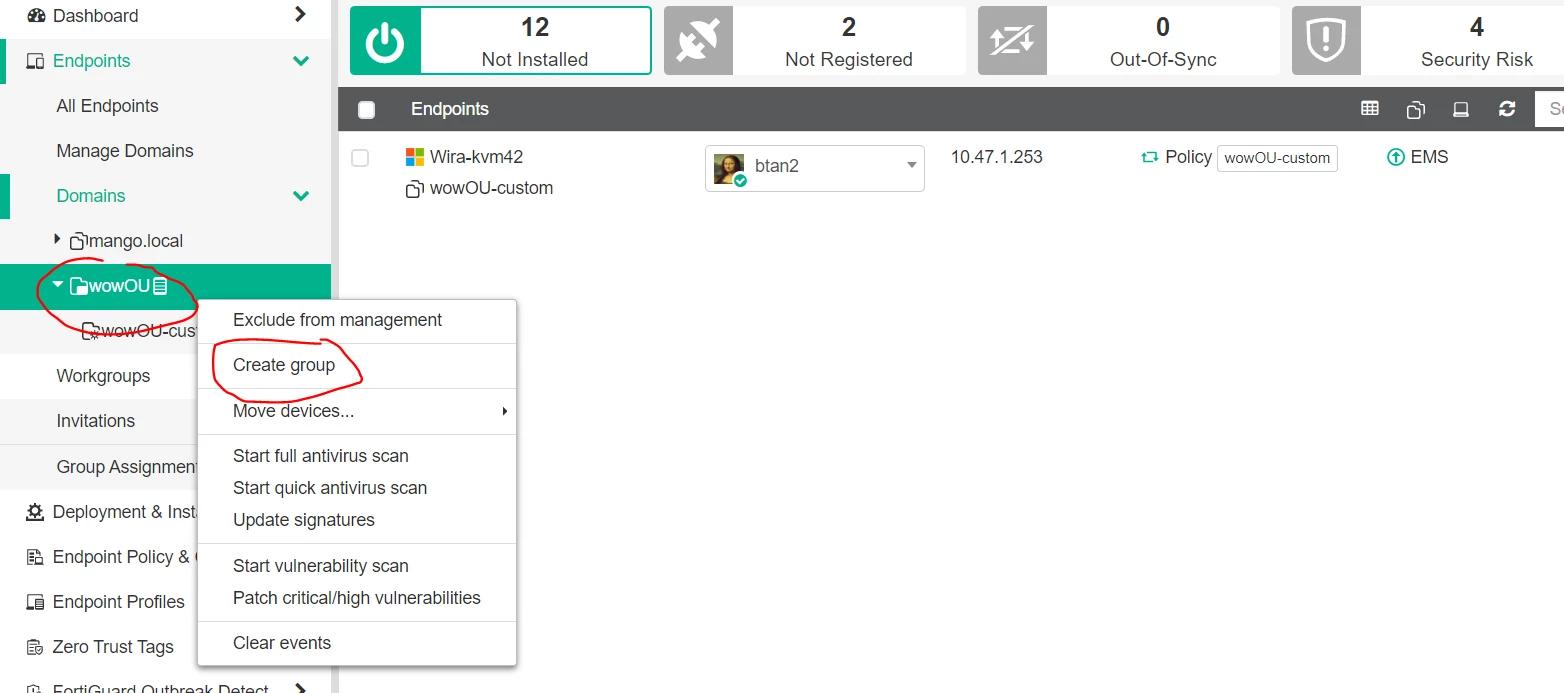
create-custom-group.PNG


1. Create a custom group under your desired OU

2. Map the same endpoint policy to the new custom group (so that endpoints in the new custom group get the same profile)

3. Move your desired PC to upgrade FCT to the new custom group

4. Create a FCT upgrade deployment package to the new custom group

5. The upgrade process will happen for PCs that are in new custom group only

6. After upgrade is completed, you may move back your desired PC back to their original OU group.


This may be a suitable solution if you have imported 1000+ AD domain joined endpoints, but only need to manage 50+ endpoints.

3 replies

btan
Staff & Editor
btanAnswer
Staff & Editor
October 29, 2022

create-custom-group.PNG


1. Create a custom group under your desired OU

2. Map the same endpoint policy to the new custom group (so that endpoints in the new custom group get the same profile)

3. Move your desired PC to upgrade FCT to the new custom group

4. Create a FCT upgrade deployment package to the new custom group

5. The upgrade process will happen for PCs that are in new custom group only

6. After upgrade is completed, you may move back your desired PC back to their original OU group.


This may be a suitable solution if you have imported 1000+ AD domain joined endpoints, but only need to manage 50+ endpoints.

SeVe
SeVeAuthor
Visitor III
October 29, 2022

Hi Bon,

thank you very much. This is exacly what i'm looking for.


Regards,

Sebastian

btan
Staff & Editor
Staff & Editor
November 1, 2022

Most welcome Sebastian.

Consider mark it as "solution" if it worked for you, so everyone can refer to it if have similar query.

Cheers!

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!

