



Solved
FortiClient Remote Access VPN – Automatic Failover Without EMS
Hello Fortinet Community,
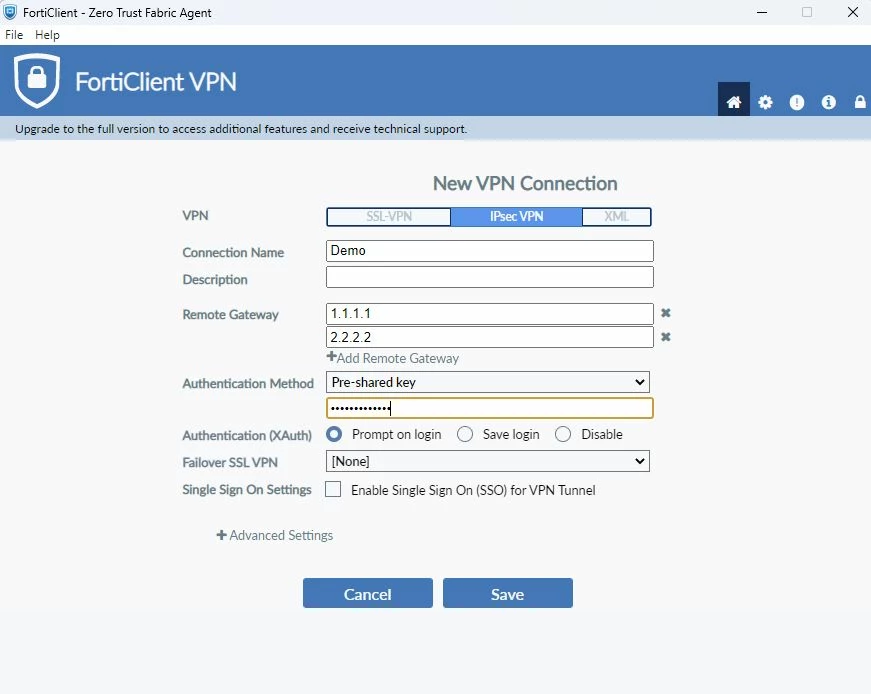
I’ve configured two identical IPsec remote access VPNs on my FortiGate—each mapped to a different WAN interface for redundancy purposes. On FortiClient, I’ve added both VPN gateways. The issue I'm facing is that when I disable WAN1, FortiClient does not automatically failover to the second gateway. Instead, I have to manually reconnect by clicking "Connect" to establish a session with the secondary gateway.
I'd like to know is it possible to automate this failover process, so users experience minimal disruption? Is it possible to achieve automatic remote access VPN failover in FortiClient without using EMS?
Thank you!

