

PamelaP
New Member
September 10, 2024
Question

Forticlient 7.4.0142 will not display login screen on iPad iOS 15.8

  • September 10, 2024
  • 30 replies
  • 14087 views

I have a fleet of managed iPads that are older Air2s running iOS 15.8, and the recent update not only deleted all previous VPN configurations, it also no longer displays the login screen with the new configs. All of my other iPads are able to connect, it's just these older ones that cannot. It appears that it's trying to use SSO, even though that is deselected in the config. When they try to connect, this window appears
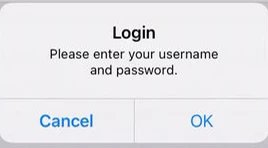
PamelaP_0-1725982426201.png

But tapping on OK results in this window:
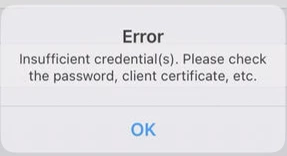
PamelaP_1-1725982478212.png

They are never offered the regular login window to enter their username and password.

I have submitted a ticket but have yet to get a response, so thought I'd ask here ot see if anyone else is experiencing the same.


30 replies

Anthony_E
Staff
Staff
September 13, 2024

Hello Pamela,


Thank you for using the Community Forum. I will seek to get you an answer or help. We will reply to this thread with an update as soon as possible.


Thanks,

Best Regards
NicholasReed
New Member
September 14, 2024

I am just posting so I can keep track of this thread.

Anthony_E
Staff
Staff
September 16, 2024

Hello Pamela,


We are still looking for someone to help you.

We will come back to you ASAP.


Regards,

Best Regards
Anthony_E
Staff
Staff
September 19, 2024

Hello @btan@Anil_Solakoglu,


Do you maybe have an answer for this request?


Thanks a lot in advance.


Regards,

Best Regards
btan
Staff & Editor
Staff & Editor
September 19, 2024

Hi @PamelaP


I personally did not see this issue before.
In affected iPad, in the VPN tab, you can click on 'Edit' at the top right, click again on your VPN tunnel, it should bring you to a new window. In that screen, do you see 'SSO' is still being toggled on?

Other workarounds that may help:

1. Clone the endpoint profile in EMS, and assign the cloned profile to this ipad.

2. Or simply assign this ipad to another profile/policy, let it sync to EMS to get the profile, then switch it back to the intended profile.
3. Deregister and rejoin back to EMS

4. Uninstall and reinstall iOS FCT

drGazza
New Member
September 30, 2024

have any suggest to resolve this issue?

I confirm that with iphone ios 15.8.3 and vpnclient 7.4.1 , I have the same problem

PamelaP
PamelaPAuthor
New Member
September 30, 2024

I opened a support ticket with Fortinet the same day I posted this, and a week later they finally acknowledge that there was a bug.in 7.4.0. They then said they would test and send out a new release that would fix it. Thus, 7.4.1 released last week, but unfortunately, it did not fix this particular issue. The suggestions upstream from btan were all fixes I tried previous to opening the support ticket, and none of them worked - so don't bother with any of those. We have tried to provide feedback on the support ticket (it's still open) but the portal was unavailable this past Friday 9/27/24. We will try again today.


ETA - SSO is not enabled, but it acts as though it is caching credentials (for lack of a better term) regardless. I can't tell where it's picking them up from though, as we use MFA for their AD/Entra accounts, the iPads are enrolled in InTune, and my users do not have AppleID's on this particular set of managed iPads. The credential-caching is what they need to fix.

btan
Staff & Editor
Staff & Editor
October 2, 2024

Hi @PamelaP , thank you for the info.


May I know the Internal Case ID or bugID if this is acknowledged as a bug by your TAC?
Thank you.

PamelaP
PamelaPAuthor
New Member
October 2, 2024

Hi Bon,


The ticket number is 9884511. It is under our network manager's name; he is the one that has the account. I'm just dealing with the outfall.

funkylicious
SuperUser
SuperUser
October 2, 2024

From my experience so far with FCT 7.4.0 it's a little buggy, so I decided to revert back to 7.2.X version at least for MacOS and Windows devices, I would suggest you trying to do the same.

"jack of all trades, master of none"
PamelaP
PamelaPAuthor
New Member
October 2, 2024

Unfortunately, this is on an iPad and pushed to our devices via the App Store - no option to revert back exists that I'm aware of.

drGazza
New Member
October 2, 2024

unfortunately not possible on mobile device, or at least I don't know how to do it

We hope for a solution via Appstore

PamelaP
PamelaPAuthor
New Member
October 2, 2024

Did it recently quit working for you too? We have been using Forticlient for remote connectivity for years and up until they pushed version 7.4.0, users logged in with their AD credentials (we have it linked) without issue. Sadly, the new version (7.4.1) that was supposed to fix it, isn't working either. On newer iOS versions it will allow you to log in once, then it caches those credentials and just waits for MFA to be approved. We don't want that either. I had one user put in the wrong password, it cached that, and I had to wipe his iPad back to factory to get FortiClient to ask for a login again. That is not acceptable, we should be able to delete those cached credentials any time there is a problem. It's really going to screw users when they have mandatory password changes, and they aren't able to enter the new one. This caching action is happening even though SSO is turned off and Save Password is not selected.

drGazza
New Member
October 10, 2024

any news for this issue? 

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!