stulluk
New Member
October 17, 2024
Question

forticlient 7.4.0 - unable to modify settings

I am running Forticlient 7.4.0.1636 under Ubuntu 22.04 to connect my company's VPN.

My problem: In the settings menu, if I unlock it , change some settings below, and then connect to VPN, my changes are not saved, and they return back to original values as below:
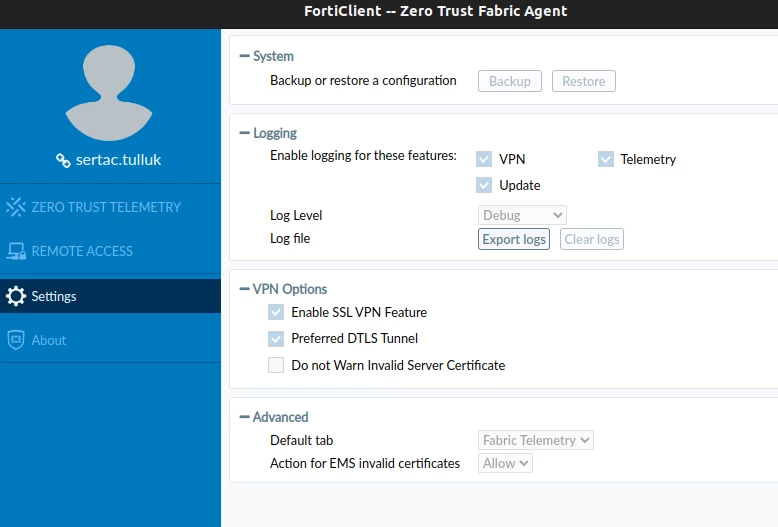
 

2024-10-17-08-39-36.png


I want to change these settings because :

1) Logging causes constant pressure on the disk I/O

2) I have to click multiple popups to accept invalid server certificate and unnecessary confirmation dialogs everytime I connect.

See below for screenshots:
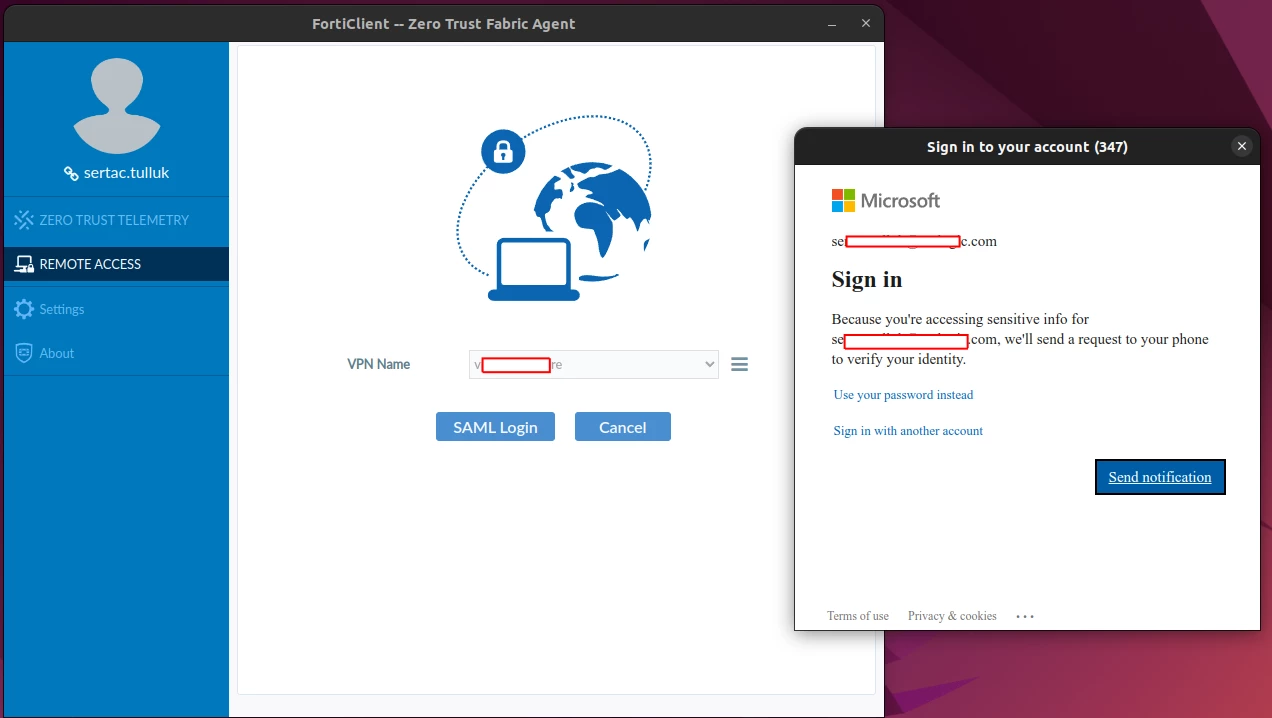
2024-10-17-08-42-35.png


2024-10-17-08-42-57.png

2024-10-17-08-43-10.png

How can I modify the settings so that I can reduce number of steps when connecting to VPN ?

13 replies

AEK
SuperUser
SuperUser
October 17, 2024

I know there are some things on FCT that cannot be done without EMS, but I'm not sure for this one.

I think you should try with FCT VPN (the free version). Try with 7.4.0 and in case the issue persists you may try with 7.2.5 or even 7.0.13.

AEK
hokumto1
New Member
October 17, 2024

Same issue here indeed. Sometimes not connecting, or after 5 or 6 times…. Running Windows 10 and 11. Tried version 7.0 7.2 and also 7.4. But same issue occurs random…

At this moment again a support ticket open… but im guessing not much Will come out! So if someone has a solution ….

stulluk
stullukAuthor
New Member
October 17, 2024

@AEK 
This is totally not related to different version as I already tried older versions before.
This is basically a bug, where the application does not PERSIST the settings.

Where should we look for official support for this?

AEK
SuperUser
SuperUser
October 17, 2024

FortiClient without EMS is not supported, and FortiClient VPN (free version) is also not supported.

As mentioned try to use FortiClient VPN instead of FortiClient, because FortiClient VPN can store the config without the need of EMS.

AEK
bronwod2
New Member
October 17, 2024

As far as VPN clients go, it's quite slow, clunky, and lots of odd issues that are virtually always resolved with a re-install. We're aiming to replace it within the next six months with something faster and more secure (likely something that uses the WireGuard protocol).

stulluk
stullukAuthor
New Member
October 17, 2024

@AEK 

Let me understand you more clearly:

1) Both "Forticlient VPN" and "Forticlient EMS" are not supported but you are still suggesting to use "Forticlient VPN" because it allows to store the configuration ?

2) Why "Forticlient EMS" is not supported ? Isn't it a paid product ? What does it mean "not supported" ?

3) "Forticlient VPN" -> Do you mean the file here: https://links.fortinet.com/forticlient/deb/vpnagent  Can you open this link ? (I can't because it says can not resolve DNS ? )


Thanks for your kindness & support.

AEK
SuperUser
SuperUser
October 17, 2024

Hi

I mean "FortiClient" agent without "EMS server" is not supported. When you have EMS server it means you have license, and in that case your FortiClient agents are supported.

If you use FortiClient without central management (EMS) then you will not get any support.

FortiClient VPN (the free version which is also not supported) can be downloaded here:

https://www.fortinet.com/support/product-downloads#vpn

Yes I can open the link that you provided above, and it is FortiClient VPN for Debian.

AEK
stulluk
stullukAuthor
New Member
October 21, 2024

@AEK

OK, now we are clear, I am using Forticlient WITH and EMS server from my company.

2024-10-22-02-03-53.png


So it SHOULD be supported.
And now back to my original question: What I need to do to let this "Forticlient with EMS" version to PERSIST my settings ? 

stulluk
stullukAuthor
New Member
October 23, 2024

@AEK any response?

AEK
SuperUser
SuperUser
October 24, 2024

Hi Sertac


Regarding certificate warning, I tried on a FCT 7.4.0 (with EMS) and I confirm it asks to validate it every time I connect. I guess this is for security reason.

Actually for security it is recommended to use a trusted certificate, otherwise there is a risk of MITM attack. Or even better, use IPsec instead of SSL-VPN.


Regarding SSL-VPN logging, go the EMS, Endpoint Profiles > System Setting, the edit the profile you are using, under "Log" section you can disable VPN logs.

AEK
Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT